

Identity infrastructure for modern compliance
space
Joined September 2020
- Tweets2.5K
- Following921
- Followers22.2K
- Likes4.5K




Pinned Tweet
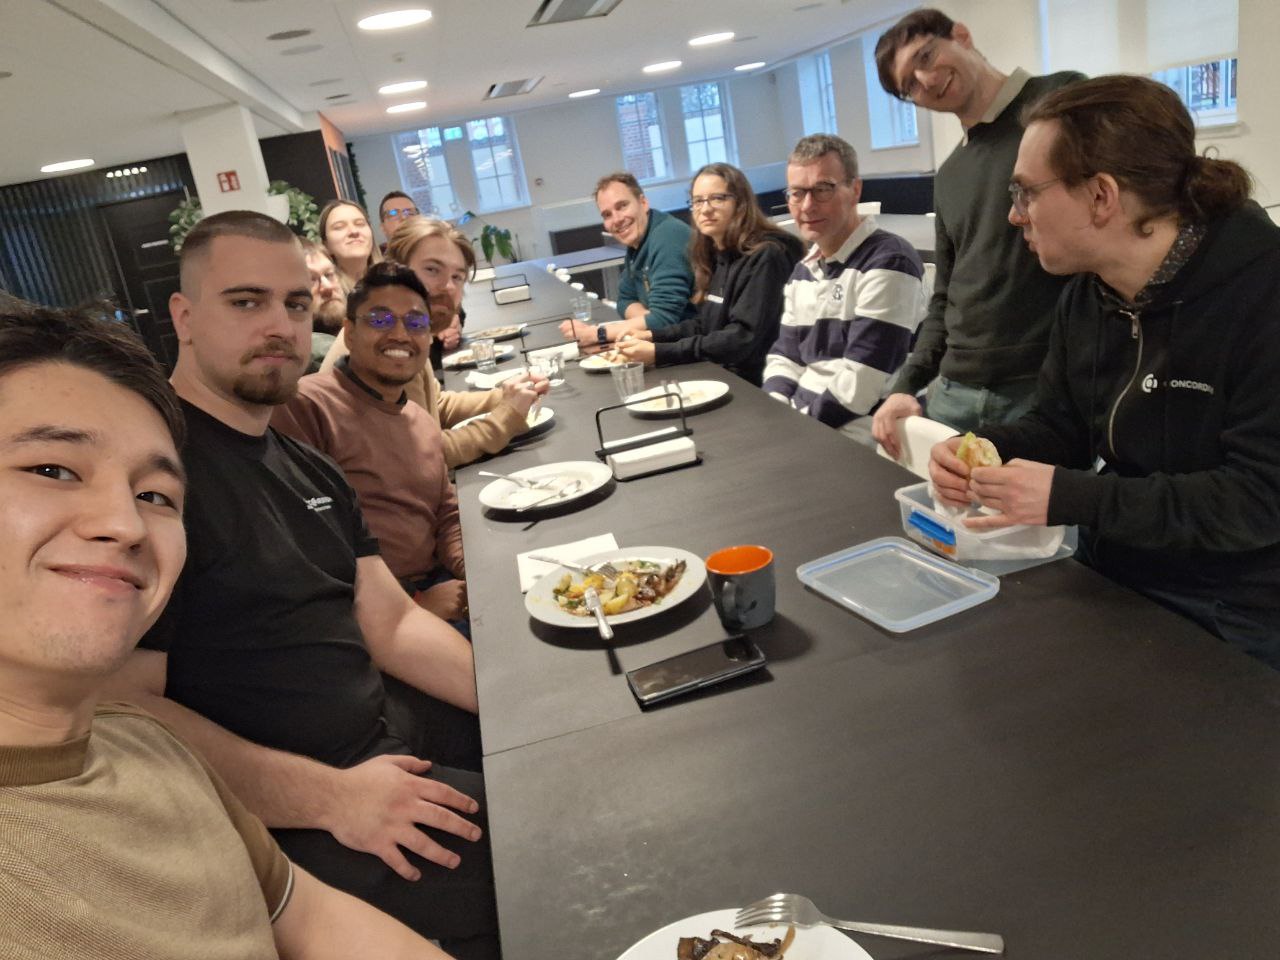
Just wrapped an in-person roadmap session at Concordium HQ 🇩🇰
Great meeting the @Concordium core team with our co-founder Vishwas Anand (CTO) & Kash Sangh of @creativeideazuk to align on the future of identity, compliance, & trust in regulated Web3.
Excited for what is ahead🚀

ALT #Hypersign #Concordium #Web3Infrastructure #DigitalIdentity #Compliance #TrustLayer #OnchainKYC

Every KYC provider is a potential point of failure if sensitive identity data is stored and exposed.
Less PII stored means less data at risk.
Verify users, not store their identities.
That's the shift the KYC industry needs.
#KYC #DataPrivacy #RegTech

4 data leaks reported today:
1. Coinbase's vendor Amplitude exposed some users’ contact data (funds unaffected).
2. Bithumb (Korea) had user data leaks.
In TradFi, two securities firms in Korea leaked data:
3. Mirae Asset
4. Daishin Securities
You can't prevent a leak, but you can protect yourself.
Leaked exchange data (names, emails, phone numbers, addresses, ID documents, transaction history) is mostly used for phishing, SIM swapping, and social engineering.
Reduce info you share
- Use a unique email alias for each exchange (SimpleLogin, Apple Hide My Email, etc). A leak then can't be linked to your other accounts, and you can spot which service leaked.
- Share only what's required. Don't add optional profile details.
- Use a dedicated phone number (a VoIP or secondary SIM) for exchange accounts if you can, since leaked numbers are the main route to SIM swaps.
Lock down the account
- Use a unique, long password from a password manager.
- Turn on hardware security keys (YubiKey) or passkeys, or at least an authenticator app.
- Avoid SMS 2FA.
- Enable withdrawal address whitelisting and a withdrawal time lock if the exchange offers them.
- Set up an anti-phishing code, which puts a code you choose in every legitimate email from the exchange.
- Review active sessions and API keys regularly. Delete any API keys you don't use.
- Restrict API keys to withdraw-disabled and IP-whitelisted.
Defend against
- SIM swapping: Ask your carrier to add a port-out PIN or number lock.
- Phishing and impersonation: Assume anyone who contacts you about your account, "security issues," or "refund recovery" is a scammer, even if they know your name, balance, or recent trades.
- Exchange support staff don't ask for your password, 2FA codes, or seed phrase.
- Never click links in emails or texts. Go to the site yourself.
- "Wrench attacks": Leaked addresses plus holdings data have led to real-world extortion and robberies. Don't publicize your holdings, and keep large balances out of anything tied to your home address if you can.
If a breach is announced
1. Change the exchange password and any other account that reused it.
2. Check haveibeenpwned.com for your email address.
3. Revoke API keys and active sessions.
4. Review recent withdrawals and security settings.
5. Watch for phishing emails and texts that reference the breach, because scammers move fast after one.
Stay SAFU! 🙏

36 hours to go, Kolkata!
A cup of chai, great conversations, and discussion on Privacy & Digital Trust.
Who's joining us? Venue details coming soon.
luma.com/i3n7ibua
#Privacy #DigitalTrust #Kolkata

Hypersign🆔 | #payfi #trusttech retweeted

Kolkata folks, let’s grab a cup of chai and have a conversation about Privacy & Digital Trust.
Would love to connect with people passionate about building a more private and trustworthy digital world. Who’s in?
luma.com/i3n7ibua
@hypersignID
📣 We're proud to be a Community Partner of the TUM Blockchain Conference 26!
Oct 29 to 31 in Munich: talks, a Digital Assets Day by @bundesblock and a 30h Hackathon. Hosted by @tbc_munich.
See you there → conference26.tum-blockchain.… #TUMBlockchainConference26

Hypersign🆔 | #payfi #trusttech retweeted
It was great to catchup with Member of Parliament Sri Gopal Ji from Darbhanga and share about @hypersignID

Hypersign🆔 | #payfi #trusttech retweeted
60 seconds to explain what you’ve been building for 5 years.
I got the chance to pitch @hypersignID in 60 seconds at an event by @AntlerIndia × INKLE in HSR, Bangalore.


Congratulations to @mperpsxyz on the successful launch on @CantonNetwork !
We’re proud to be their KYC partner and excited to support their journey toward secure, compliant, and trusted growth.

Compliance stacks keep growing.
Every new regulation adds another tool.
KYC. AML. Sanctions. Risk scoring.
It does not have to be this way:
Verify identity once
Reuse verification everywhere
Hypersign makes identity reusable.
Explore how → hypersign.id
🤖 Made with AI

ALT #DigitalIdentity #Compliance #KYC #AML #ReusableIdentity #Web3Infrastructure #TrustInfrastructure #DecentralizedIdentity #Hypersign
KYC alone is not sufficient for Web3 compliance.
Modern platforms must verify:
Users. Businesses. Transactions.
That means KYC • KYB • KYT.
Explore how Hypersign supports modern compliance infrastructure.
#Web3 #KYC #Compliance
KYC is not broken.
It is built wrong.
Most solutions optimize for compliance.
Very few optimize for users.
That is why friction feels normal
and drop-offs are ignored.
It should not be this way.
Rethink KYC. Build it right with Hypersign.
What do AI faces, stolen selfies, and synthetic identities have in common?
They are reshaping identity fraud.
Swipe to see how attackers are bypassing verification systems. 👇
1 billion identity records exposed.
The @id_merit breach reportedly involved real KYC data. National IDs. Addresses.
You can change a password. You cannot change your national ID.
Maybe it is time to rethink how compliance data is stored.
Read more: hypersign.id/blogs/tpost/gm9…

ALT #OnchainKYC #CryptoKYC #Web3Compliance #BlockchainIdentity
Same user.
Same identity.
Why the same KYC again?
With Hypersign
Verify once. Use everywhere.
Reusable. Privacy-first. Regulation-ready.
Building in Web3? Let us connect. linktr.ee/hypersign

ALT #OnchainKYC #Web3Compliance #ReusableCredentials #BlockchainIdentity #CryptoRegulations #Hypersign
User verification is changing.
Businesses are online, on-chain, & global by default.
Communities move capital before formal structures exist.
Yet most KYC systems remain rigid, data-heavy, & built for the old internet.
As privacy regulations tighten, verification has to evolve.
Hypersign🆔 | #payfi #trusttech retweeted
1/
Reading Vitalik’s thoughts on L2s really hit home for me.
We built Hypersign on Cosmos SDK early on because interoperability just worked.
Chains followed the SDK. Standards were shared. Things moved together.

There have recently been some discussions on the ongoing role of L2s in the Ethereum ecosystem, especially in the face of two facts:
* L2s' progress to stage 2 (and, secondarily, on interop) has been far slower and more difficult than originally expected
* L1 itself is scaling, fees are very low, and gaslimits are projected to increase greatly in 2026
Both of these facts, for their own separate reasons, mean that the original vision of L2s and their role in Ethereum no longer makes sense, and we need a new path.
First, let us recap the original vision. Ethereum needs to scale. The definition of "Ethereum scaling" is the existence of large quantities of block space that is backed by the full faith and credit of Ethereum - that is, block space where, if you do things (including with ETH) inside that block space, your activities are guaranteed to be valid, uncensored, unreverted, untouched, as long as Ethereum itself functions. If you create a 10000 TPS EVM where its connection to L1 is mediated by a multisig bridge, then you are not scaling Ethereum.
This vision no longer makes sense. L1 does not need L2s to be "branded shards", because L1 is itself scaling. And L2s are not able or willing to satisfy the properties that a true "branded shard" would require. I've even seen at least one explicitly saying that they may never want to go beyond stage 1, not just for technical reasons around ZK-EVM safety, but also because their customers' regulatory needs require them to have ultimate control. This may be doing the right thing for your customers. But it should be obvious that if you are doing this, then you are not "scaling Ethereum" in the sense meant by the rollup-centric roadmap. But that's fine! it's fine because Ethereum itself is now scaling directly on L1, with large planned increases to its gas limit this year and the years ahead.
We should stop thinking about L2s as literally being "branded shards" of Ethereum, with the social status and responsibilities that this entails. Instead, we can think of L2s as being a full spectrum, which includes both chains backed by the full faith and credit of Ethereum with various unique properties (eg. not just EVM), as well as a whole array of options at different levels of connection to Ethereum, that each person (or bot) is free to care about or not care about depending on their needs.
What would I do today if I were an L2?
* Identify a value add other than "scaling". Examples: (i) non-EVM specialized features/VMs around privacy, (ii) efficiency specialized around a particular application, (iii) truly extreme levels of scaling that even a greatly expanded L1 will not do, (iv) a totally different design for non-financial applications, eg. social, identity, AI, (v) ultra-low-latency and other sequencing properties, (vi) maybe built-in oracles or decentralized dispute resolution or other "non-computationally-verifiable" features
* Be stage 1 at the minimum (otherwise you really are just a separate L1 with a bridge, and you should just call yourself that) if you're doing things with ETH or other ethereum-issued assets
* Support maximum interoperability with Ethereum, though this will differ for each one (eg. what if you're not EVM, or even not financial?)
From Ethereum's side, over the past few months I've become more convinced of the value of the native rollup precompile, particuarly once we have enshrined ZK-EVM proofs that we need anyway to scale L1. This is a precompile that verifies a ZK-EVM proof, and it's "part of Ethereum", so (i) it auto-upgrades along with Ethereum, and (ii) if the precompile has a bug, Ethereum will hard-fork to fix the bug.
The native rollup precompile would make full, security-council-free, EVM verification accessible. We should spend much more time working out how to design it in such a way that if your L2 is "EVM plus other stuff", then the native rollup precompile would verify the EVM, and you only have to bring your own prover for the "other stuff" (eg. Stylus). This might involve a canonical way of exposing a lookup table between contract call inputs and outputs, and letting you provide your own values to the lookup table (that you would prove separately).
This would make it easy to have safe, strong, trustless interoperability with Ethereum. It also enables synchronous composability (see: ethresear.ch/t/combining-pre… and ethresear.ch/t/synchronous-c… ). And from there, it's each L2's choice exactly what they want to build. Don't just "extend L1", figure out something new to add.
This of course means that some will add things that are trust-dependent, or backdoored, or otherwise insecure; this is unavoidable in a permissionless ecosystem where developers have freedom. Our job should make to make it clear to users what guarantees they have, and to build up the strongest Ethereum that we can.

🧵 WhatsApp, India & the Global Privacy Double Standard
1/
🇮🇳 India is asking a hard but fair question:
If WhatsApp protects EU users by design,
why should Indian users accept weaker privacy safeguards?
Privacy can’t be geography-based.
This quoted post is unavailable.
10/
This is why we’re building Hypersign.
Identity that’s:
• portable
• interoperable
• verifiable without data hoarding
Trust without surveillance.