



Ian Hellen retweeted

MSTICPy 2.11.0 released
This minor release includes:
- Better handling of large/split queries for MS Sentinel
- Updated support for installing MSTICPy in a Conda environment
- Updates for future pandas support
github.com/microsoft/msticpy…

Ian Hellen retweeted

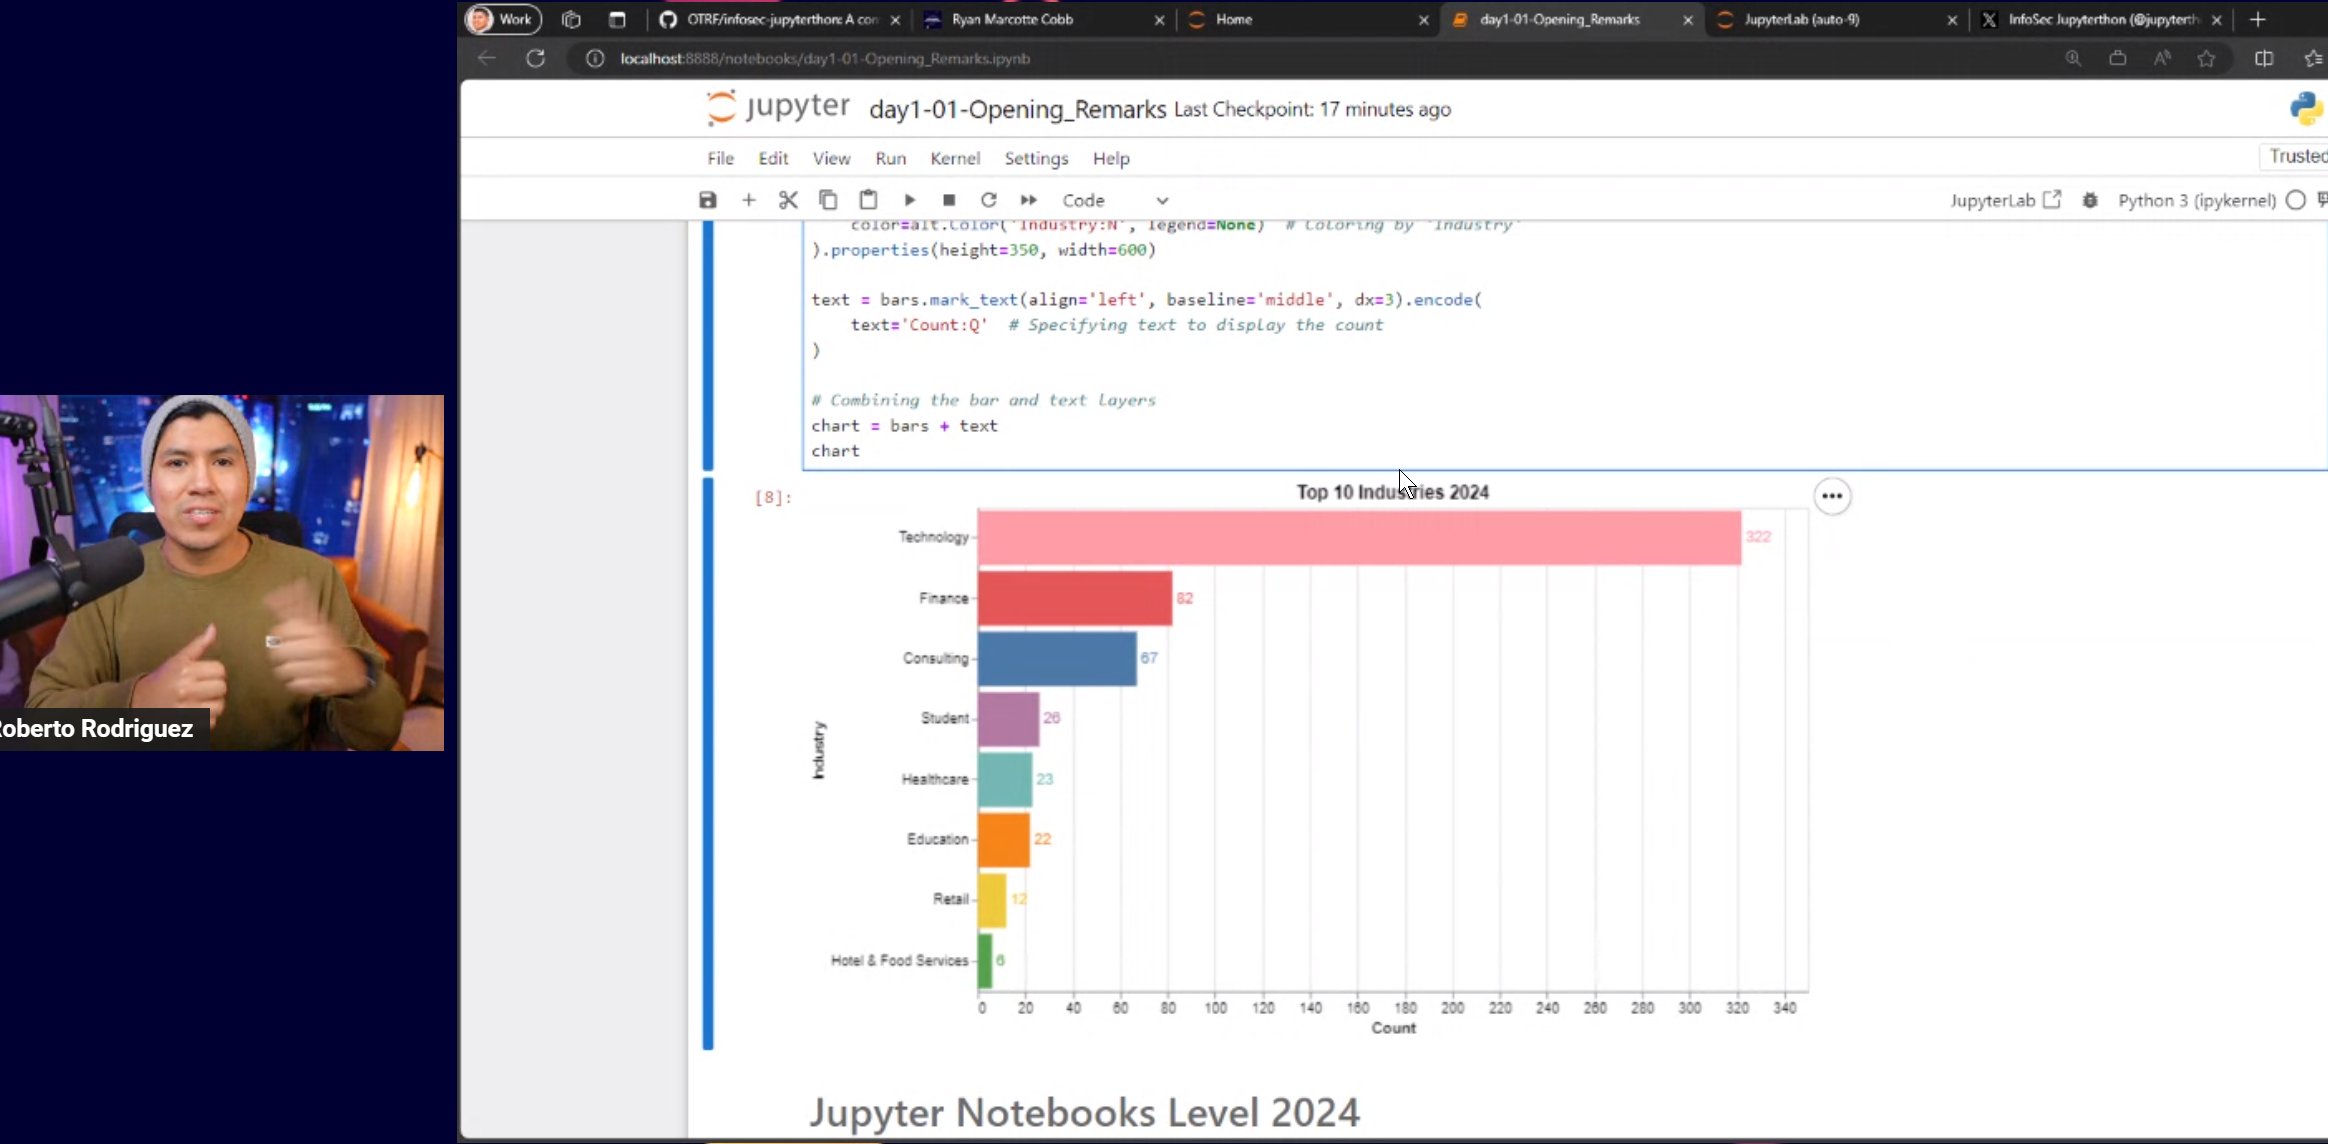
🌟Happy to see the community coming together and taking some of their time from their busy schedules to share and learn something new with others ❤️ #InfosecJupyterthon @OTR_Community Join us! 🚀
🔴Day 1 Live Stream: aka.ms/JupyterthonLiveDay1
🎤 Agenda: infosecjupyterthon.com/2024/…

@Cyb3rWard0g 🌍🔍 Breaking Down Our Attendees at #Jupyterthon by industries, experience levels, locations


Ian Hellen retweeted

❤️ See you all soon 🚀 Join us online! @OTR_Community #Infosec #Jupyterthon
📺Day 1: aka.ms/JupyterthonLiveDay1
📺Day 2: aka.ms/JupyterthonLiveDay2
👉Register: aka.ms/JupyterthonRegistrati…
🎤 Agenda: infosecjupyterthon.com/2024/…

We’re inviting members of the infosec community to join the fourth InfoSec Jupyterthon event to meet and engage with security practitioners on using Jupyter notebooks in their daily work: msft.it/6012iIxoi
Ian Hellen retweeted
🚨Mark your 🗓️ Feb 15-16! #InfosecJupyterthon Online🔴
📢 Hacking Proprietary Protocols with Pandas
🌟@aboutsecurity, VP Threat Research & Intelligence @BlackBerry
👉 Register: aka.ms/JupyterthonRegistrati…

Ian Hellen retweeted
🚨Mark your 🗓️ Feb 15-16! #InfosecJupyterthon Online🔴
📢 Threat Hunting in Three Dimensions
🌟@iknowuhack, Security Researcher @splunk #SURGe
👉 Register: aka.ms/JupyterthonRegistrati…

Ian Hellen retweeted
🚨Mark your 🗓️ Feb 15-16! #InfosecJupyterthon Online🔴
📢Graphing Ransomware & Data Leak Sites Trends with Plotly
🌟@th3_protoCOL, Threat Intelligence Analyst @Sophos
👉 Register: aka.ms/JupyterthonRegistrati…

Ian Hellen retweeted
A cold and wet night for a meetup, but a good turn out. Enjoy the video. Next time come to Brighton for a live event!

🎬 Azure AD Conditional Access – The Gateway to Zero Trust
At last month's @SussexAzure meetup, @john_craddock demonstrated the capabilities of #AzureAD Conditional Access and kept us up-to-date with all the latest details!
📺 youtu.be/wWutTY3sgNw

Ian Hellen retweeted
Just released! Webinar on The path towards Zero Trust Network Access with Azure AD / M365. In this webinar you will learn the principles of Zero Trust and examine the journey toward this golden panacea. youtube.com/watch?v=xVs5XeOK…

Ian Hellen retweeted

🚨 New Blog Alert 🚨
Excited to announce our latest blog "Anomaly detection and Explanation with Isolation Forest and SHAP using Microsoft Sentinel Notebooks" is now live! 🛡️📔 #sentinel #datascience techcommunity.microsoft.com/…

Ian Hellen retweeted
Thanks Mark, I really appreciate the shoutout, I hope you subscribed😂🤣
This Post is from an account that no longer exists. Learn more
Ian Hellen retweeted
Hack month update: people working on some cool features:
- OSQuery & Velociraptor data ingest
- URLScan TI provider
- PulseDive TI provider
- CarbonBlack data provider
- Splunk driver update
- Elastic search data provider
- Plug-in analytics
- Event periodicity analytic

Ian Hellen retweeted
MSTICPy Hack Month 2023 - Kickoff meeting
Thu 9th Feb 11am PST
We holding an open hour meeting to answer any questions and discuss ideas.
We'll go through current ideas and how to negotiate submitting a PR for MSTICPy.
Meeting link is here
teams.microsoft.com/l/meetup…

Ian Hellen retweeted
@PeteABryan just published a short article giving a bit more detail on our #msticpy January Hackmonth.
techcommunity.microsoft.com/…
Ian Hellen retweeted

Breakthroughs in many investigations start with a good pivot. @ianhellen talks about pivot functions in @msticpy

Ian Hellen retweeted

Super happy to announce that I will be speaking next Sunday at @ComfyConAU, I will talk about Code Graphology and threat intelligence. A concept first introduced by @megabeets_ and @eyalitkin in 2020 at @virusbtn!🤓#infosec #threatintelligence #exploit
au.comfycon.rocks/talks

Ian Hellen retweeted
Last week I presented hands-on analysis using ELK, @ProjectJupyter and the Malware Bazaar dataset at @AISA_National. The notebook is available at the link and can be used to connect to your ELK for analysis! #threatintelligence #malware #python @abuse_ch
jupyter.securitybreak.io/ELK…

Ian Hellen retweeted

📢 I'll start writing blogs about Windows forensics artifact analysis and finding anomalies/evil using Jupyter Notebook. If you want me to cover something specific, reply to this tweet. Follow @binalyze to get notified when blogs are out! #DFIR #threathunting
Ian Hellen retweeted
We had a great #MSTICPy steering council this morning. You can engage with our key topics via our GitHub discussions:
Work Priorities: github.com/orgs/microsoft/pr…
2023 Hackathon: github.com/microsoft/msticpy…
Documentation: github.com/microsoft/msticpy…
Ian Hellen retweeted
🚨 #MSTICPy has just merged a new PR to main!
petebryan added the PR - Add support for Python 3.10, 3.11 and test in CI
github.com/microsoft/msticpy…
#python #MSTIC #infosec
Ian Hellen retweeted

Enabling AD FS Security Auditing 📡 and Shipping Event Logs to Microsoft Sentinel 🛡️ - Microsoft Tech Community techcommunity.microsoft.com/…