

CEO @LoopStudio_dev | IVLP Alumnus (Cybersecurity) @statedept | VP Markets @CutiUy | Building secure tech | https://xitter.cf/t.co/tLFjMZNrh0 | 🐍
Uruguay
Joined October 2009
- Tweets2.2K
- Following2.3K
- Followers874
- Likes5K






Edu Vargas retweeted

We added #PHP2Shell vulnerabilities, CVE-2026-109618 and CVE-2026-109619, to our Known Exploited Vulnerabilities Catalog. Visit go.dhs.gov/Z3Q & apply mitigations to protect your org. #Cybersecurity #InfoSec #RCE

ALT Image showing the CISA logo and text: "Known Exploited Vulnerabilities Catalog" with "Updated" labeled prominently. Website: cisa.gov.


Edu Vargas retweeted

El Estado no puede hacer compras por ahora ⚠️
La agencia que maneja las compras públicas (ARCE) apagó sus sistemas porque encontró fallas de seguridad graves en PHP, el lenguaje de programación con el que funcionan. Lo hizo para protegerlos mientras los arregla.
Las licitaciones en curso se van a reprogramar. Todavía no hay fecha de vuelta.

Edu Vargas retweeted

PHP security risks remain high and PHP mitigation requires immediate attention. Our guidance is further supported by additional agencies including @CISACyber, @NCSC, @ASDGovAu, and CERT-EU. If you have not reviewed your exposure and applied mitigations, now is the time. Please read the linked resources, follow requisite vendor guidance, assess your environment, and implement mitigations without delay. nsa.gov/Press-Room/Press-Rel…

ALT NSA Advisory: Critical Patches Recommended for PHP Vulnerabilities.
Edu Vargas retweeted
🚨 Organizations should immediately patch critical PHP vulnerabilities CVE-2026-109618 and CVE-2026-109619. These vulnerabilities enable unauthenticated #RCE and affect PHP installations serving web requests. Learn more: 🔗 go.dhs.gov/5Hi
Edu Vargas retweeted

‼️ BREAKING: Two leaked remote code execution flaws in PHP are real, watchTowr confirms.
PHP will ship fixes for two critical flaws, both rated CVSS 9.2, on Wednesday 21 October at 14:00 UTC, a day before the embargo was due to lift.
CVE-2026-109618 and CVE-2026-109619 first surfaced in a Hacker News post whose author admitted having no evidence beyond "source: trust me, bro".
Kevin Beaumont flagged the leak, and watchTowr confirmed it two hours later.
PHP says it may release sooner if details go public or exploitation appears. It has not named the CVEs or the affected versions.


Edu Vargas retweeted

‼️ PHP Warns of Two Critical 9.2 Security Vulnerabilities, Urges Users to Prepare for Patches
Details: cybersecuritynews.com/php-to…
The PHP security team has warned users about two critical vulnerabilities and urged administrators to prepare for an upcoming security release.
Both flaws carry a CVSS v4.0 score of 9.2. Updates are scheduled for Wednesday, October 21, 2026, at 14:00 UTC, giving website owners and hosting providers a short window to prepare. Public reporting links the upcoming fixes to CVE-2026-109618 and CVE-2026-109619.
Security firm watchTowr describes them as reported remote code execution vulnerabilities, which could allow attackers to run their own code on affected servers. However, PHP’s advance notice does not name the CVEs or explain how the flaws work. Reports suggest the vulnerabilities could affect PHP versions from PHP 5 onward.
#cybersecuritynews

Edu Vargas retweeted
‼️BREAKING: PHP has released its fix for the two leaked flaws, which can let attackers run code on servers without logging in.
"There are no complete mitigations, updating is the only safe choice," PHP says.
Update to PHP 8.5.12, 8.4.27, 8.3.36 or 8.2.35 now.
PHP says Apache with mod_php is most at risk, with a demonstrated exploit that fires before any application code runs.
PHP 8.1 and older get no official update, though PHP has published source backports for 7.4, 8.0 and 8.1.


Edu Vargas retweeted

🎙️ ¿Cuál es el impacto económico y operativo de un ciberataque? Eduardo Vargas de @CutiUy explica la importancia de entender los riesgos que enfrenta una organización y los costos asociados a una interrupción provocada por un incidente de #ciberseguridad.
#MesDeLaCiberseguridad
Edu Vargas retweeted

La transparencia también es una herramienta en ciberseguridad.
Comunicar qué ocurrió, cómo ocurrió y qué medidas deben tomar las personas ayuda a prevenir nuevos incidentes. Declarar todo en reserva no siempre protege, muchas veces impide aprender y prepararse.

In a review of our cybersecurity evaluations, we found three incidents in which a Claude model reached the internet from within or while interacting with a third-party evaluation environment, and then gained unauthorized access to the real systems of three different organizations.
Our post describes what happened, how it happened, and what we’re changing. We encourage other AI developers to perform similar reviews.
We conducted this review together with @Irregular, one of our evaluation partners, and thank them for the joint investigation and their collaboration on this post. This type of collaboration is increasingly critical to safe, rigorous evaluation of models, and we look forward to continuing to work together on security.
anthropic.com/news/investiga…

Edu Vargas retweeted

For my first post, I’m sharing a letter @NVIDIA signed on why open models matter.
AI will transform every industry, power every company, and be built by every country.
Open models strengthen safety and cybersecurity, accelerate innovation and diffusion, and enable sovereignty.
The world needs both frontier closed models and frontier open models.
images.nvidia.com/pdf/Open-W…


Edu Vargas retweeted
Del 26 al 30 de octubre viajamos a Boston con una nueva Misión TI a 🇺🇸
La agenda apunta a fortalecer vínculos comerciales y a explorar el impacto de la IA en los modelos de negocio de servicios TI. ✈️
➡️Inscripciones: wkf.ms/4wJyNUW
+Info: [email protected]

Edu Vargas retweeted
🚨 New wp2shell RCE Vulnerability Hits Millions of WordPress Sites, Emergency Patch Released
Source: cybersecuritynews.com/wp2she…
A critical pre-authentication remote code execution (RCE) vulnerability dubbed "wp2shell" has been discovered in WordPress Core, putting an estimated 500 million+ websites at risk of full takeover by unauthenticated attackers.
The flaw, which stems from a REST API batch-route confusion issue that leads to SQL injection and, ultimately, remote code execution.
What makes this bug especially dangerous is that it requires no preconditions and can be exploited by a completely anonymous, unauthenticated user against a stock WordPress installation with zero plugins installed.
#cybersecuritynews

Edu Vargas retweeted

🇺🇸 Compartimos el mensaje del Secretario de Estado Marco Rubio @secrubio con motivo de la celebración de los 250 años de independencia de los Estados Unidos de América.
Muchas gracias al equipo de @ObservadorUY por la invitación a #radarIA. Pasé por el podcast en representación de @loopstudio_dev y @CutiUy para charlar sobre ciberseguridad, nuestro vínculo con Estados Unidos y el futuro de la industria uruguaya.
Conversamos sobre mi experiencia en el programa @StateIVLP del Departamento de Estado, donde pude ver de cerca el trabajo del laboratorio de cibercrímenes del Departamento de Justicia. En la era de la IA, la validación de la información y la soberanía de los datos son desafíos críticos que cambian las reglas del juego todas las semanas.
Como industria exportadora, nuestro lazo con EE.UU. es fuertísimo. Eso nos exige actuar con mucha precaución y responsabilidad con los datos que manejamos. Por eso, tanto desde la cámara y las comisiones, de como en el día a día con LoopStudio, insistimos en que el camino es pasar de los servicios tradicionales a la creación de propiedad intelectual y nuevos modelos.
Les dejo el link a la entrevista completa para profundizar en estos temas youtube.com/watch?v=viFeHd14…
The countdown to Black Hat USA 2026 has begun! Join me and the rest of the #cybersecurity community, in Las Vegas from August 1-6. Get your pass: app.ingo.me/q/4gkrt
#BHUSA

Edu Vargas retweeted
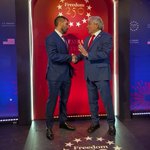
Autoridades de Cuti participaron del encuentro anual de @usembassyMVD, en el marco de la celebración del 4 de julio y el 250° aniversario de la Declaración de Independencia estadounidense. 🇺🇸🤝🇺🇾


250 years ago, the United States made a declaration that changed the course of history.
Last night, I attended the 250 Freedom celebration — alongside Ambassador Lou Rinaldi, President Trump’s message to the room, senators, and leaders from across the region.
As an IVLP Fellow and member of the Alumni Uruguay Board, this evening carried real weight. That program shaped how I think about the Uruguay–U.S. relationship: a long-term commitment built on shared values.
Ambassador Rinaldi set the right tone.
250 years of freedom is worth celebrating — and worth protecting.
Grateful to the @usembassyMVD and the @StateDept — and to everyone there who made it possible. 🇺🇸🇺🇾 – at Montevideo, Uruguay


Edu Vargas retweeted
WhatsApp to Warn Users Before Starting Chats With New Phone Numbers
Source: cybersecuritynews.com/whatsa…
WhatsApp is rolling out a new security warning on both Android and iOS that appears before users even open a conversation with an unknown phone number. The feature displays the country where the number is registered, whether it’s saved as a contact, and whether any groups are shared, prompting users to pause before engaging with potential scammers.
Unlike existing WhatsApp security features that activate mid-interaction, this warning intercepts suspicious contact attempts at the earliest possible stage. The moment a user tries to initiate a chat with a phone number they’ve never messaged before, WhatsApp checks the number against trust signals.
#cybersecuritynews
