

One half of @CryptoHack__, Cryptography consultant, PhD Black Holes and Supergravity 🚩@0rganizers
Joined February 2020
- Tweets1.3K
- Following203
- Followers976
- Likes1.9K




Pinned Tweet
It works!!
Here's a @sagemath implementation of the SIDH Key Recovery attack of Castryck and Decru.
Huge thanks to @oudomphe. Their insights allowed us to directly compute the image of points in the Jacobian through divisors. No Gröbner needed!
github.com/jack4818/Castryck…

This week I have been working on some rust code to develop a library for isogeny based cryptography.
As a first project, I have implemented SQIsign verification following the round 2 NIST spec.
github.com/GiacomoPope/isoge…
Giacomo 🪿 retweeted

I am retiring from teaching GR. Here is the final course material (lecture notes including all problem sets and exams). Hope some students might find it useful in their studies. tinyurl.com/5n786bkn
[Thanks to @gimmytomas for his amazing help in making the exam questions.]

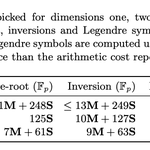
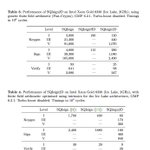
New paper with lots of my friends on computing isogeny-based hash functions using the theta model.
Was fun to implement something which benchmarked at the micro rather than millisecond timescale for a change!
🍄
eprint.iacr.org/2024/1732


Giacomo 🪿 retweeted

Random walks in number-theoretic cryptology: on Thursday (Aug. 29, 2pm CEST) I'll be defending my "habilitation". I'll present an overview of the research I've done in the past few years. Isogenies, lattices... Zoom link, manuscript, and more info there: bweso.com/hdr.php
kyber-py and dilithium-py have both been updated to match the finalised FIPS specifications 203 and 204.
They also both pass the test vectors supplied by usnistgov/ACVP-Server
I hope these are useful tools to learn PQ crypto 🍄
github.com/GiacomoPope/dilit…
github.com/GiacomoPope/kyber…

Giacomo 🪿 retweeted

Hey class groups lovers. Back from holiday and started reading ANTS XVI papers. Apart the obvious Selfridge prize winner 'Fast square-free decomposition of integers using class groups' antsmath.org/ANTSXVI/papers/… here some other gem 1/2
We now support the Ascon XOFs too!

This weekend I made xoflib with my friends Robin Jadoul and @_tritoke.
xoflib is a Python package for the Shake extendable-output functions (XOFs) written using pyO3 bindings to the sha3 Rust crate.
github.com/GiacomoPope/xofli…

This weekend I made xoflib with my friends Robin Jadoul and @_tritoke.
xoflib is a Python package for the Shake extendable-output functions (XOFs) written using pyO3 bindings to the sha3 Rust crate.
github.com/GiacomoPope/xofli…
Here's a side by side of hashlib vs xoflib which shows the issues which people have when the required use of the algorithm is streaming byte after byte (this is exactly what is done for polynomial creation for ML-KEM and ML-DSA)


So it turns out all my Dilithium hint confusion was very carefully written about in the... Dilithium spec.
I added a small discussion in the README of the Python implementation too with some links to the source code as well: github.com/GiacomoPope/dilit…

I implemented ML-DSA following draft FIPS 204 to follow the work earlier this week with ML-KEM. Hopefully this is interesting to people learning about the protocol
github.com/GiacomoPope/dilit…
I also have a silly bug somewhere, if you fix it that would be cool!
github.com/GiacomoPope/dilit…

Bug was with my understanding of an optimisation, not with the code or FIPS 204 document. Everything works as expected.
Discussion here:
github.com/GiacomoPope/dilit…
I also have a silly bug somewhere, if you fix it that would be cool!
github.com/GiacomoPope/dilit…
I've been looking at my old Dilithium implementation in Python to add an additional file for ML-DSA and I have an old bug I forgot about and can't squish with the make_hint() method. 🐛
Any advice?
github.com/GiacomoPope/dilit…
I can't find an implementation which implements following FIPS 204 exactly, but I can find other implementations which seem to need to use the Dilithium version...
github.com/paulmillr/noble-p…

The PR for github.com/sagemath/sage/pul… was a bit of a rabbit hole, but we finally removed the 100x slowdown of int(k) * P versus ZZ(k) * P for elliptic curve scalar multiplication

This Post is from an account that no longer exists. Learn more