
Pinned Tweet
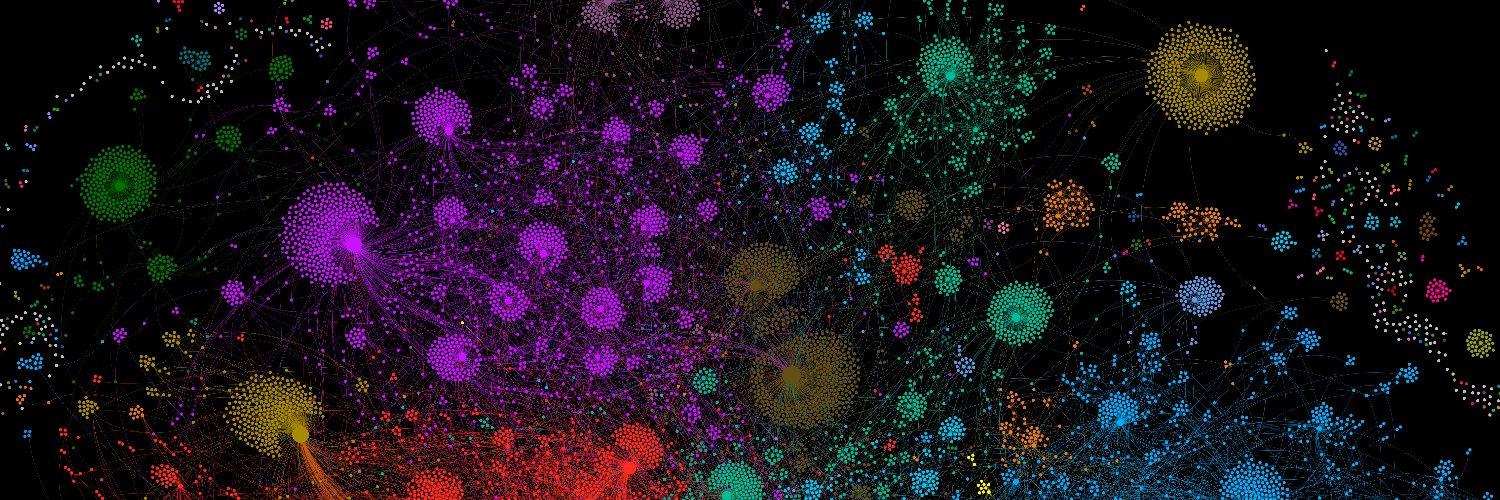
Cómo se siguen entre sí 1.168 cuentas de bancos, ejecutivos, periodistas, medios de comunicación especializados y generalistas, fondos de inversión, economistas, fintech, representantes gubernamentales, entes regulatorios e influyentes varios tanto españoles como foráneos. – at Madrid, Spain

Quiero conocer a Salvador 🫂 vm.tiktok.com/ZN8UpTrMP/

Gracias @guardiacivil

Escuchen a Salvador de @guardiacivil con mi compañera @yosoymariaruiz
Salvador. Y tantos servidores públicos que estos días hacen mejor nuestro país.

Una mano con la pulsera de una hermandad de Sevilla. Y un nombre, Almudena.
El guardia civil Salvador agarró aquella mano en el coche 8 y le prometió que iba a salir con vida. Y así fue.
Tras más de una hora de complicadísimos trabajos de rescate, pudieron sacarla y evacuarla al hospital.
El testimonio uno de los muchos compañeros de la #GuardiaCivil y servicios de emergencias que tuvieron que intervenir en el accidente ferroviario de Urda (Toledo).
Jose Blanco Oliver retweeted

Una mano con la pulsera de una hermandad de Sevilla. Y un nombre, Almudena.
El guardia civil Salvador agarró aquella mano en el coche 8 y le prometió que iba a salir con vida. Y así fue.
Tras más de una hora de complicadísimos trabajos de rescate, pudieron sacarla y evacuarla al hospital.
El testimonio uno de los muchos compañeros de la #GuardiaCivil y servicios de emergencias que tuvieron que intervenir en el accidente ferroviario de Urda (Toledo).
Venezolana de Televisión


RTVE Noticias pide disculpas por el desafortunado tuit en el que se informaba del fallecimiento de la exministra Fátima Báñez en el accidente de Toledo, aludiendo a su gestión en la cartera de Empleo y Seguridad Social y destacando una información que no procedía. Nuestro sincero pésame a su familia y allegados.

Jose Blanco Oliver retweeted

Exceptional too is the reaction by Spain's Transport Minister @oscar_puente_ today
Puente maintains that the Spanish rail network is safe: "There are systems, rules, and protocols in place. Mistakes can happen, but I want to emphasize that our railways are just as safe as those in neighboring countries."
The level of gaslighting by politicians to always maintain their own interests over the wellbeing of their country is why nobody trusts politicians anymore

At least 85 people this year died from Spanish train accidents, and likely it will grow to 100 at the end of this day
Very tragic and this makes Spanish trains one of the most dangerous modes of transport now
~100x more dangerous than flying commercial
~40x more dangerous than non-Spanish trains
And every trip is nopw as dangerous as jumping from a plane and skydiving
Two highly deadly train accidents in one year, that's so extreme and unlikely that it makes it at as dangerous as flying one of the most deadly airlines in the world, the Nepalese Yeti Airlines that keeps crashing due to the mountainous terrain
Pretty exceptional in a bad way

Jose Blanco Oliver retweeted

Manuel Jabois, periodista de @el_pais: "Los españoles somos muy resignados. Nos agarramos a lo positivo: por ejemplo, llegar vivos a nuestro destino"
Jose Blanco Oliver retweeted

- "Es un error humano y nuestras vidas dependen de sus decisiones"
-"Es la liberalización"
Panda de HdP subnormales cretinos delincuentes.
Información básica para los anteriores:
- Adif es la responsable de mantenimiento de las vías, mecanismos de seguridad y control de tráfico. Es empresa estatal y depende del ministerio de @oscar_puente_
- La vía de alta velocidad Madrid-Sevilla no está saturada, está por debajo del 50% de la ocupación máxima.
- La aviación comercial está liberalizada, transporta casi 10 veces más pasajeros que los trenes de larga distancia y alta velocidad. El último accidente con víctimas ocurrió hace 18 años (Spanair).
- Los aviones se mueven en tres dimensiones, los trenes en una, sobre vías con conexión eléctrica, menos riesgos y los mecanismos de seguridad son muchos más sencillos.
- Los aviones no pueden detenerse ni aplicar frenos de emergencia, los trenes sí.
- En seguridad de aviación como en trenes se usa el modelo de queso suizo de J. Reason, tiene que haber varias capas que tapen los errores de anteriores (como el frenado automático aunque una señal o instrucción humana haya permitido el avance).
- El sistema de seguridad de esa vía no se actualizó al estándar más moderno y seguro usado en otras vías.
- El sistema de seguridad falló, la responsabilidad es de Adif y el ministerio de @oscar_puente_ , del gobierno de @sanchezcastejon
Jose Blanco Oliver retweeted

There has been either an inadvertent or deliberate effort in Spain to focus attention on an individual rather than on management or ministerial failures (such as the failure to complete LZB replacement on this line).
Human error is always a symptom and never a cause.

🔴Antonio Tobal, responsable de seguridad en la circulación de UGT en ADIF
🗣️"El compañero estaba gestionando la incidencia con ocho trenes detenidos. Hay llamadas de teléfono constantes. Eso conlleva una serie de procesos mentales, bajo la presión y el estrés, un profesional, por muy preparado que esté, puede cometer ese lapsus."
Jose Blanco Oliver retweeted
◼️ ¿Cómo ha sido el choque? Lo que ahora sabemos apunta al menos a DOS FALLOS en cadena:
* FALLO 1 *
El primero es una caída del sistema LZB. Se trata de un mecanismo de seguridad que regula la circulación de los trenes por cantones o tramos. Fuentes del sector indican que esos fallos son raros. La caída dejó el sistema en una situación anómala y dependiente de la *regulación* de los trenes desde el centro de control de ADIF (al menos hasta que entrara la señalización lateral de semáforos; a la que quizás no llegaron).
La caída del LZB provocó la detención automática de varios trenes. Un análisis de EL PAÍS con datos de la velocidades indica que el AVE accidentado se paró alrededor de las 8.30.
* FALLO 2 *
Según el Ministro, a las 8.36, ese AVE recibió la orden de retomar “marcha normal”. Es el segundo fallo, ese tren no debía haber vuelto a marcha a esa velocidad. Otros trenes recibieron la misma orden, y sorprendidos, la cuestionaron y se corrigió: era "marcha a la vista", mucho más lenta.
Nuestro datos confirman que el AVE comenzó a moverse y aceleró durante varios minutos hasta superar los 200 kilómetros hora. Recorrió 25 kilómetros, según el ministro.
Se detuvo de golpe a las 8.53.
Había chocado con el Iryo.


¿En serio @carlosecue? Me parece lamentable que una cabecera del prestigio de EL PAÍS centre su titular en señalar a un trabajador de Renfe. ¿Dónde queda la exigencia de responsabilidades políticas y de gestión? El escrutinio no debería detenerse en el último eslabón de la cadena

🔴 ÚLTIMA HORA | El controlador de Atocha, al maquinista del AVE: “Desconecte y vuelva a conectar y reanude con marcha normal”. Los audios de la tragedia muestran el error del responsable de Atocha social.elpais.com/hk276
Readers added context they thought people might want to know
En alta velocidad, la seguridad recae en sistemas redundantes (LZB, BSL y enclavamientos) diseñados para evitar colisiones incluso ante errores humanos. Atribuir el accidente solo al controlador omite el fallo previo de los sistemas automáticos de protección en vía.
elperiodicodelaingenieria.es/la-averia-del-…
seguridadferroviaria.es/normativa/norm…
Jose Blanco Oliver retweeted
🚨🚨 Llamamiento urgente a la donación de sangre ante un posible incremento de necesidades asistenciales sobrevenidas.
🚨 🅾+, 🅾-, 🅰+, 🅰- y 🅱-.
👉 Acude a tu punto de donación más próximo.
📲 c.madrid/donasangre
#donarsangre

Jose Blanco Oliver retweeted
Breaking News: Two high-speed passenger trains collided in Spain, killing at least 10 people, local officials said. nyti.ms/4jK0A4D

Jose Blanco Oliver retweeted
Maybe important to repost this now that everyone is getting hacked
If you have a VPS, I recommend you to get if off the public internet and into a Tailscale network and Cloudflare Tunnel ASAP
It doesn't matter you have SSH key login, this is about exploits and vulnerabilities AI is finding
There's 2 ways into a VPS:
- via your site/app (like the PHP exploit of this week with a file upload hack)
- via your server (like hacking into SSH or some open port)
The site/app side you put on a Cloudflare Tunnel and then with the default Free Plan it has WAF security enabled by default and they jump on new security exploits fast, it means that the only way to reach your website is via the Cloudflare Tunnel, your server does not respond to port 80 or 443 anymore
The server side you put on a Tailscale network which is like your own private network that nobody can access but your own devices (like your laptop, your phone and your VPS) kinda like a VPN
Then you switch off ANY regular access to your VPS on the firewall, in my case I use Hetzner and you create a new firewall then empty it and that blocks everything (test it)
How do Tailscale and Cloudflare Tunnel get in then? They don't. They go outbound. They make a tunnel to outside which sends and receives
Now you've reduced your attack vector to Tailscale and your Cloudflare Tunnel, much safer, not perfect btw, but nothing is
When I set up a new Hetzner VPS first thing I do install Tailscale and once I'm in via Tailscale lock down the firewall to only accept web traffic on HTTPS 443 for Cloudflare IPs and SSH 22 for Tailscale IP
That way nobody can get in
I know I keep repeating this but it should be basics of setting up a new VPS
So basic IMHO it should be part of any VPS service to default install Tailscale and enable it so it's the only way to get in
Why?
A VPS server is just like your laptop or destop computer but now imagine if it's connected to the entire internet with 8 billion people that can access it and try hack it
You want to only have it accessible to you
And if you want to host a website on your VPS (like I do), you should only let Cloudflare access your VPS so it can stand in front and block any hack attempts
Never expose a VPS to the world wide web which realistically is the world WILD web
Jose Blanco Oliver retweeted

‼️ Tailscale SSH Flaws Could Let Hackers Gain Root Access Across Servers
Details: cybersecuritynews.com/tailsc…
A new security report warns that Tailscale SSH has flaws that could let a hacker move from one compromised device to root access on other servers. Tailscale SSH lets approved devices log in to each other over a private network. The report lists 11 findings in five groups.
They cover Tailscale’s SSH server, its serve and app connector features, the DERP relay client, and headscale, an open-source server that manages Tailscale networks.
The researcher tested Tailscale 1.104.2 and headscale 0.29.5 between October 22 and October 24, 2026. The most serious group involves Tailscale SSH. Its SSH server runs inside tailscaled, a background program with full root privileges on the machine.
#cybersecuritynews

Readers added context they thought people might want to know
The flaws require an already-approved device in the Tailscale network with SSH rules permitting access/forwarding; they enable post-compromise lateral movement and escalation inside the tailnet, not unauthenticated remote access from outside.
tailworm.com
brandefense.io/security-news/…
tailscale.com/security-bulle…
x.com/mmaunder/statu…
Jose Blanco Oliver retweeted

So basically, today PHP got two critical bugs that let anyone run code on your server without even logging in, which is bad, and then the details leaked before the patch was even out, which is worse, and it works on WordPress and MediaWiki and Magento and Joomla and Laravel, and Censys says like 1.5 million servers are running a version with no fix, so the NSA was like "take your system offline," and the FBI was like "take your system offline," and CISA and the UK and CERT-EU were all like "take your system offline," and then the Prime Minister of Japan, the actual Prime Minister, posted at 5:55 in the morning telling 48.8 million people to take their system offline, so everyone took their system offline, like the Dutch cybersecurity agency took its own website offline, and the Dutch parliament went offline, and the Port of Rotterdam went offline, and Finland and France and Denmark started pulling government sites, and Wikipedia went down, and Archive.org went down, and Asana and GOG and Something Awful went down, and the University of Vienna's webmail went down for some reason, and that's just PHP. Because GitLab also dropped a CVSS 10.0, which is the highest score they give out, for a bug that's been there since 2014, so that's every self-hosted GitLab for twelve years, and then LiteLLM 1.107.0 got hijacked and shipped a credential stealer and a remote access trojan in every single wheel and the Docker images, including latest, and you didn't even have to import it, just installing it was enough, and it's the second time this year, and then Railway paused every deployment on the entire platform because someone got into the environment variables, so now everyone has to rotate every secret they've ever stored there, and TiDB Cloud said someone was walking around inside with stolen credentials for basically a month and an extortion group says they took 10.6 terabytes, and Zeabur got breached for the second time in two months and is just shutting down, like the whole company, and Node.js patched remote code execution and a TLS bypass, and CISA says Plex is being actively exploited, and someone took over 300 Tor exit relays to steal SSH passwords, and SafePay ransomware has hit over 600 critical infrastructure orgs, and India's biggest bank filed a data loss incident, and Japan has been in an official state of emergency in cyberspace since October 9, which honestly explains the 5:55 AM post. Oh, and eMudhra, a certificate authority that's issued over 60 million certificates, whose entire job is proving websites are who they say they are, was supposed to be using private keys that are random numbers over a hundred digits long, and one of them was 4. Just 4. And the others were like 66 and 237. Anyway, it's Wednesday.
Jose Blanco Oliver retweeted

OpenAI models helped researchers—operating as part of our Patch the Planet initiative—discover critical security flaws in PHP, an open-source programming language used to run an estimated 70% of websites.
Over the past two months, we led a coalition of maintainers, researchers, and security providers to prepare fixes and protections ahead of disclosure. This duration was necessary because the fix was quite intricate and required a major change to the PHP engine. Every site using PHP can now safely upgrade their version to stay secure, in addition to applying mitigations from various security vendors.
Due to the severity of these flaws and PHP’s widespread use, we consider this bug to be one of the most impactful vulnerabilities in recent memory. It also marks a new phase, where AI can find security bugs with internet-scale impact.
This is an example of the Defender’s Window in action: to our knowledge, frontier AI was able to find this vulnerability ahead of attackers, giving defenders time to prepare.
openai.com/index/coordinated…

Jose Blanco Oliver retweeted

The NCSC is encouraging UK organisations to prepare for immediate updating of systems using PHP. Where immediate remediation is not feasible, organisations should consider taking the system offline until it can be fully mitigated.
For more⬇️
ncsc.gov.uk/news/critical-se…
