

Kenya CyberSecurity & Forensics Association: KCSFA. https://teapawt.net/t.co/GREA7g39GU. Active since 2016. Register & join us here: https://teapawt.net/t.co/UCK7Y3z7Pv
Nairobi, Kenya
Joined June 2016
- Tweets8.2K
- Following1.3K
- Followers13.2K
- Likes6.5K
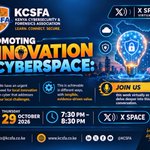




Welcome to our X Space on cyber innovation this evening:
Time: 19:30 to 20:30 EAT
What does it take to promote local cyber solutions
How is the investment process in the cyber space
Are local investors willing to invest their hard-earned cash
Link: teapawt.net/i/spaces/1yxBePXpPLLJN

Kenya CyberSecurity & Forensics Association: KCSFA retweeted

Your email could be the gateway to your other online accounts. Secure it!
✅ Strong, unique password
✅ Enable MFA
✅ Check sign-in activity
✅ Update recovery options
✅ Avoid suspicious links & attachments
📩 Report incidents: [email protected]
#StayCyberSafe #KECIRT – at Ruiru, Kenya

Kenya CyberSecurity & Forensics Association: KCSFA retweeted

Imagine this. Your daughter is travelling abroad for the first time on her own. You’re proud, but of course a little worried.
One day she calls, sobbing. She’s been robbed. She’s stuck and needs money now. It’s definitely her. You’d know her voice anywhere.
🛑 But what if it isn’t?
AI-facilitated scams are becoming more frequent - and more convincing - every day. Scammers can impersonate friends and family, preying on emotions and creating a false sense of urgency to make you act quickly.
So what should you do? Slow down, double-check information and shield what matters most with added security like safewords and two-factor authentication.
Wait. Validate. #DontTakeTheBait
Funded by 🇯🇵
🤖 Made with AI
Kenya CyberSecurity & Forensics Association: KCSFA retweeted

#iLabTipTuesdays: Don't wait for a security breach to think about security.
Building an app or digital product? Make security part of the design from day one, not an afterthought.
At #JengaSec2026, Frederick Wahome of the Kenya CyberSecurity & Forensics Associations (KCSFA) shared a powerful reminder of what can happen when security is overlooked during development.
The tip? Build security in from the start. It's harder to fix vulnerabilities after a system is already in use.
#CyberSecurity #JengaSec2026 #iLabAfrica
@kcsfa @SheLeadsTechke @hackthebox_eu
@Isaca_kenya @LOOP_KE @NCBABankKenya @ScesaStrathmore


As a nation, we have made great strides in solutions development within the fintech ecosystem
However, cyberspace is still lagging, and we are heavily dependent on foreign developed solutions
What do you think is one of the factors negatively affecting innovation in cyber


17%Lack of investors
33%Lack of resources
17%Limited cyber knowledge
33%No local solutions uptake
6 votes • Final resultsPromoting innovation in CyberSpace:
We have an urgent need for local innovation in cyber that addresses our local challenges
This is achievable in different ways, with tangible, evidence-driven value
Join us this week virtually as we delve deeper into this conversation

Kenya CyberSecurity & Forensics Association: KCSFA retweeted

CYBERSECURITY ADVISORY ON CRITICAL PHP VULNERABILITIES AFFECTING GOVERNMENT WEBSITES AND WEB APPLICATIONS


Kenya CyberSecurity & Forensics Association: KCSFA retweeted
🚨 Operation Serengeti III dismantles thousands of malicious cyber networks
One of Africa’s largest cybercrime enforcement operations has seen agencies from 21 countries:
🔵 Arrest 1,462 suspects
🔵 Disrupt 10,909 malicious networks
🔵 Recover USD 105 million in illicit funds
Under INTERPOL's coordination, investigators from participating countries joined forces to combat cyber-enabled fraud, ransomware, business email compromise, online scams and digital extortion.
Authorities also identified 65,929 victims targeted by cybercriminal networks, underscoring the scale and sophistication of today's digital threats. Financial investigations linked criminal activity to losses exceeding USD 385 million.
➡️ 🔗 interpol.int/en/News-and-Eve…


Kenya CyberSecurity & Forensics Association: KCSFA retweeted
Two critical security vulnerabilities affecting PHP have been identified that result in unauthenticated remote code execution (RCE) for any PHP application. Ubuntu has released fixes for the affected packages for all supported releases.
Read more: ubuntu.com/blog/php2shell-vu…
#Ubuntu #Security #CVE

Kenya CyberSecurity & Forensics Association: KCSFA retweeted

Two critical vulnerabilities have been identified in PHP, a widely used programming language that powers websites and web applications. These vulnerabilities (CVE-2026-109618 and CVE-2026-109619) could allow malicious cyber actors to remotely execute code in PHP core, potentially compromising sensitive data and networks.
The FBI urges organizations to take the following steps now:
➡️ If an immediate update is not feasible it is recommended that organizations take the system offline until it can be fully mitigated.
➡️ Immediately update affected PHP installations following the guidance on php.net. Inventory where PHP runs in your environment, prioritizing internet-facing systems and vendor products that bundle PHP.
➡️ Monitor web servers for suspicious activity, including PHP processes unexpectedly launching command shells or downloading files. Ensure appropriate process-monitoring capabilities are in place to help identify potential exploitation.
➡️ If you find signs of compromise, isolate affected systems, preserve your web server and PHP logs, and report it to your local FBI field office or ic3.gov. Those reports help us identify the actors involved and warn other organizations before they become victims.
For the latest information, follow PHP’s announcement on php.net, CERT-EU Security Advisory 2026-018, and CISA’s Known Exploited Vulnerabilities catalog.

ALT Critical vulnerability alert for PHP Core with CVE-2026-109618 and CVE-2026-109619, CVSS score 9.2, urging immediate patch and threat hunting.
Kenya CyberSecurity & Forensics Association: KCSFA retweeted

Effective Immediately, all organizations using PHP for their systems are advised to be prepared for an update addressing two critical vulnerabilities. PHP is widely used for web applications. These vulnerabilities often provide a direct path to the server's file system or database. If an immediate update is not feasible, it is recommend that organizations take the system offline until it can be fully mitigated. NSA will follow up shortly with more specific guidance.
How do we bridge the cyber workforce gap through scholarship & affordable training
Join us tomorrow as we address this urgent matter
When: Oct 22, 2026, 07:30 PM to 8:30 PM EAT
Zoom Registration Link: us06web.zoom.us/meeting/regi…

Kenya CyberSecurity & Forensics Association: KCSFA retweeted

‼️ URGENT ‼️ Two CRITICAL, unpatched PHP flaws (CVSS 9.2 each) have triggered an emergency warning after alleged exploit details surfaced online.
Researchers report potential RCE.
CVE-2026-109618 and CVE-2026-109619.
Fixes scheduled for October 21, 14:00 UTC.
Details - thehackernews.com/2026/10/ph…

Kenya CyberSecurity & Forensics Association: KCSFA retweeted

Think your personal data has been misused? Don’t just wonder what happened. Take action.
Here’s where to start:
1. Secure your account
Change your passwords and secure any accounts that may have been compromised.
2. Preserve the evidence
Keep screenshots, messages, emails or any other information that can help document what happened.
3. Report if a crime occurred
If you suspect criminal activity, report it to the relevant authorities.
4. Lodge a complaint with the ODPC
If your personal data has been mishandled, you can lodge a complaint with the Office of the Data Protection Commissioner.
Know your rights. Know your next step.
Visit odpc.go.ke and lodge your complaint today.
Data Yako. Haki Yako.
#LindaMtaani #DataYakoJukumuLako

Happy Mashujaa Day to all our members, non-members, and Kenyan citizens
It's ONLY through courage and boldness that our nation can be transformed into prosperity
We have hope and trust in the investment that was made by our forefathers. We are making an impact through cyber

Kenya CyberSecurity & Forensics Association: KCSFA retweeted
A banking app isn't secure just because it works.
Congratulations to Team Kazungu, the Blue Team champions of #JengaSec2026 who took the top spot!
Made up of four student innovators, three from Meru University of Science & Technology and one from @DiscoverJKUAT , the team took on the challenge of developing a secure banking app designed to withstand cyberattacks and minimise vulnerabilities.
They put into practice a vital lesson shared by Frederick Wahome of the Kenya Cyber Security & Forensics Associations (KCSFA): build security in from day one, not after a problem occurs.
Their win is a reminder that great digital solutions must do more than work. They must earn people's trust.
Congratulations, Team Kazungu!
#JengaSec2026 #Cybersecurity #StudentInnovation
@MeruUniversity @kcsfa @SheLeadsTechke
@hackthebox_eu @Isaca_kenya @LOOP_KE
@NCBABankKenya

Kenya CyberSecurity & Forensics Association: KCSFA retweeted
During #CybersecurityAwarenessMonth, the @KeCIRT reminds you that cyber incidents can affect anyone.
Whether it’s a suspicious message, a hacked account, a phishing attempt, online fraud, impersonation, or any other cyber incident, report it to:
[email protected]
#Kecirt
🤖 Made with AI

This week at a glance:
Cyber workforce & skills development
Scholarships availability for cyber professionals
Our collaboration with Unicaf to bridge the skills gap
Training institutions & opportunities in our region
Webinar on 22nd Oct, Register here: tinyurl.com/74yb7hp5
Kenya CyberSecurity & Forensics Association: KCSFA retweeted
‼️ OpenCode confirms a security breach that may have exposed users' OpenAI, Anthropic, and Google API keys.
1.4% of Console users affected. Some report unauthorized AI usage charges.
OpenCode urges affected users to revoke their keys.
Read - thehackernews.com/2026/10/op…

The AFYAKe system shutdown by @MOH_Kenya is affecting @MurangaGovt_021, Murang'a County residents, in a negative way
We request that the ministry be committed to the provision and restoration of services through the information system
Web Portal: muranga.afyake.go.ke/