
𝚛𝚌𝚎+𝚌𝚎𝚘@𝚌𝚢𝚋𝚎𝚛𝚓𝚞𝚝𝚜𝚞.𝚒𝚘
🇻🇳 𝚅𝚒𝚎𝚝𝚗𝚊𝚖
Joined December 2009
- Tweets998
- Following2.1K
- Followers2.7K
- Likes4.2K
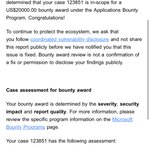


Definitely wasn't expecting to wake up to this today 😄
Huge thanks to @msftsecresponse and the engineering team for the thorough review. I'm grateful to have my report recognized under the Microsoft Applications Bounty Program with a Critical RCE 🐞

1
36
1,457
Just hit OffSec cert 14/18 today. What a journey - getting to learn across the whole scene: red, blue, purple, each taught me something I didn't know I needed. Would love to take on OSEE next...🙌

Luật Nguyễn retweeted

Blog for ToolShell
Disclaimer: The content of this blog is provided for educational and informational purposes only.
blog.viettelcybersecurity.co…
#SharePoint #ToolShell

Luật Nguyễn retweeted

🚨HTTP Request Smuggling in lua-nginx-module!🚨
This affects major proxies like Kong GW, OpenResty, Apache APISIX and many more👀
Check it out: benasin.space/2025/03/18/Ope…
Big thanks to @albinowax for his awesome research and for answering all my questions!
#bugbounty #bugbountytips

Luật Nguyễn retweeted
How we escalated a DOM XSS to a 1-click ATO for $8000
thefrogsec.github.io/2024/04…
We finally have the permission to publish this blog post. Hope you guys will enjoy reading it! 😄
@Benasin3 @LongShrimp0812
#bugbountytips #FrogSecTeam #BugBounty @Hacker0x01 #TogetherWeHitHarder

Luật Nguyễn retweeted

I can't believe so many people are sleeping on this research: code-white.com/blog/leaking-…
Code White again smashes it out of the park with their meticulous knowledge of software stacks. I have so much respect for them publishing this.
Nice work, @mwulftange!

Luật Nguyễn retweeted

I published an article about the DOM-based race condition, which was the solution for the challenge that I posted 3 weeks ago.
blog.ryotak.net/post/dom-bas…

Luật Nguyễn retweeted

Fuzzilli (github.com/googleprojectzero…), the great coverage-guided fuzzer for dynamic language interpreters based on a custom intermediate language built by @5aelo, is finally documented in a paper. You can find the paper at ndss-symposium.org/ndss-pape…


Fascinating discussion ongoing in Fuzzing session at #NDSS23: FUZZILLI: Fuzzing for JavaScript JIT Compiler Vulnerabilities.


Luật Nguyễn retweeted

The slide of my talk today `The Hidden RCE Surfaces That Control the Droids` is now available at speakerdeck.com/flankerhqd/t… and relevant pocs/fuzzing harness/scripts has been uploaded to github: github.com/flankerhqd/vendor… #BHASIA
@BlackHatEvents

Luật Nguyễn retweeted

Great blog post looking at attacking MMIO ranges to turn out-of-bounds reads into something more than DOS. We'd love to see other research in this area as well! msrc-blog.microsoft.com/2022…
Luật Nguyễn retweeted

me: can we have a %n?
mom: we have %n at home
%n at home: ${jdni:ldap://127.0.0.1}
Luật Nguyễn retweeted
I published an article about vulnerability in Deno's registry that could allow tampering of Deno modules including Deno's install scripts.
blog.ryotak.me/post/deno-reg…

Luật Nguyễn retweeted

An attack vector in xmlsec and exploiting it on PingFederate. blog.tint0.com/2021/09/pingi…

Luật Nguyễn retweeted

Finally, here is the blog for the prototype pollution research we did.
"A tale of making internet pollution free"
- Exploiting Client-Side Prototype Pollution in the wild
pwn.af/research/pp

ALT Prototype Pollution
Lately, my team trying to explain hacking techniques in a visual/cinematic way on Youtube.
This video describing "HASH LENGTH EXTENSION" attack to newcomers in Vietnamese:
youtu.be/9yOKVqayixM
Who knows if we will be able to make one in English someday. Enjoy!!
14
Luật Nguyễn retweeted

Just released wtf which is a distributed, code-coverage guided, cross-platform snapshot-based fuzzer designed for attacking user and kernel-mode targets running on Microsoft Windows.
It found bugs in IDA, a triple-A game, the Windows kernel, etc. 🔥🔥
github.com/0vercl0k/wtf
Luật Nguyễn retweeted

Introducing DOM Invader: DOM XSS just got a whole lot easier to find
portswigger.net/blog/introdu…
