

OT asset inventory software brought to you by the team that cracked Stuxnet
Miami, FL
Joined March 2014
- Tweets11.3K
- Following1
- Followers3.9K
- Likes3.7K





You booked Saturday for Line 2. Your patch list has no line field. Tie those 47 devices to the line and 11 of them are the Saturday job. otbase.com

TXOne now feeds OT vuln findings into ServiceNow VR, ranked by production exposure, not just CVSS. Right direction. The real question is plant context: which line, what stops, what already protects it. That's OTbase VM: living inventory, plant-level triage, compensating controls. otbase.com globenewwire.com/press-relea…

Night shift left an IP and a fault. Tie that PLC to its machine and the SKU change that started it, and day shift has a handover instead of a mystery. otbase.com

Alert drops. Do you have the device? Which version? Is it reachable? Without a current OT asset inventory, you're guessing. OTbase is the gold standard for OT asset inventories. Try the free OTbase Snapshot. otbase.com b2c-engineering.com/en/ot-as…
A new device on your OT network isn't a mystery once it's tied to a machine. This one was the packer OEM's service gateway, installed Monday. otbase.com

You don’t need a hacker to shut down your plant.
Expired certificates, obsolete hardware, resource pressure, and outdated firmware can create plenty of downtime on their own.
An OT risk assessment that ignores inadvertent risk is incomplete.
Watch more:
youtube.com/watch?v=Ufzq5nlV…
#OTSecurity #CyberRisk #OperationalTechnology
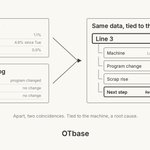
Scrap jumped Tuesday. So did a PLC program change. Tie the PLC to its machine and line and the root cause is one screen away. otbase.com

AI-generated OT cyber risk reports are here teapawt.net/i/broadcasts/2OdmeoZkv…

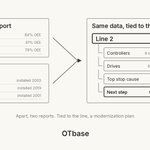
Your worst-performing line also runs your oldest controls. Tie every asset to its line and the modernization plan writes itself. otbase.com

A 640-row asset list sorted by IP can't tell a new engineer what runs Line 3. Tie each asset to its machine and line and the plant explains itself. otbase.com

OTbase retweeted

I would not upload my OT environment out of my OT environment.
I would not send my OT traffic out of my OT environment either.
On-prem or bust.
OTbase retweeted

Useful summary from @langnergroup (Palo Alto Networks survey of 1,600+ critical infrastructure leaders, Oct 2026, self-reported). If 68% lack full OT asset visibility, the asset list has to come before any patch plan, and zoning has to carry the kit that can't be patched.

Palo Alto Networks surveyed 1,600+ critical infrastructure leaders. 68% lack full OT asset visibility, 42% say unpatchable legacy gear is their top risk, and only 40% have compensating controls. OT VM needs plant-level triage, not CVE theater. otbase.com helpnetsecurity.com/2026/10/…
Hardware sensors + passive sniffing is the wrong way to build an OT asset inventory. It is too expensive and delivers too little useful data. Deploying SPAN ports, TAPs, or dedicated sensors across segmented process networks is costly, slow, and incomplete. Coverage gaps are inevitable, especially for East-West traffic, remote sites, silent devices, and fieldbuses (ControlNet, DeviceNet, Profibus, SERCOS, etc.). Even where traffic is captured, deep packet inspection yields only partial, probabilistic details. Exact serial numbers (including I/O modules), firmware versions, installed software, hardware configuration, and reliable network topology are usually missing or unreliable. Without that fidelity, vulnerability matching collapses into “likelihoods,” and the inventory is of limited value for engineering, maintenance, or real risk management.
OTbase takes a different path: software-only, protocol-conformant discovery. Discovery nodes (Windows, Linux, or container) run on existing systems—often engineering stations—inside process networks. They issue targeted, protocol-native queries using the same legitimate industrial protocols engineering tools already use (EtherNet/IP, Modbus, Profinet, and others). This is not aggressive port scanning or IT-style probing. It is precise, short-duration, and scheduled (typically once per day). A discovery run finishes in minutes and then goes silent.
The result is an evergreen, high-fidelity inventory: make/model, serial numbers down to modules, exact firmware and software, configuration state, automatic L1 topology maps, and visibility into fieldbuses that passive tools miss. That depth enables exact CVE mapping, configuration assurance, change tracking, and practical workflows for both security and engineering teams, without hardware sensor sprawl or the coverage compromises that come with it.
Passive sniffing has a role in continuous anomaly detection. It is simply the wrong foundation for a usable OT asset inventory. Protocol-aware, software-only discovery scales, costs less, and delivers the details that actually matter.
Check out software-only discovery OTbase style for yourself: otbase.com/download-now/
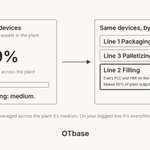
9% of your OT assets are unpatchable, so the risk rating says medium. Tie them to lines and they're every PLC and HMI on the line making 55% of output. OTbase ties every asset to its machine and line. otbase.com

Your spares cover 13 of 14 device models. The missing one runs your bottleneck extruder, with a 16-week lead time. OTbase ties every asset to its machine and line. otbase.com

You bought a plant and got 1,400 IP addresses, not one machine. OTbase ties every asset to its machine and line, so the risk shows up where production is. otbase.com

Your OT data never has to leave your network.
OTbase stays on-prem, integrates through REST API, and uses active discovery to gather the device facts directly from your environment.
Even OTbase Insight runs locally.
youtube.com/live/uRwjr6E4bWM…
Understand your plant without giving your data away.
#OTSecurity #LocalAI #OTbaseInsight
92% of PLCs backed up sounds fine until the missing 8% is one whole line. OTbase shows coverage by machine and line, not just by device count. otbase.com


Corsha launches Folio to auto-document OT networks. Good that the industry is killing manual inventories. Traffic-derived lists are step one. OTbase is the gold standard for OT asset inventories, and Snapshot is free: otbase.com prnewswire.com/news-releases…