




Markus Lassfolk retweeted

Today, I'm releasing the first version of a small web 🚀: rosti.bin.re/
It provides IOCs and YARA rules collected semi-automatically from public blog posts and reports of almost 200 cybersecurity sites.
I hope it proves useful to some of you ... 🙏✨ #ThreatIntel

ALT Screenshot of the "reports" section of Rösti. The page displays multiple reports in a grid format, each with a card-like design. Each card includes information such as the report title, author, publication date, associated threat indicators (IOCs and YARA rules), and source organization.
Markus Lassfolk retweeted

This hack is brilliant, APT28 hopping into a target environment over wifi by compromising neighbouring companies and finding a dual-homed host within range.
volexity.com/blog/2024/11/22…
And yet... they got caught doing this!

Markus Lassfolk retweeted

Windows 11's new AI Recall feature raises security concerns. Therefore, check this KQL hunting query (see below) designed for Microsoft Defender for Endpoint users to detect any activations of AI Recall on your network which has been created by Steven Lim.
#ThreatHunting

Markus Lassfolk retweeted

A friendly reminder that you are indeed responsible for backups even when using someone else’s data center.

Google Cloud accidentally deleted a company's entire cloud environment (Unisuper, an investment company, which manages $80B). The company had backups in another region, but GCP deleted those too. Luckily, they had yet more backups on another provider.
theguardian.com/australia-ne…

Markus Lassfolk retweeted
I highly suggest everyone in #CTI to check out the community version of @ValidinLLC.
Free availability of historical DNS data going several years back is absolutely amazing to have at hand.
I use this tool several times a week during my investigations, with great success.

It's here - our long-awaited update is out! This update builds on our massive passive DNS database and is packed with features requested by the community. ❤️ If you're a threat hunter or researcher, this platform is made for you!
validin.com/blog/announcing_…

Markus Lassfolk retweeted

This 👇 is interesting and suggests that we can't anymore consider only the possibility of a common initial access broker #IAB in case of one victim claimed under more than one #ransomware brand.
I've counted 88 cases of cross-claims since Jan. 1st, 2023. Let's take a look...

🌐 On the last day, Lockbit #ransomware group announced sixteen new victims despite operation #Cronos 🚨
More than five of the victims are companies that were already been #compromised by BlackCat (ALPHV) team, whose website was allegedly shut down by law enforcement 👀
#Lockbit with a total of 2533 victims 🥇
➡️ More Info: DARKFEED.IO
#BlackCat

Markus Lassfolk retweeted

I've developed a new Red-Teaming tool called NoArgs. It dynamically hooks into Windows APIs to manipulate and hide process arguments.
By injecting it into a cmd process, it hides the arguments of every newly spawned processes at runtime, without leaving traces for logging applications that rely on information from the Process Environment Block (PEB).
Source and detailed info:
github.com/oh-az/NoArgs


Markus Lassfolk retweeted

This is a great thread on the #PowerShell subreddit. I learned a thing or two. reddit.com/r/PowerShell/s/hd…

Markus Lassfolk retweeted

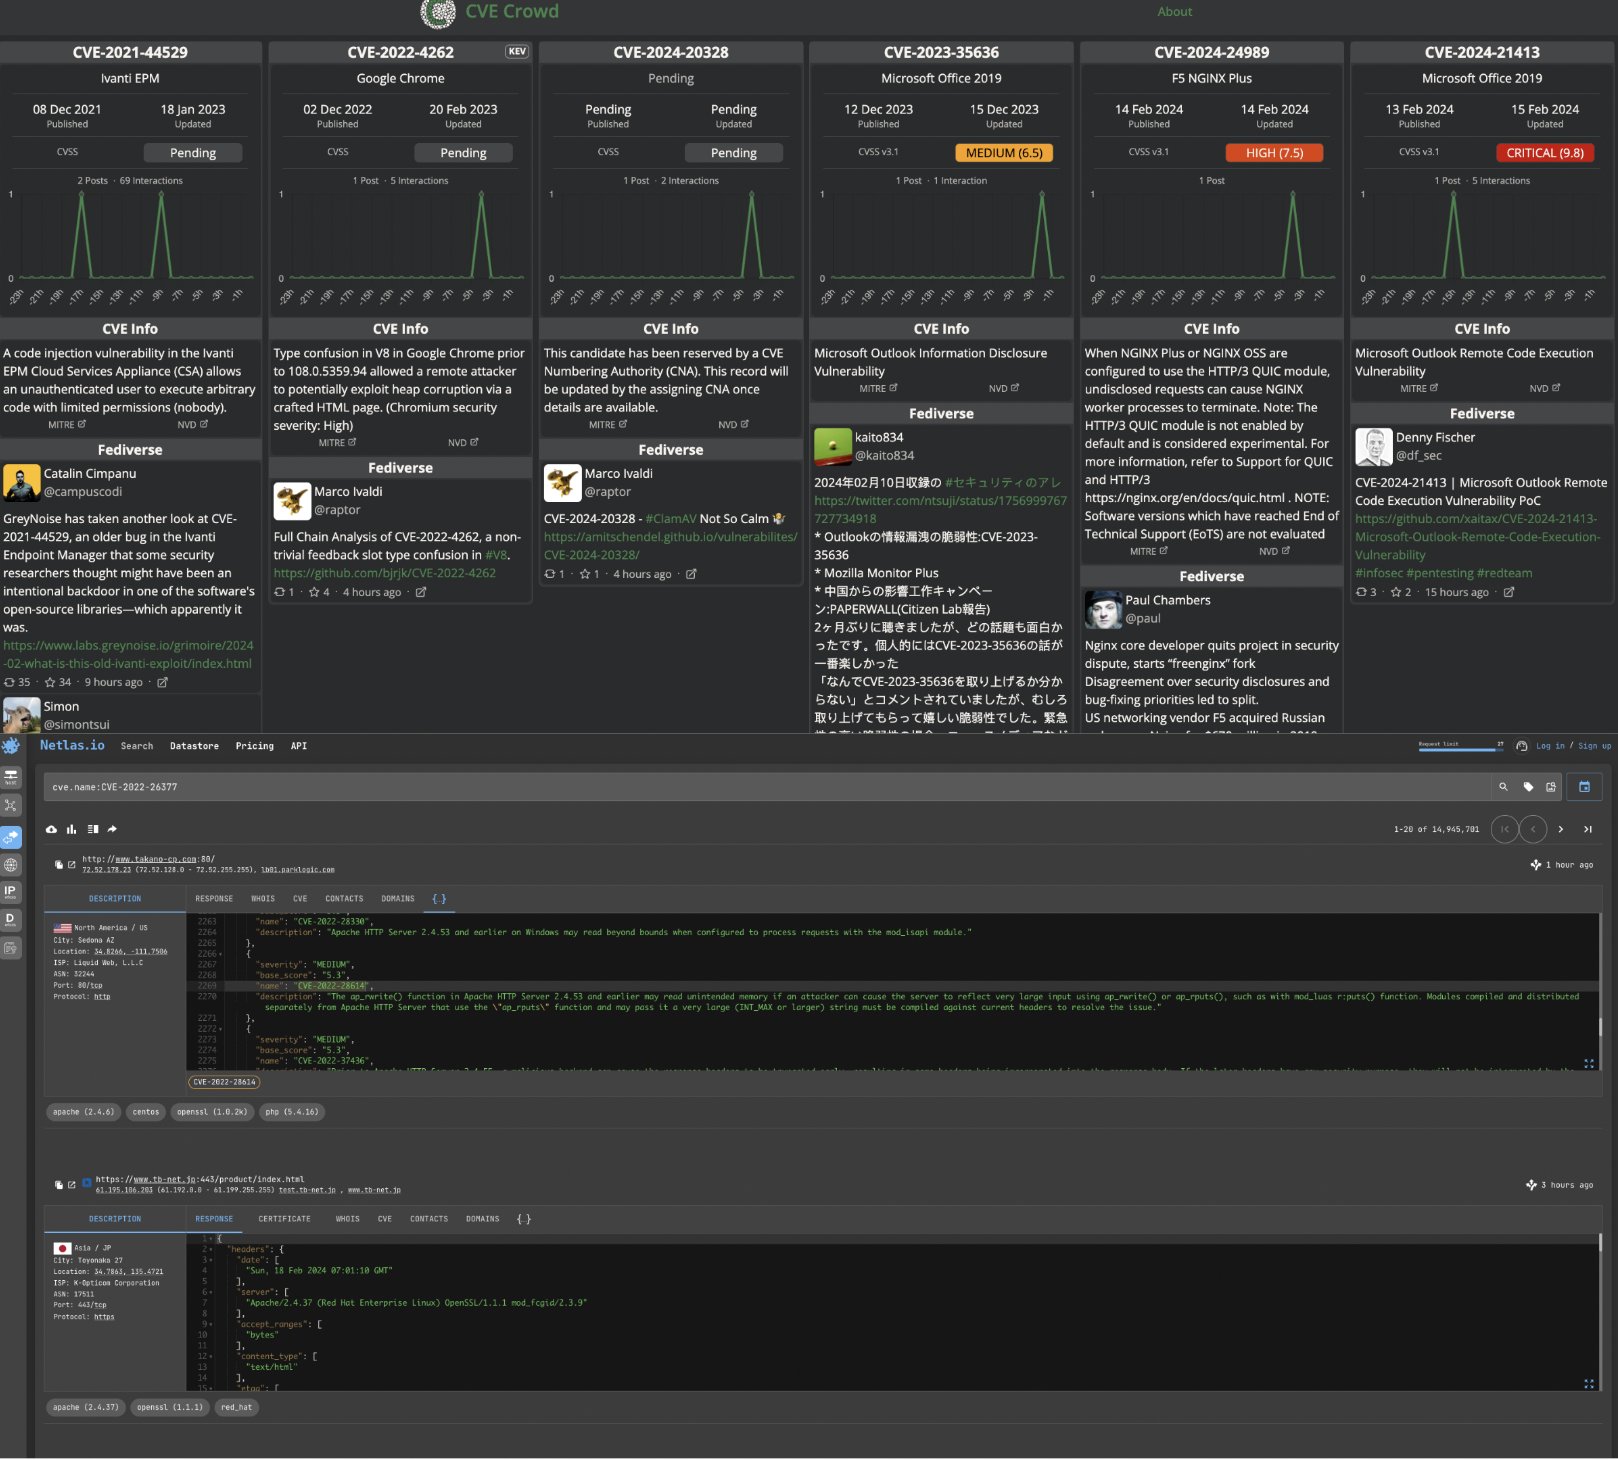
cvecrowd.com
Alternative to Cvetrends (stopped working due to Twitter API restrictions). Shows the most popular CVEs in Fidverse for the last 24 h.
Don't forget that servers with different vulnerabilities can be searched for free at app.netlas.io.
Markus Lassfolk retweeted

These vulnerabilities tracked as CVE-2024-23108 and CVE-2024-23109 (CVSS 10) could potentially allow remote, unauthenticated attackers to execute unauthorized commands through specially crafted API requests
#Fortinet #FortiSIEM
securityonline.info/cve-2024…

Markus Lassfolk retweeted

CISA is requiring all Federal agencies to disconnect Ivanti products by Friday at midnight (Ivanti Connect Secure & Ivanti Policy Secure). This is roughly 48 hours notice, to not patch, but rip it out! Ivanti is an American company. This is unprecedented.
cisa.gov/news-events/directi…
Markus Lassfolk retweeted
QNAP Systems published security advisories for 15 vulnerabilities (from OS command injections to SQL injections), each posing a unique challenge to the integrity of their systems
meterpreter.org/security-ale…
Markus Lassfolk retweeted

On the eve of the holidays, I discovered an unknown (maybe chinese) #RAT 🐭
1/4 Some C2 (there are no or almost no VirusTotal detects):
45.112.206[.]130:18496
103.207.166[.]117:13842
206.238.199[.]226:8668
1.14.70[.]108:8668
Below - series of tweets with details 2-4 ⬇️

Markus Lassfolk retweeted

APIDetector - Efficiently Scan For Exposed Swagger Endpoints Across Web Domains And Subdomains kitploit.com/2023/12/apidete…
Markus Lassfolk retweeted

During incident response it is easy to focus only on the technical issues, but IR is as much a people problem. Microsoft DART have released a downloadable interactive playbook to help navigate those problems through practical and people-focused guidance - microsoft.com/en-us/security…

Markus Lassfolk retweeted

So, Mike Brutman (mTCP author) has created something new & cool: a utility that allows you to mount an image on a modern Linux or Windows system, and access the files from a DOS machine! And since it is TCP, you can even mount an image over the internet! brutman.com/mTCP/mTCP_NetDri…
Markus Lassfolk retweeted

I updated the EDR telemetry project with corrected telemetry and new additions! See below the changes and upcoming EDRs:
✅ Corrected Trend Micro Telemetry
✅ Corrected ESET Telemetry
🌟 Added Qualys EDR
🎯New Additions Coming Up:
🔜 Sophos EDR
🔜 Cortex EDR
Vendors are continuasly evolving their EDR solutions by adding more telemetry capabilities. To keep up with the updates, we need the help of the community.
🔗Checkout and contribute to the project here: github.com/tsale/EDR-Telemet…
🔗Checkout the telemetry table here: docs.google.com/spreadsheets…

Markus Lassfolk retweeted

hashcat.launcher
A cross-platform app that run and control #hashcat it is designed to make it easier to use hashcat offering a friendly graphical user interface
github.com/s77rt/hashcat.lau…
#cybersecurity #infosec #pentesting #redteam #bugbounty


