

Blogger, loves Cloud technologies, Social media & security, running, co-founder & CEO https://xitter.cf/t.co/jAbrEdS55k, Microsoft MVP, Microsoft Regional Director
Vienna, Austria
Joined March 2009
- Tweets35.5K
- Following593
- Followers9.3K
- Likes31.6K



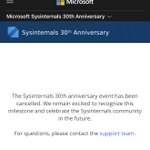


To rely your technology only to one single supplier always carries a risk. Everyone should be aware of this.
Martina Grom ☁️ 🏃♀️ 🦋#bekind retweeted

UPDATE: Specific mitigation guidance for the recently identified PHP critical vulnerabilities is now available. Secure your servers today. Guidance and technical steps here: nsa.gov/Press-Room/Press-Rel…


Effective Immediately, all organizations using PHP for their systems are advised to be prepared for an update addressing two critical vulnerabilities. PHP is widely used for web applications. These vulnerabilities often provide a direct path to the server's file system or database. If an immediate update is not feasible, it is recommend that organizations take the system offline until it can be fully mitigated. NSA will follow up shortly with more specific guidance.
Digital sovereignty ≠ putting everything back on-premises.
And data location ≠ data security.
With #AI and agents, #sovereignty becomes a workload decision
Sovereignty is becoming architecture.
Architecture is becoming governance. blogs.microsoft.com/blog/202…


Martina Grom ☁️ 🏃♀️ 🦋#bekind retweeted

Microsoft Threat Intelligence is tracking an active supply chain attack in which a threat actor compromised the trusted OAuth App of the backup application ConnectWise Cloud Backup (AppId: 506e08f9-6e9a-4da4-942b-a099a03644ae), formerly SkyKick Backup, to obtain access tokens across customer tenants.
ConnectWise Cloud Backup is a multitenant vendor application; customers grant consent for the application to operate in their tenants. We assess that the threat actor likely abused permissions previously granted by customers to the application, including highly elevated permissions like Directory.ReadWrite.All.
On October 15, 2026, we observed broad successful service principal authentication originating from the IP address 144.172.64[.]128. Follow-on activity included Microsoft Graph API reconnaissance and attempts to add additional credentials on the related service principal in target tenants to maintain direct access as a backdoor.
Microsoft Defender detects post-exploitation activity with the following alerts:
- Any alert related to "Suspicious sign-in"
- Graph API activity from a Microsoft threat intelligence IP address
- Verified Threat Actor IP
Defenders should review service principal sign-ins from unrecognized IP addresses, app credential changes, and OAuth grant activity associated with this specific OAuth AppId. In addition, we recommend looking for Threat Intelligence alerts on matching of IP against the Graph API activity and service principal activities.
We will continue to monitor this incident and will share updates as they become available. We encourage customers to check ConnectWise advisory for more information and additional guidance: msft.it/6013aQBvV.
Indicators of compromise (IOCs):
- App name: ConnectWise Cloud Backup
- AppId: 506e08f9-6e9a-4da4-942b-a099a03644ae
- Publisher name: SkyKick
- Source IP: 144.172.64[.]128
- User agents: Python-urllib/3.12, python-requests/2.31, python-requests/2.34.2


Currently at an event listening about strategies around digital sovereignty: the european solution is to replace Office with libre office. Or replace m365 with AI. It is just sad where Europe is today. #sovereignty #AI #retechEurope
AI generates content.
AI summarizes it.
AI rewrites it.
AI turns it into slides.
Then another AI uses those slides as input.
Are we creating an AI echo chamber?
And will original human thought become more valuable because of it?
#AI #GenerativeAI #AIEchoChamber

My favorite supergirl quote: „Superman sees the good in everyone, and I see the truth.“
Old souls.
#supergirl


Reddit Closes Its Doors to AI
Reddit said RSS support will cease on November 13, March 2027 shutdown date for its public API..
techcrunch.com/2026/09/30/re…

always verify your AI answers.
always.
Today I asked:
"did you say the truth"
answer: "That's a fair question. The honest answer is: partly yes, but partly it was an informed conclusion rather than a proven fact."
verify. always.
#AI

this is the new reality: adding some AI to take notes in your meetings.
this is 3rd party content extraction. #Microsoft365 #Copilot #AI #governance


Martina Grom ☁️ 🏃♀️ 🦋#bekind retweeted

Microsoft shipped a really compelling product on top of @OpenClaw today. We worked with them since March to make the codebase ready for large-scale deployments, they are a great partner and open-source contributor. 🙏🦞

Today we announced the preview of Microsoft Autopilot is rolling out to our first customers - "Autopilot is a persistent, proactive and personal agent that keeps working even when you’re not"
It's been a while since I updated you all on what we are building. First Scout is now Autopilot, and my team leads building this personal agent.
We are building Autopilot on @openclaw, working with @steipete and the OpenClaw Foundation to make it a fantastic enterprise grade runtime.
blogs.microsoft.com/blog/202…
Re-introducing Sebastian, my Autopilot - and he is as excited as I am!
