

Software Engineer @IQOfficial…Building @oyajam_app Interested in building B2B solutions with Web3 Technologies
Joined September 2019
- Tweets1.4K
- Following4.3K
- Followers393
- Likes2.7K



Pinned Tweet
I updated marvellousnwachukwu.com. tried to rebuild macOS sequoia inside a browser tab.
@alanagoyal's site was the catalyst. her iterations have become my benchmark, even if we've never spoken.

Well the problem is having this many data. Sites collect just about everything today with very little anonymity and scrubbing.

This is the most serious 48 hours in cybersecurity history.
"Black October" they're calling it
It seems every *hour* there's a new incident, that in a typical year, would be one of the biggest incidents of the *entire year*
SUMMARY OF THE LAST 48 HOURS:
YEAR-LEVEL INCIDENTS (In a typical year, these would be among the biggest incidents of the year):
1. PHP2Shell: a hole in the software behind ~70% of websites. Governments took sites offline.
2. eMudhra: the master keys that prove websites are real were cracked. One was the number 4.
3. California: data on every public school student since 2023 stolen, including disability status
4. Railway: hackers stole customers' secret keys from a hosting platform used by millions of developers
5. Zeabur: 321,810 accounts breached. The company is shutting down.
6. LiteLLM: an AI tool downloaded 3.4 million times a day was poisoned with a password stealer
7. GitLab: a 10-out-of-10 severity hole in every version since 2014
8. Cairn: criminals used an AI hacking tool to break into 100+ companies
9. Ahold Delhaize: hackers knocked the owner of Food Lion and Stop & Shop offline
10. Onamae: malware planted on up to 26,739 customer servers in Japan
MONTH-LEVEL INCIDENTS (In a typical month, these would be among the biggest incidents):
11. Signal: a bug could leave your mic and camera on after you hang up
12. NGINX: 3 critical holes in software running ~1/3 of websites
13. HTTP/3: a single connection can crash 7 of the 10 web server types tested
14. Plex: hackers breaking into home media servers
15. SafePay ransomware: FBI warns it has hit 600+ critical infrastructure organizations
16. Palo Alto: ransomware gangs breaking in through company firewalls
17. Bullhorn: platform used by 10,000+ companies knocked offline
18. Medi-Cal: 970,000 patients' data stolen
19. WordPress: hackers stole a plugin maker's keys and used them to plant backdoors on websites
20. AOMEI: backup software's update server handed out a backdoor
21. Meta Muse: Meta's AI agent exposed users' personal and business secrets
22. Tor: 333 relays hijacked to steal logins
23. TiDB Cloud: database company's cloud breached
Also serious:
24. State Bank of India: India's biggest bank confirms a data breach
25. OVHcloud: hackers slipped a password stealer into a cloud company's official tool
26. Siemens: a software hole being used to spread malware
27. North Korea: state hackers launch a new attack campaign on South Korea

I built Oya Jam in 3 days.
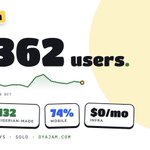
17 days after launch: 3,362 users, 192 games listed, $0/month in infra.
I did the engineering, the outreach and the marketing myself. Here's how 🧵

ALT Oya Jam stats card: 3,362 users with a chart of daily users from 2 to 18 October. 192 games, 132 Nigerian-made, 74% mobile, $0/month infra. Built in 3 days, solo.
Then I did distribution myself: DMs to devs, posts, getting games submitted, and a weekly chart plus embeddable badges so makers bring their own audience back.
There was low ad spend. Most of the growth came from outreach.
This is the work I enjoy most: spot a gap, build it fast, then get it in front of people.
Always happy to talk with anyone building something ambitious. DMs open.
oyajam.com


Insane work ethics, rest bro!

Just listed: Naija Chronicles by @martony_zinx
Test your Naija knowledge. Own the leaderboard.
Play free in your browser: oyajam.com/games/naija-chron…

Marvellous retweeted

Just listed: Naija Chronicles by @martony_zinx
Test your Naija knowledge. Own the leaderboard.
Play free in your browser: oyajam.com/games/naija-chron…

I built a quiz game about Nigeria.
50+ categories. 6,000+ questions. Multiplayer. ₦ wallet. Free. No signup.
It's called Naija Chronicles.
Play here: chronicles.husli.online
Use my code MARTONX9F and we both get ₦50 🧵


It interesting how Naija Farms by @simplypheyie in less than 24hrs topped the 7 days chart of other games released on @oyajam_app.
Goes to show other genres are untapped, execute properly and see adoption.
Try it here: oyajam.com/games/naija-farm

Awesome launch!!!
Wonder what future versions would bring.

The past couple of weeks have been full of creativity on my timeline, so I decided to tap into mine.
My first mini game, Pixel Pop, came out some months ago with the release of my portfolio, for anyone who finds their way there. A few weeks ago at @iqwiki , we launched IQ Arcade, 7 puzzle games that are a lot of fun to play. Now I’ve brought an idea to life in one of my favourite genres: farming games.
This is Naija Farm 🇳🇬🌱
oyajam.com/games/naija-farm
It’s inspired by years of playing Farm Frenzy, Stardew Valley, Green Farm and, to this day, Farm Merge Valley. You can grow crops, raise animals and take them to the market to sell. You can also haggle prices with the traders, build factories, decorate your farm, visit other farmers and so much more.
Play it in your browser, or add it to your home screen and play it like an app. I hope you enjoy it 😊.
Y’all really cooking 😂
No Gree by @GrowthByMikeJay don land on Oya Jam
Area boys, landlords, mosquitoes. You no gree!
Play free in your browser: oyajam.com/games/no-gree?utm…


I don't recommend anyone scramble to move their funds to new wallets today. But we should take the risks to cryptography from AI-accelerated math seriously, and minimize our exposure to not just quantum-vulnerable cryptography, but also potentially AI-vulnerable cryptography.
The core new area of risk from this viewpoint is, unfortunately, ML-DSA / FHE / lattices.
(and it's also another reason, along with quantum, why ECDSA might fall even faster than expected, hence the "fresh address" recommendation)
So far most people have been in the mode of thinking "elliptic curves broken, hashes safe, lattices safe". But there is a good chance that the concrete security of lattices will take serious hits from the next two years of AI math.
The basic threat model is: factoring is something that naively takes 2^(n/2) time, but over decades smart people have found and optimized number field sieves, and degraded that to 2^O(n^(1/3)), which is why RSA keys and signatures need to be ~400 bytes (and not 64 bytes). What if there are skeletons in the closet like that, both for elliptic curves and lattices, that we are simply not smart enough to discover - but bots soon will be?
This is a major part of the reason why for the past year ethereum's lean roadmap has been going in the "hash-only" direction: no lattices, no ML-DSA, no Falcon, no lattice-based commitments inside ZK proofs, etc. Signatures in lean ethereum are all hash-based, either WOTS or SPHINCS-.
For signatures and proofs, we already know how to go hash-only. The bigger challenge is for *public-key encryption* - and this goes far beyond blockchains. Secure communication, anonymizing protocols, lots of things need public-key encryption.
And unfortunately there are long-standing mathematical theorems showing why public-key encryption cannot be done with hashes alone. You have to have some kind of trapdoor object that has at least one form of usable "structure" - either group theory (incl. isogenies) or lattices or code-based or potentially in the future even more newfangled and spooky things (local mixing?). But for anything that has structure, you should assume that AI will make at least some progress in breaking that structure. Here, one reasonable inference is that if you want to make something plausibly long-term secure, multiply the key sizes by 10.
To me that's a very plausible world and something not at all extreme to predict. If AI will bring us 50 years of math in 2 years, then that 50 years of math may very plausibly include a "naive factoring -> GNFS" level of improvement to our ability to break lattices. In that world, lattices will still exist, but they will have to be significantly bigger to guarantee the same level of safety.
And at those new larger sizes, hash-based constructions will beat lattice-based constructions on concrete efficiency in every use case where hash-based constructions are possible at all.
Theoretically, of course it's possible that hashes are broken too (eg. P = NP would imply that). But I think P = NP is very unlikely. And intuitively, it's much more likely that a mathematical object has exactly no exploitable structure (like hashes are intended to), than that a mathematical object has exactly ~3 forms of exploitable structure (for elliptic curves: associativity, Schoof, pairings) and not some secret fourth form of structure we have not yet discovered that greatly degrades its security (for elliptic curves, ECDLP and pairing security). Similar for LWE, SVP, RLWE and the zoo of lattice problems.
For this reason, we do not yet see any reason to worry and start padding the byte size of hashes (if we start to worry more, we would pad the round count first before doing anything to the byte size).
Concrete TLDR, my own personal views:
* Hash-based > lattice-based, in those situations where hash-based is possible at all
* For anything lattice-based, be much more paranoid on param sizes. Remember that blockchains are only a small portion of the cryptography story; this point goes far beyond blockchains and applies to eg. access to websites, secure messaging, Tor / VPNs ...
* For privacy protocols, strongly favor NOT putting encrypted notes onchain. Instead, send them offchain through some third-party mechanism.
* If it's not difficult for you, keeping your funds in addresses which have not yet been used to make a transaction is a good idea. If it's easy for you, do it. **But be careful about migrations; I personally have lost more money in botched migrations than I have lost in all hacks combined**.
* For multisig wallets, doing confirmations offchain is better than onchain, because this way the signatures of signer wallets do not get exposed to the public, so if ECDSA falls to AI much faster than expected, at least the multisig "gracefully degrades" to a 1-of-1 where the 1 is whoever was gathering the signatures - a much better place to be than "anyone can take the money"
firefly.social/post/x/210783…
