

in allah we trust, the rest we test. #OSWE
Nador, Royaume du Maroc
Joined September 2017
- Tweets755
- Following1.6K
- Followers937
- Likes6.6K



Pinned Tweet
Excited to share my journey on discovering my first Remote Code Execution (RCE)!
Check out the article here: mchklt.medium.com/how-i-foun…
#BugBounty #bugbountytips #cybersecuritytips #CyberSecurity

Seems like the @Hacker0x01 agent is taking a break. It's been 30 minutes since I submitted my report and bro still hasn't closed it

15
150
4,932
mchklt retweeted

Myself and @OriginalSicksec , bagged over 6OK-ish $ bounties from this technique in bug bounties, and based on the current supply chain attacks I wanted to share some thoughts
Note: english not my mother tongue so article is enhaced by AI, but content is not an AI slop I promise
poneglyph.cloud/research/uvx…
i reported RCE through @Bugcrowd . A day later, a new version dropped and the bug was fixed. Neither the bot nor @RelentlessT7 flagged it as a duplicate during triage. Yet, after fixing it, the team called it a duplicate and awarded only points. No reward. i felt disappointed!

7
99
4,172
mchklt retweeted

What do security people in Morocco actually earn?
Nobody has the numbers. So we built State of Sec Morocco: an annual, anonymous survey of the field, junior to CISO.
Open results. Open source. 10 to 15 minutes.
stateofsec.ma

seems like a solid xss poc, it gonna keep the triagers mad as fuck 😂😂
#BugBounty #bugbountytips

mchklt retweeted

Ola Bug bounty hunters 😀
DarkEntry’s free Associated Domains feature maps every domain tied to a target — including exposed admin panels.
Type in your in-scope domain, one click, Export All its associated domains as .txt!
darkentry.net
Happy hunting 🙏

mchklt retweeted
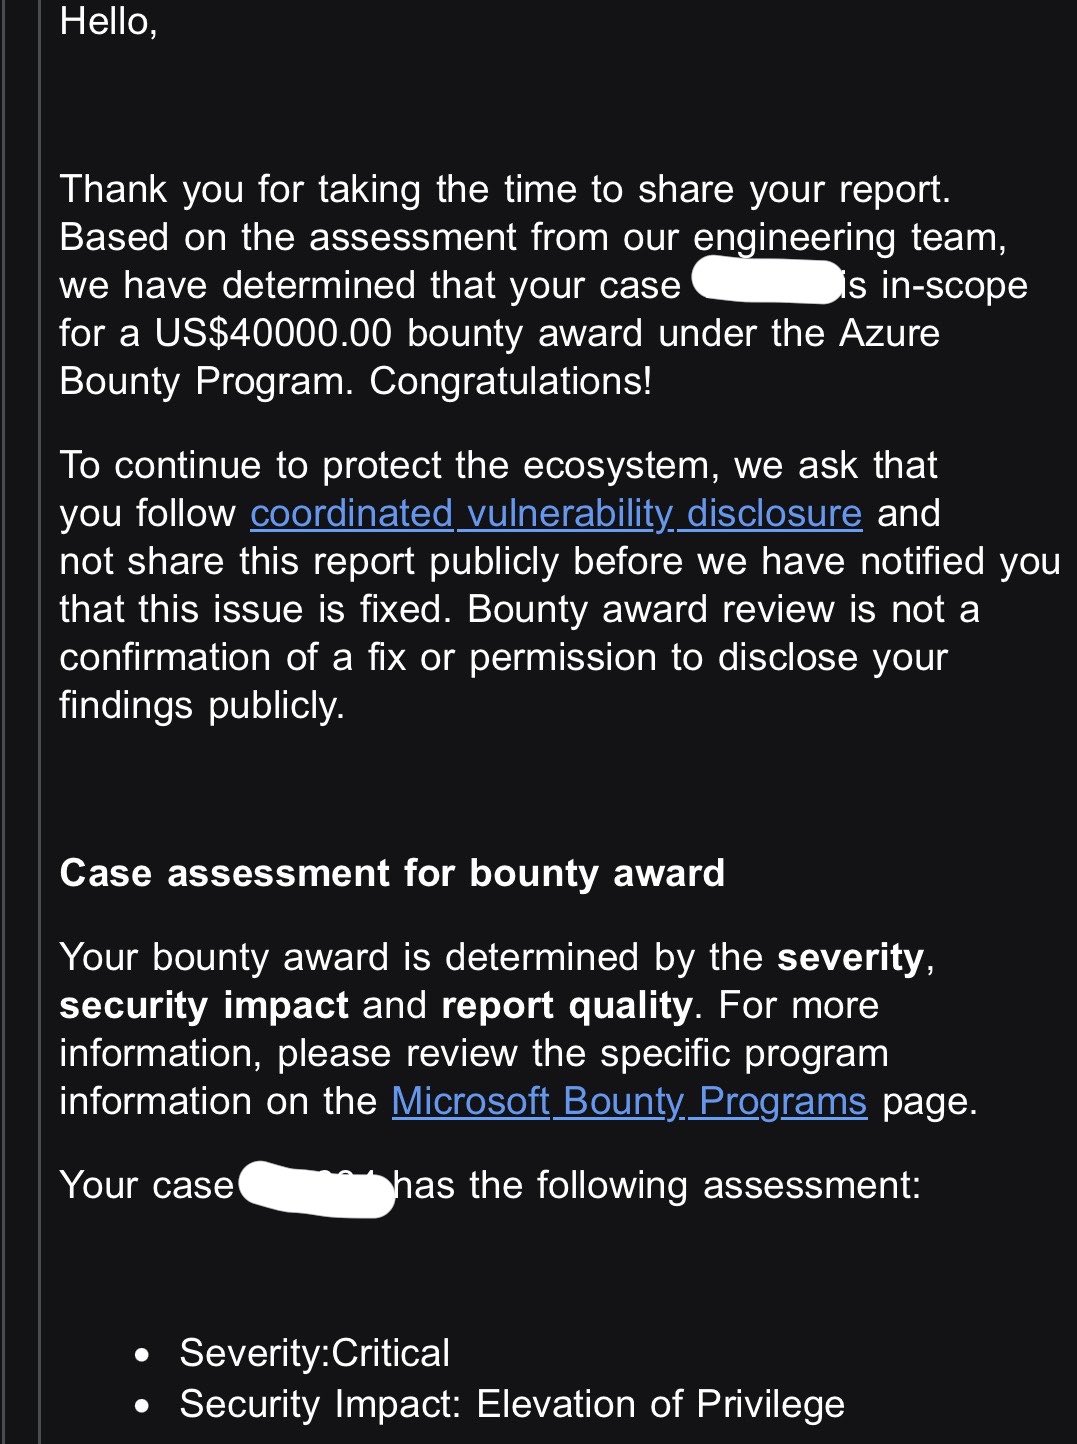
Microsoft’s finding wasn’t my only hit for managed db bugs using AI
poneglyph.cloud/research/man…
And I know its full of em dashes (i wrote initial draft and AI rewrote later)
Besides this managed runtimes/dbs are a good area of research 1/n



Spending 3h to get full ATO then to report it they say you reached the reports limit bro like wtf is that @intigriti let me pay to submit than losing my time then saying i’ve reached the limits 😑
#bugbounty #bugbountytips
2
57
4,007
mchklt retweeted

To solve the issue of "What should I hack next?" and "Is this program worth my time?".
In the last few weeks I've been building bountylens.com
An attack surface intelligence platform that aggregates data and metrics from @Hacker0x01 @yeswehack @Bugcrowd and @intigriti — giving you accurate data about the health, dupe risk, and scope changes of every program and asset.
Everything monitored in real time.
Join the waitlist to try it out: bountylens.com
Feature requests & issues: github.com/bountylens/bounty…
#bugbounty #infosec
Teaser: youtu.be/L94uEr1TMXY


I found 3 potential subdomain takeovers related to Foleon, but the platform is invite-only. If anyone has access, let’s collaborate
#bugbountytips #bugbounty


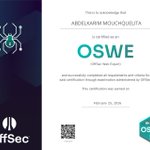
I’ve written a detailed breakdown of my #OSWE journey. It covers the methodology, mindset, and workflows that helped me succeed, all while strictly respecting exam integrity
Dive into the full guide: linkedin.com/pulse/oswe-meth… a summary? lnkd.in/dJHw_qab #InfoSec #PenTesting

mchklt retweeted

In this episode ive shared my small experience in client side hacking, so i hope you guys will enjoy it.
And Thank you @SalhiMahdi72759 for the invitation, i had a really good time recording it.

حلقة جديدة من Hunter Cust 🎙️🔥
أول خطوة لك في عالم صيد الثغرات (Client-Side) تبدأ من هنا 👀
في هذه الحلقة:
كيف تتعلم Bug Bounty بالطريقة الصحيحة
أخطاء المبتدئين
نصائح حقيقية للتطور بسرعة
🎙️ الضيف: @Magn4_
شاهد الآن 👇
youtube.com/watch?v=zdFqr7XL…


mchklt retweeted

New research just dropped by @alien2exe on hijacking OAuth popups via predictable window. open() targets.
The chain uses iframe name collision forcing the auth flow into a controlled context, eventually linking an attacker-controlled addon to leak workspace PII and config data
lab.ctbb.show/research/can-a…