

Applied Security Research | Threat Hunting | DFIR | [email protected] 👁🗨
Joined March 2019
- Tweets81
- Following40
- Followers2.5K
- Likes94

MENASecurity retweeted

Integrating process protection level information into all #EDR #Sysmon events. As suggested by @menasec1 in blog.menasec.net/2022/04/aud…
using Win API instead of checking RunAsPPL registry key (which seem to apply only to lsass)
#dfir #threathunting
github.com/0xrawsec/whids
MENASecurity retweeted
Just pushed the code to embed process protection level in severa events of our #opensource #EDR
#dfir #threathunting
github.com/0xrawsec/whids
thanks to @menasec1 for the idea

MENASecurity retweeted

We just released 1000+ yara rules and 200+ endpoint behavior rules github.com/elastic/protectio…

Hunting for Suspicious Usage of Background Intelligent Transfer Service (BITS)
blog.menasec.net/2021/05/hun…
#ThreatHunting
MENASecurity retweeted

📌How to Design Abnormal Child Processes Rules without Telemetry by @menasec1
[BLOG]➡️ blog.menasec.net/2021/01/how…
#ThreatHunting #BlueTeam #security #DFIR


good understanding of the offensive technique, filtering out normal behavior while in the same time balancing detection resilience, alert context and performance impact are key concepts for detection engineering.
blog.menasec.net/2020/11/how…
Hunting for T1078.003 - Local Accounts and Groups Changes using Sysmon
blog.menasec.net/2020/09/hun…
#ThreatHunting
9
Discovering Windows Registry Symbolic Links using Sysmon
blog.menasec.net/2020/09/dis…

Forensics traces of NTDS.dit dumping using ntdsutil utility blog.menasec.net/2019/11/for… #threathunting #dfir

A starting point to hunt for suspicious usage of Remote Support Tools blog.menasec.net/2019/11/hun… #threathunting #dfir

Interesting DIFR traces of .NET CLR Usage Logs blog.menasec.net/2019/07/int… #DFIR #ThreatHunting #SharpShooter

Detecting Namedpipe Pivoting using Sysmon blog.menasec.net/2019/04/det… … #threathunting #DFIR #sysmon

The negative impact of Network Level Authentication on Windows Failed RDP Logon Events -> blog.menasec.net/2019/04/the… #DFIR #threathunting

[Credential Access] - KeePass.exe credential dumping using KeeFarce.exe can be detected using the following SIGMA rule #ThreatHunting #DFIR #SIGMA


[Credential Access] - short write-up explaining one way to detect malicious programs dumping browser's saved credentials or permanent cookies 👉 blog.menasec.net/2019/04/cre… … #ThreatHunting #DFIR

QRadar SIEM Sysmon App comes by default with almost 80 use cases, for those planning to adopt it, here you can find the needed events mapped to use cases' description 👉goo.gl/hWRCih #threathunting #SIEM #Sysmon #Qradar #DFIR

[Persistence] backdooring domain object to grant the rights associated with DCSync to a regular user or machine account, will allow to re-obtain the pwd hashes of any user/computer (lsadump::dcsync Mimikatz cmd) will leave the follw traces (EIDs 5136 & 4662) #threathunting #DFIR
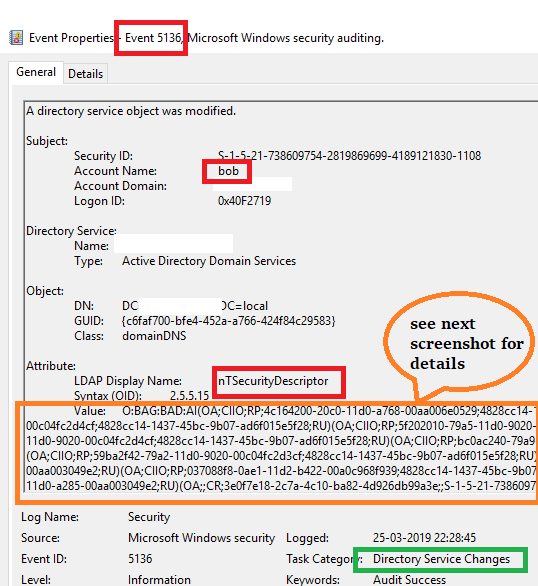


For those interested about those AD Objects DACL, ACEs & Extended rights manipulation techniques (with main purpose to elevate privs and/or persist in plain sight), we urge you to give a read over this excellent whitepaper by @harmj0y & @SpecterOps specterops.io/assets/resourc…
Ifu see 4738 OR 4742 with ALL Changed Attribs equal to "-" (almost 0 in normal behavior), then its strong evidence of DACL based attacks (manipulating ACEs and AD specific Objects's Rights) Powerview\Add-DomainObjectAcl| Set-DomainObject|Set-DomainObjectOwner #threathunting #dfir
