

India's Sovereign AI SOC I Full Stack Cyber Resilience I Built for AI I Digital Defence.
Bengaluru, India
Joined August 2023
- Tweets74
- Following19
- Followers110
- Likes30




Linux KVM flaw (CVE-2026-99312): researchers read ~127 GB of host memory from inside a VM on AMD hosts with nested virtualization. DigitalOcean has patched. Self-managed hosts: install the fixed kernel or turn nested virtualization off.
#CyberSecurity #Linux #KVM #CloudSecurity #Mitigata

Critical Cisco Expressway flaw (CVE-2026-76466, CVSS 9.8): on clustered nodes, an attacker with no login could run commands as root. No workaround. Upgrade to X15.5.20 or later. Cisco knows of no attacks.
#CyberSecurity #Cisco #Expressway #InfoSec #Mitigata

2
220
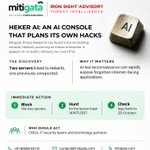
Mitigata found HekerAI, a live AI hacking console scanning an Indian enterprise, with a hidden 2nd server. Block 213.199.49[.]235, 169.58.19[.]2 and hekerai[.]app. Hunt favicon hash 1414712307.
#CyberSecurity #ThreatIntel #AISecurity #HekerAI #InfoSec #Mitigata

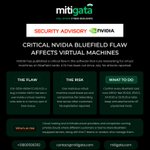
NVIDIA BlueField flaw (CVE-2026-65094, CVSS 9.0): a VM user could break out and affect other tenants. Fixed since July, no attacks reported. Confirm your DPUs are updated.
#CyberSecurity #NVIDIA #BlueField #CloudSecurity #InfoSec #Mitigata

2
98
Windows zero-day SignDrop has public exploit code and no patch. A basic user could become SYSTEM on Windows 11 25H2/26H1 and Server 2025. No attacks reported yet. Next fix due 8 Dec.
#CyberSecurity #Windows #ZeroDay #PrivilegeEscalation #InfoSec #Mitigata

1
48

Critical JetBrains TeamCity flaw (CVE-2026-132891, CVSS 9.8): a pull request from an outsider could run code on the build server with no login. No attacks reported. Upgrade to 2025.11.8, 2026.1.4 or 2026.2.
#CyberSecurity #TeamCity #JetBrains #DevSecOps #Mitigata

32
Mitigata retweeted

Java4Shell (CVE-2026-114938): a flaw inside Java can corrupt server memory with no login, on Java 17.0.6+ and 18+ with newer Intel or AMD chips. Takeover vs crash is debated. Update Java and restart.
#CyberSecurity #Java #Java4Shell #AppSecurity #Mitigata

The scariest part of a cyber incident? Finding out your policy doesn't cover what you assumed it did.
We gave Bhranti Shah, Mitigata's Chief Insurance Officer, 7 cyber scenarios to unpack the difference between being insured and being covered.
How many answers can you guess correctly?
#Mitigata #CyberInsurance #CyberRisk #CyberResilience
From compromised laptops to exposed systems and third-party risks, recent cyber incidents have given businesses plenty to think about.
We picked four worth learning from.
Swipe through. Better to read the headlines than become one.
#CyberSecurity #RiskManagement #Mitigata #CyberResilience


Wondering what the cyber world has been up to this week? 👀
Extortion, espionage, vendor breaches, and compromised developer accounts. Quite a lot, apparently.
Catch it all in this week's 𝗧𝗵𝗲 𝗖𝘆𝗯𝗲𝗿 𝗧𝗶𝗺𝗲𝘀.
#Mitigata #TheCyberTimes #CyberSecurity #CyberResilience

Mitigata retweeted

14 Ransomware victims confirmed in India over the last 24 hours! 🤯
threatometer.com
#threatometer @mitigata


Remember refreshing Worldometer during COVID to see how fast it was spreading? Cyber attacks are the new pandemic, and now they have their own live counter.
Every day, new vulnerabilities get exploited and new breaches surface across the globe. Most teams hear about them too late, or from unverified sources.
So we built ThreatOMeter: a free, real-time threat monitor that gives you verified updates on ongoing cyber attacks worldwide. CVEs, exploits, breaches and research with advisory, scored and mapped so you know what matters right now.
threatometer.com/
@mitigata

Not every access request gets approved. This one just did.
Mitigata has joined @AnthropicAI 's Cyber Verification Program, gaining access to 𝗖𝗹𝗮𝘂𝗱𝗲 𝗠𝘆𝘁𝗵𝗼𝘀.
The program supports verified cybersecurity teams with advanced AI capabilities for vulnerability research, threat investigation and authorised security testing.
#Mitigata #Anthropic #ClaudeMythos #CyberResilience

1
81
Outlook zero-day under active attack (CVE-2026-124194): opening one crafted email file can leak your Windows password hash. Update Office, not just Windows, and block outbound SMB (ports 445 and 139).
#CyberSecurity #Outlook #Microsoft365 #ZeroDay #Mitigata

1
3
989
Critical MongoDB flaw (CVE-2026-118383, CVSS 9.5): an attacker with no login can set up a memory error that crashes a replica set. Login alone doesn’t stop it. Upgrade to a fixed version.
#CyberSecurity #MongoDB #DatabaseSecurity #InfoSec #Mitigata

1
87
Microsoft has fixed 3 critical cloud flaws: Entra Device Registration (CVSS 10), Azure Managed Grafana and Azure OpenAI (both 9.8). Nothing to patch, but review access and rotate keys.
#CyberSecurity #Azure #MicrosoftEntra #AzureOpenAI #CloudSecurity #Mitigata

82
𝗔𝗜: “What can I help you with?”
𝗨𝘀: “Let's start with security.”
And now, that conversation just got a little more interesting.
𝗠𝗶𝘁𝗶𝗴𝗮𝘁𝗮 𝗶𝘀 𝗽𝗮𝗿𝘁 𝗼𝗳 𝗖𝗹𝗮𝘂𝗱𝗲'𝘀 𝗖𝘆𝗯𝗲𝗿 𝗩𝗲𝗿𝗶𝗳𝗶𝗰𝗮𝘁𝗶𝗼𝗻 𝗣𝗿𝗼𝗴𝗿𝗮𝗺.
@AnthropicAI @claudeai #Mitigata #AISecurity #CyberSecurity

2
206
Mitigata retweeted
Remember refreshing Worldometer during COVID to see how fast it was spreading? Cyber attacks are the new pandemic, and now they have their own live counter.
Every day, new vulnerabilities get exploited and new breaches surface across the globe. Most teams hear about them too late, or from unverified sources.
So we built ThreatOMeter: a free, real-time threat monitor that gives you verified updates on ongoing cyber attacks worldwide. CVEs, exploits, breaches and research with advisory, scored and mapped so you know what matters right now.
threatometer.com/
@mitigata
4 flaws to act on this week: Chrome (already exploited), SAP Web Dispatcher (CVSS 10), Hitachi HiRDB (CVSS 9.8) and a WordPress upload plugin with no patch yet. Update Chrome first.
#CyberSecurity #Chrome #SAP #WordPress #InfoSec #Mitigata
