

Strategic Advisor | AI, Security Doctrine & FinOps
Joined January 2012
- Tweets4.4K
- Following238
- Followers5.1K
- Likes2K




Pinned Tweet
practise humility & do the right thing. if fast fwd say u're 90 years old.. would u be proud with what u're doing now? if not, change it.
Mohd Atasha retweeted

🚨 单单一个被投毒的脚本,在一天之内击中了至少25个国家的178个大品牌。以下是每一方的遭遇:
🇺🇸 美国 — Zoom、CNN、福克斯新闻、NPR、Peacock、Salesforce和Equifax向自家访客推送了窃取银行卡信息的代码,汇丰美国也遭感染
🇬🇧 英国 — BBC最先中招,而TalkTalk是当晚最后一个仍受感染的网站
🇫🇷 法国 — 法航荷航集团和加密钱包制造商Ledger推送了会调包钱包地址的代码
🇦🇺 澳大利亚 — 汇丰、沃达丰、TPG Telecom和Rest Super:大规模扩散,一个国家就有4个大牌
🇭🇰 香港 — 汇丰和恒生投资遭到感染,银行业是受打击最严重的行业,共32家公司
🇳🇱 荷兰 — 荷航遭到重击,荷兰银行和ICS Cards遭感染
🇲🇽 墨西哥 — 汇丰中招(是整份名单中扩散范围最大的银行:11个市场)
🇸🇬 新加坡 — 汇丰和Levi's中招;攻击者当天暗中将代码重建了26次(Report URI)
🇨🇦 加拿大 — Equifax、CTV新闻和星巴克中招
🇦🇪 阿联酋 — 汇丰中招
🇲🇾 马来西亚 — 汇丰中招
🇹🇼 台湾 — 汇丰中招
🇻🇳 越南 — 汇丰被同一脚本直接击中
🇵🇭 菲律宾 — 汇丰中招
🇪🇬 埃及 — 汇丰中招
🇫🇮 芬兰 — S-Pankki中招
这些公司中没有一家是自己的服务器被攻破的。
恶意软件是通过Optimizely Web进来的,这是宜家、GitLab和其他所有公司都在每个页面上加载的一款测试工具。
它窃取银行卡号。它调包加密钱包。在较旧的iPhone上,它试图加载2套黑客工具包。
CNN和BBC自己就在这份名单上。
我发布这类黑客事件时会保留每一个名字,不经任何公关过滤。关注我。
Mohd Atasha retweeted

We are deeply sorry for the disruption this incident has caused our customers and partners. We know the trust they place in our services and take that responsibility extremely seriously. We are seeing broad recovery and stability across our services.
This was a technical issue not related to cyber or AI / agents. The incident was introduced by an issue during an earlier network capacity upgrade that surfaced following a recent network change. We have addressed the underlying issue and continue to restore service to remaining customers and regions.
Given the scale of demand, we restored services gradually, validating stability at each stage. While this took longer, it helped ensure a stable restoration.
We will provide a full post-incident report once our review is complete.
Mohd Atasha retweeted

BREAKING:
BBC has developed a secret emergency broadcasting plan to keep the UK informed if a major blackout or cyberattack shuts down electricity, internet and communication networks.
Around 100 BBC staff will operate a special emergency radio studio with independent power, food, water and fuel supplies to keep broadcasts running for at least three days.
The plan relies on FM radio, which can continue operating even when internet and mobile networks go down.
The UK is also preparing for a potential nationwide crisis, with officials urging the country to be ready to withstand a major disruption for at least 72 hours.
Mohd Atasha retweeted
ドコモ顧客情報流出、本人確認書類の番号も 前田社長が謝罪
nikkei.com/article/DGXZQOUC0…

Johor hosts two of the world's top 10 AI data centres, making Malaysia an unexpected global tech compute powerhouse.
says.com/my/tech/tech-news/m…
#johor #malaysia

33
Mohd Atasha retweeted
BREAKING:
This morning’s cyberattack against supermarket fridges and freezers has now spread to Belgium, Sweden, Luxembourg and Estonia.
The hackers increased the temperature up to 50C. Food worth millions of euros has been spoiled.
Experts warn that such cyberattacks on supply chains and logistics can constitute a threat to national food security in many Western states.

Mohd Atasha retweeted

🚨 GitLab: remote code execution via crafted regex in CI/CD config (CVE-2026-97229)
Exploited in the wild (CISA KEV) · EPSS 0.18
Patch → 19.2.8, 19.3.5 and more
cve.now/CVE-2026-97229

Mohd Atasha retweeted

🇲🇾 🚨 RHYSIDA RANSOMWARE CLAIMS MALAYSIAN SHIPPING GIANT MISC GROUP
The Rhysida ransomware group has listed MISC Group, the Malaysia-based energy shipping and maritime services company, on its leak site.
The gang claims to hold about 29,800 files (28.4 GB), allegedly from onboard vessel workstations. It says the haul includes PST mail archives, crew records with passport numbers and employment contracts, shipboard system and account credentials, internal investigation and incident reports, audit findings, and drydock and charter documents.
MISC has not commented publicly, and the claim has not been independently verified.
⚠️ Analyst Note:
If genuine, leaked shipboard credentials could expose vessel navigation, security and communication systems, and crew data could fuel identity fraud. Seafarers should watch for crew-agency or payroll-themed phishing, and maritime operators should rotate onboard and shore credentials. Unverified threat-actor claim, NOT confirmation of a breach.
#DDW #DarkWeb #Rhysida #Ransomware #MISC #Malaysia #Maritime #Shipping #CriticalInfrastructure #ThreatIntelligence #CyberSecurity

Mohd Atasha retweeted

Masayoshi Son of SoftBank Group Corp. chose locations in Malaysia for $50 billion in technology investments, the country’s prime minister said, an outlay that would accelerate the billionaire’s global bet on AI infrastructure. bloomberg.com/news/articles/…

Mohd Atasha retweeted

Evolving threat 🚨 CVE-2026-111497, previously known to affect Node.js (node2shell) and Python has evolved into “HTTP2Shell.”
A significant blast radius.
This vulnerability leaves many libraries and applications using HTTP vulnerable to pre-auth RCE via Brotli decompression.
Please be aware. Fixes not yet available for all affected services. Look for Brotli (1.2.1) dependency upgrades when they become available.

Mohd Atasha retweeted

🚨 Do you understand what happened in the last 48 hours..
> PHP, the code behind 69% of all websites, got 2 holes rated 9.2 out of 10, and the US, the UK and Japan told site owners to patch or go OFFLINE.. 4 days after hackers had already started trying the flaw..
> Japan's Prime Minister posted the request late at night.. the Finance and Health ministries pulled pages, MUFG Bank and JR West went into emergency maintenance, and Onamae shut ALL Desktop Cloud plans after malware hit up to 26,739 customer servers..
> India's eMudhra was caught with 8 intermediate certificate keys so weak one of them was literally the number 4.. the 60,000,000+ certificates it has issued can't be trusted..
> GitLab disclosed a 10.0 severity hole in every version since 2014.. the maximum score there is..
> criminals were caught using a literal AI hacking tool on 1,200+ sites.. it broke into more than 100 companies including John Deere and Cummins..
> LiteLLM, an AI tool with about 23,000,000 downloads a week, was secretly poisoned with a password stealer.. the bad version sat on PyPI for about 2 hours..
> State Bank of India, the country's biggest bank, confirmed 3,897 customer records on the dark web..
> WIRED now calls the PHP flaw "broadly exploited".. nearly 55,000,000 web properties still run PHP..
every single government on this list told PHP site owners the same thing within the last 48 hours.. patch it or take it offline..
all of this.. 48 hours..
if you're not following me you're finding out about this 48 hours late from someone who read my post..
it's only getting crazier from here..
Mohd Atasha retweeted

Effective Immediately, all organizations using PHP for their systems are advised to be prepared for an update addressing two critical vulnerabilities. PHP is widely used for web applications. These vulnerabilities often provide a direct path to the server's file system or database. If an immediate update is not feasible, it is recommend that organizations take the system offline until it can be fully mitigated. NSA will follow up shortly with more specific guidance.
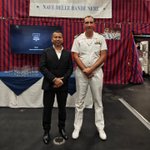
a closer look aboard ITS Giovanni delle Bande Nere, the Italian Navy’s multi-purpose combat ship.
a pleasure to be hosted by Commander Lorenzo Malandrucco, with the visit facilitated by the Embassy of Italy in Malaysia.
🇲🇾🤝🇮🇹


56
Mohd Atasha retweeted

Joint Statement by the Foreign Ministers of Türkiye, Algeria, Indonesia, Jordan,
Lebanon, Malaysia, Mauritania, Pakistan, Palestine, Qatar, Saudi Arabia and
Somalia, 21 August 2026 – at Putrajaya Federal Territory, Malaysia

Mohd Atasha retweeted

Statement | Foreign Ministers of Qatar and seven Arab and Islamic countries condemn Israel’s continued illegal settlement policies in the occupied Palestinian territory and reaffirm their rejection of the “E1” settlement plan
Doha | 21 August 2026
The Foreign Ministers of the State of Qatar, the Hashemite Kingdom of Jordan, the United Arab Emirates, the Republic of Indonesia, the Islamic Republic of Pakistan, the Republic of Türkiye, the Kingdom of Saudi Arabia, and the Arab Republic of Egypt, unequivocally condemn Israel’s continued illegal settlement policies in the Occupied Palestinian Territory and categorically reject the “E1” settlement plan and related settlement activities east of occupied East Jerusalem. They further reiterate their condemnation of the violations and acts of violence perpetrated by settlers, with the support of the Israeli occupying authorities, against the Palestinian people and their property. They stress that such acts in no way diminish the inalienable rights of the Palestinian people and constitute violations of international law and relevant United Nations resolutions, while posing a serious threat to regional and international peace and security.
The Ministers warned that the “E1” settlement plan constitutes a dangerous escalation that further advances settlement expansion and annexation and undermines the geographical contiguity of the Occupied Palestinian Territory, particularly between the West Bank and East Jerusalem, thereby threatening the viability and realization of an independent, contiguous Palestinian State based on the 1967 lines with East Jerusalem as its capital. Such actions constitute a direct challenge to international efforts aimed at achieving peace, foremost among them President Donald Trump’s Comprehensive Plan, including its unequivocal rejection of annexation and forced displacement, and the mechanisms envisaged for its implementation, including through the Board of Peace, as well as President Trump’s firm commitment to not allow annexation of the West Bank, with a view to achieving stability and bringing the conflict to an end.
The Ministers reaffirm that the two- State solution, in accordance with international law and relevant United Nations resolutions, remains the only viable path towards a just, comprehensive and lasting peace. They warn that actions aimed at undermining this solution risk further escalating tensions, threatening regional and international peace and security, and jeopardizing prospects for lasting peace and stability in the region.
In this context, the Ministers support all efforts aimed at ensuring accountability, including through appropriate international measures and sanctions against entities and individuals responsible for illegal settlement activities, including the “E1” settlement plan, as well as those supporting, facilitating or implementing policies of settlement expansion and annexation. They further call for an end to any support or financing that contributes to the establishment, expansion or entrenchment of illegal settlements. They stress that the lack of accountability contributes to the continuation of violations and further undermines prospects for a just and comprehensive peace.
The Ministers call for immediate action to halt the “E1” settlement plan, rescind all measures taken in connection with it, and cease all settlement activities and other measures aimed at altering the geographic and demographic character of the Occupied Palestinian Territory. They further call upon the United Nations Security Council, all States and relevant international actors to uphold their responsibilities under international law and take urgent and effective measures to halt illegal settlement expansion, and to ensure the protection of the Palestinian people, safeguard their inalienable rights, including their right to self- determination, and realize their independent State, in accordance with international law and relevant United Nations resolutions.
#MOFAQatar

I welcome this clear and principled joint position.
Upholding international law, protecting civilians, and preserving the viability of a two-state solution remain essential to any credible path towards a just and lasting peace.
#TwoStateSolution #PeaceAndSecurity #WestBank

Joint statement from the leaders of the United Kingdom, France, Germany, Italy, Netherlands, Norway and Canada.

ALT Joint statement from the leaders of United Kingdom, France, Germany, Italy, Netherlands, Norway and Canada. Read full statement here: https://www.gov.uk/government/news/joint-statement-on-israeli-governments-decision-to-publish-construction-tenders-for-the-e1-settlement-project
26
Projek Edgewing usahasaman antara BAE, Leonardo & JAIEC. Kontrak $6.1 Billion
astroawani.com/berita-dunia/…
25
AI can automate hacking methods, but it’s still not good at creating entirely new kinds of attacks.
15