

Dad / Husband / Marine / Student / Teacher / @Hak5 / @NoVAHackers / @SiliconHBO / @NationalCCDC / @MARFORCYBER Auxiliary
The Internet
Joined February 2007
- Tweets33.5K
- Following24.8K
- Followers77.9K
- Likes5.3K




Pinned Tweet
If you have ever learned anything from me at all. I challenge you to pay it forward. I didn’t get to where I am by standing on the shoulders of giants, I got here by learning tidbits from hundreds of tweeters, bloggers, podcasters & presenters who chose to share their knowledge.
Rob Fuller retweeted

hashcat v8.0.0 released!
The largest update in the history of hashcat, with PCFG attacks, hash recipes that crack hashes without a hash-mode, and bcrypt on FPGA boards.
Release notes: github.com/hashcat/hashcat/b…
Download: hashcat.net/hashcat/

Rob Fuller retweeted

Syswhispers4
github.com/JoasASantos/SysWh…

Rob Fuller retweeted

I wrote up a way to defeat enforced SMB signing for relay.
It abuses a documented SMB re-authentication behavior.
I'm surely missing nuance and prior art. Corrections welcome.
Writeup:
blackfield.ch/blog/defeating…
PoC:
github.com/aas-n/reauthx

Rob Fuller retweeted

Its me, I have a working PoC with the infoleaks to bypass ASLR. It took a lot of prompting and re-iterating to find those, tested against PHP 8.5.11 x86_64 with with all defaults and tested over the Internet

Rob Fuller retweeted

@BSides_NoVA OCT 31st Keynote: @mubix
Stories from the Red Side
Creating tools, wielding donuts, walking on water, etc.
With 25 years of experience, Rob's been though crazy situations.
And we're gonna hear about it!
Info: bsidesnova-2026.sessionize.c…
Tickets: eventbrite.com/e/bsidesnova-…

Rob Fuller retweeted

It’s hard to believe 11 years have passed since @gentilkiwi encouraged me to open-source DSInternals and start tweeting about my research, with him being my very first Twitter follower. Thank you, Benjamin! #MyXAnniversary

PastySpace - dead simple modern pastebin that runs in docker, and easy URLs to type URLs. I Ai'd it because I couldn't find something to move files and clipboards around to other systems easily.
github.com/mubix/pastyspace
pastyspace.com/

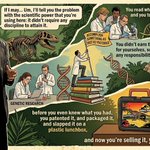
Every time I hear about the advances in Ai and the fears about what it could do and what it is doing to society, I remember this quote from Jurassic Park 1:

Rob Fuller retweeted

1/4 NetScaler exploitation IOCs (CVE-2026-88771 suspected) 🚨
Sharing detection info from a failed exploitation attempt seen on 22 Sep. Unauthenticated, two-stage, fully automated. Shared for detection only, so you can check your own logs.
#NetScaler #Citrix #DFIR
Rob Fuller retweeted

We’re doing this again. hobocon 3 is coming.
hobocon 2 put 68 hackers, makers, radio nerds, and assorted weirdos in one train car.
For hobocon 3, we’re planning at least twice the nonsense: two train cars and 136 people.
Interest form: hobocon.com

Rob Fuller retweeted

ScreenConnect is 74.5% of the abused remote-access tools @HuntressLabs sees.
So I detonated two real samples and hunted both on Defender and Elastic. Full hunt notes and every query in the Article.


Made a Golang port of it heavily using AI to do so: github.com/mubix/ntlmscout-g… - workflow built out most of the binary versions someone would need.
Amazing concept and work by @BoydHacks


Just released ntlmscout, a single-file, zero-dependency recon tool for internet-exposed NTLM endpoints. Combines the best parts of several tools all in one.
Decodes the Type-2 challenge across HTTP/SMB/MSSQL/mail/LDAP/RDP, recovers the internal IP (OXID, IIS host-header, cert SANs), flags DCs, and sprays lockout-safe.
Hack the Planet!
github.com/boydhacks/ntlmsco…

Rob Fuller retweeted

great stuff mate, I did something similar: github.com/stratomarco/ai-tr…

Added more training to the AI-CTF (it won't be fast but you can run this on a halfway decent laptop) - github.com/mubix/ai-ctf
It teaches prompt injection and other paths prompt injection can take. All the answers are in the repo so it isn't about getting the flags but learning.

Finally had some time to update IOXIDResolver thanks to a few people submitting changes/issues: github.com/mubix/IOXIDResolv…

Rob Fuller retweeted

ItsNotAlwaysSMB: DPAPI in other protocols🔥
SMB is monitored closely nowadays, stopping attacks like looting DPAPI secrets. Thanks to @_zblurx, NetExec got a huge upgrade, extending DPAPI credential dumping to other protocols such as WMI, WinRM and MSSQL and various modules🔑

ALT Dumping DPAPI secrets via WinRM, MSSQL and WMI

ALT Dump various credentials using DPLoot
Rob Fuller retweeted

Friday afternoon (vibe)coding project that was on my to-do for a while: obtaining Entra ID tokens from an endpoint by asking the WAM. This alternative to using the PRT cookie follows the legitimate SSO flow used by apps like Teams to obtain tokens. Code: github.com/dirkjanm/askWAM

Rob Fuller retweeted

Outflank's ntlmrain takes Google's ~8 TiB NetNTLMv1 rainbow tables and losslessly compresses them to ~3.99 TB using globally sorted endpoints, packed 39 bit chain starts, delta encoding + Rice-16 coding, and a global GIDX index.
The result is ~1 min SSD table lookups, WebGPU-accelerated DES precomputation/verification, and ~7 min end-to-end cracking on an RTX 4070 Ti.
More Explanation in their blog: outflank.nl/blog/2026/09/08/…
Github tool: github.com/outflanknl/ntlmra…
NTLMRain Table: lookup.ntlmrain.com
#NetNTLMv1

Made a Cybersecurity Resume Reviewer AI skill that I've been using for some mentees, made it public for anyone who is interested in using it as well. Hope others find it useful (also open to feedback or pull requests). github.com/mubix/cyber-resum…

