Security Researcher. Infosec. 😝 Share what you know, learn what you don't. =[ https://teapawt.net/t.co/dK4hcFyN8z ]=
Internet
Joined October 2016
- Tweets191
- Following62
- Followers169
- Likes429
Pinned Tweet
Updated #MalwLess for sysmon v8.
Now you can add RuleName field in rule sets.
#Sysmon #DFIR #BlueTeam
github.com/n0dec/MalwLess/re…


Javier Ruiz retweeted

Are you passionate about finding new #malware? The renowned AT&T Alien Labs Threat Intelligence team is looking to add to their research team to help design the next gen of threat protection and uncover new threats. Here’s more information - go.att.com/bf064462


Javier Ruiz retweeted

Get ready for the SEVENTH ANNUAL FLARE-ON CHALLENGE!!!! Starts on Friday, September 11, 2020 #flareon7 @FireEye @Mandiant fireeye.com/blog/threat-rese…

Javier Ruiz retweeted

Updates for Sysmon (v11.0), Coreinfo (v3.5), Process Explorer (v16.32) and LiveKD (v5.63) have now been posted!
See what's new directly from @MarkRussinovich in his video update: youtube.com/watch?v=_MUP4tgd…
Get the tools at sysinternals.com

Javier Ruiz retweeted

We just released Cutter v1.9 on #r2con2019 with a HUGE surprise -
a full integration of Ghidra decompiler in Cutter! 🥳
Download v1.9 with the Decompiler from cutter.re
For more info, keep reading >>

Finished #flareon6 😊😊
Thanks to @FireEye and all the FLARE team for these amazing challenges.

Javier Ruiz retweeted

Defeating Commercial and Custom Packers like a Pro - VMProtect, ASPack, PECompact, and more: youtu.be/N4f2e8Mygag?t=1
Javier Ruiz retweeted

InfinityHook sample is live, please consult the readme. Massive kudos to @0xNemi for incredible code clean-up. Microsoft says this is not security issue, have fun.
github.com/everdox/InfinityH…


Javier Ruiz retweeted

Osquery for Windows local privilege escalation
offsec.provadys.com/osquery-…

Javier Ruiz retweeted

I've finally got around to completing my first post on reversing #ISFB, specifically, unpacking and analyzing the first stage loader (executable):
0ffset.net/reverse-engineeri…
As always, all samples mentioned have been uploaded to @virusbay_io


Javier Ruiz retweeted

New blog post! Building an Office macro to spoof parent processes and command line arguments blog.christophetd.fr/buildin…


Javier Ruiz retweeted
1250 lines of Java later, I ported one of my abstract interpretation-based deobfuscation tools (msreverseengineering.com/blo…) to Ghidra:

Javier Ruiz retweeted

📢 Quick Tip Tutorial Video 📢
Have you noticed x64dbg is crashing when you try to analyze recent malware samples?? We explain why, how we worked around it, and their fix in the new release of the debugger!
youtu.be/FNuFlhnfZQU
#malware #x64dbg #OpenAnalysisLive


Javier Ruiz retweeted

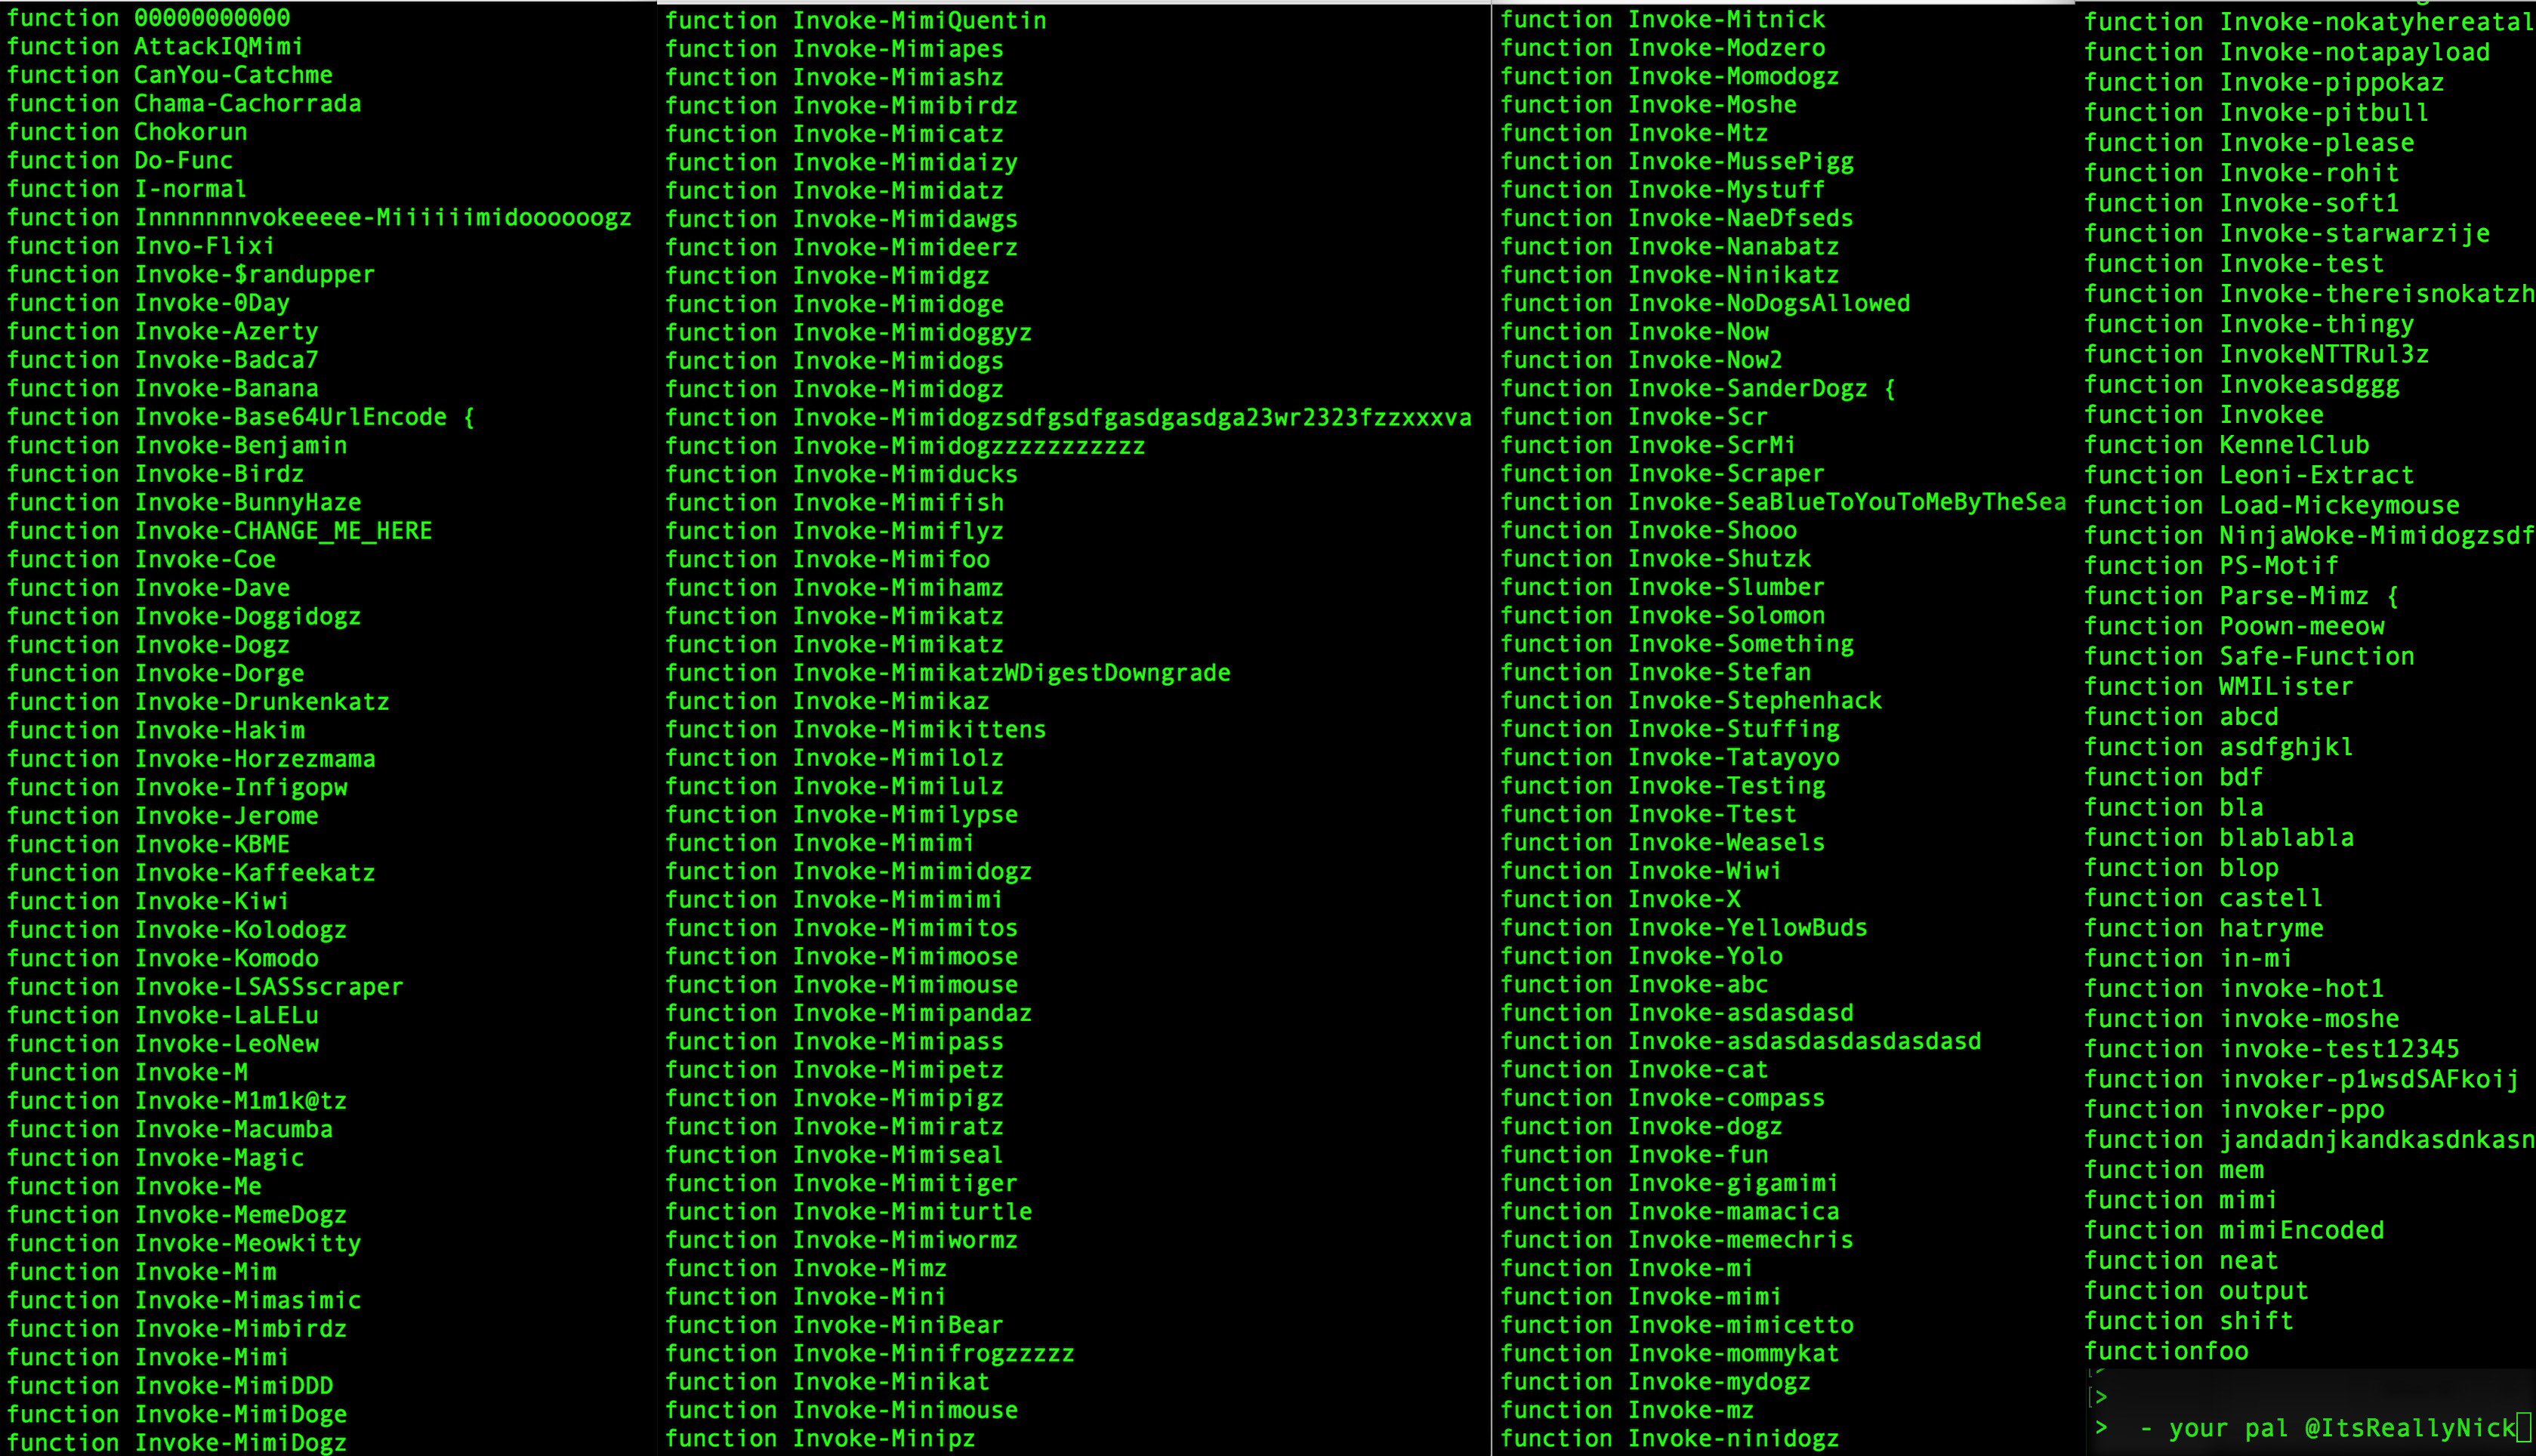
🆕 Now with almost 700 🥝 samples!
Pictured: head -1 <667 samples of invoke-mimikatz> | sort -u
⚠️ Attention #redteam: Did any of you make the list? 🐑 Some of these are great!
📜 Full list with counts: gist.github.com/itsreallynic…
🏆 Which is *your* favorite?
I have a few...