
Aficionado a la seguridad informática, análisis forense, DFIR y hacking ético. Cacharreando con Windows y sus internals. @neosysforensics@infosec.exchange
Joined January 2011
- Tweets11.5K
- Following623
- Followers1.7K
- Likes2K





neofito retweeted

What's up pisha? Prompt Injection con Jailbreak en Grok 3 y 4 m3n0sd0n4ld.github.io/patoHa…
#AI #LLM #Grok #promptInjection #jailbreak
neofito retweeted

1/2
LDAP signing was supposed to stop NTLM relay to LDAP. I found a way to relay coerced SMB auth to a DC with LDAP signing and channel binding enforced.
Patched in October.
Blog: specterops.io/blog/2026/10/2…
PoC: github.com/grayhatkiller/swi…

neofito retweeted

what if we just automatically patched security vulns directly in the bins
trufae.substack.com/p/securi…
neofito retweeted

Si vous avez téléchargé aujourd'hui la dernière version de CLI d'OVHcloud, merci de la mettre à jour à nouveau très rapidement. Sinon effacer. Il s'agit de repo:
github.com/ovh/ovhcloud-cli
La version CLI de 14h47 a été compromise par un hacker. Nous l'avons détecté et bloqué à 16h21. Merci au client qui nous a remonté le souci. La version compromise est v0.11.0 v0.12.0 v0.13.0 v0.14.0 v0.15.0.
La version v0.10.0 et la future 0.16.0 est clean.
On vient de finit les premières vérifications et aucun autre repo n'est affecté. Nous avons aussi retracé l'incident. Le hacker a utilisé le compte github d'un des développeurs et a ajouté un binaire dont le job est récupérer les secrets sur le disque. La qualité du binaire est médiocre mais il peut aller jusqu'au bout. Si vous êtes concernés, merci de changer tous les secrets sur votre disque.
On continue les recherches sur le binaire et on va publier les détails additionnels sous peu.


neofito retweeted

Blogpost acerca de como explotar el CVE-2026-81963 con la explicacion del diff y el codigo de un poc basico funcional que eleva a SYSTEM, que por supuesto mejoramos muchisimo en el exploit que releaseamos para Core Impact, pero servira para entender por donde va la cosa.
coresecurity.com/blog/cve-20…
neofito retweeted

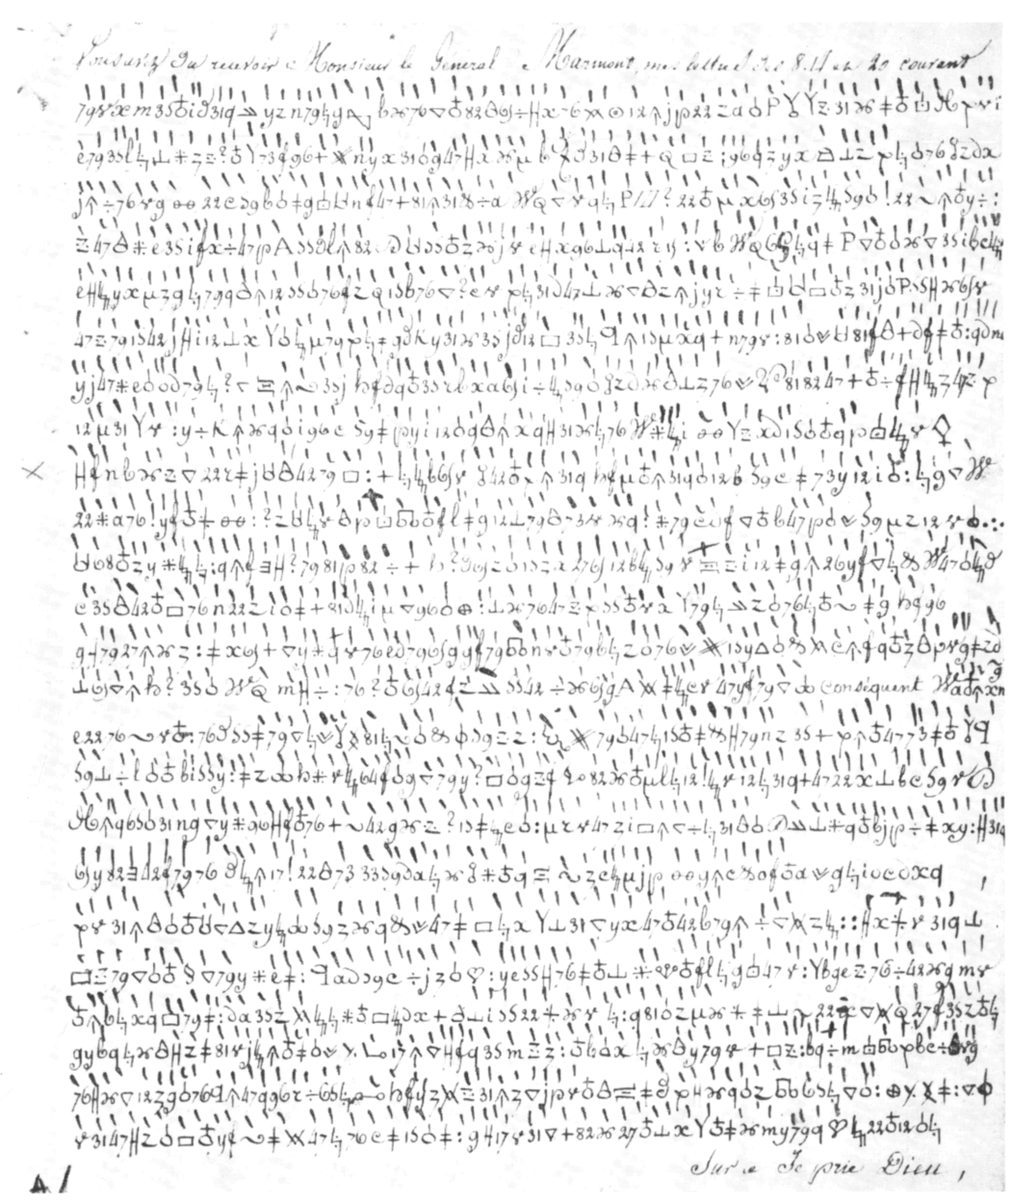
I used GPT-6 Astra to break an unsolved cipher to one of Napoleon's generals that had gone unread for 217 years.
What makes this impressive isn't actually the codebreaking, but that Astra completed the entire multi-modal workflow in ~6 hours from a single image and goal.
1/6🧵
neofito retweeted

Un grupo de aficionados a la ciberseguridad hemos creado un nuevo capítulo de @owasp en Valencia (España). Si queréis participar en esta nueva comunidad, podéis visitar la web owasp.org/chapters/valencia y uniros al canal #chapter-valencia en el Slack de OWASP owasp.org/slack/invite

neofito retweeted

NetNTLMv1 is dead. Long live NetNTLMv1. 🌈
Today we're releasing NTLMRain: recovering NT hashes from NetNTLMv1 responses.
🌐 Browser-based cracking
⌨️ Cross-platform CLI with GPU/CPU support
💾 Searchable tables that fit on a 4 TB disk
Read the blog: outflank.nl/blog/2026/09/08/…

neofito retweeted

For a long time, I thought the moat in pentesting was technical excellence: "hire the best hackers and customers will come".
I still think it matters, but the answer is more complex.
I'd be keen to hear what you think the real moat is:
pentesterlab.com/blog/what-h…

neofito retweeted

A couple of days ago, I did a quick explainer on Claude’s new watermarking process and implementation. Since it’s such a popular topic and sparked such a lively discussion, I thought it might be interesting to go into a bit more detail when explaining how it works.
So, instead of the usual text article, I recorded a little lecture on the topic (to change it up a bit from my usual articles).
It ended up a bit longer than intended, but I hope it clarifies a lot of things:
- Sampling the next token in an LLM and pseudorandom number generators
- How watermarking relates to the regular LLM sampling process
- Whether watermarking makes text "worse"
- How to remove watermarks
- Tournament sampling
- How new text is checked for watermarks without rerunning the LLM
I ended up with ~50 slides, but I hope that these explain it well, though! Happy watching!


neofito retweeted
Check out first images of the start of the total solar eclipse in Spain: flic.kr/s/aHBqjD2dKZ More will be posted throughout the day! The total solar eclipse will be visible in parts of Greenland, Iceland, northern Russia, the Atlantic Ocean, Spain, and a small corner of Portugal. @NASA is streaming the eclipse live with views across the path and interviews with subject matter experts: nasa.gov/live

ALT The Moon is seen passing in front of the Sun during a solar eclipse from San Millán de los Caballeros, Spain, Wednesday, Aug. 12, 2026. A total solar eclipse swept across parts of Greenland, Iceland, northern Russia, the Atlantic Ocean, Spain, and a small corner of Portugal. A Partial eclipse was visible in parts of the U.S., most of Canada, much of Europe, and northwest Africa. Photo Credit: (NASA/Bill Ingalls)

neofito retweeted

Hoy hemos liberado Didacta,
Una plataforma educativa Fair-Code que hemos creado directamente para sustituir a Moodle.
Modular, de verdad.
Tecnología actual.
AI First.
Cumplimiento con RGPD, AI Act, ...
Módulo de implementación FUNDAE desde el inicio.
Y de libre uso.
👇

neofito retweeted

The board of directors panicked after reading an article in Forbes and hired a boutique cybersecurity firm.
They paid $80K for a team of external auditors to stress-test our network architecture.
A guy named Connor showed up to my office with a customized laptop covered in hacking stickers.
He ran a preliminary port scan and immediately found 14 open vulnerabilities on our primary subnet.
He barged in and demanded to know why our main firewall was running outdated firmware from 2014.
I leaned back in my Herman Miller Aeron chair and smiled like a disappointed father.
I told him he had successfully discovered the outer layer of my decentralized honeypot matrix.
I explained that we intentionally leave legacy ports open to trap malicious actors in an infinite digital loop.
I used the phrase "asymmetrical threat inversion protocol."
He stopped typing on his mechanical keyboard and looked deeply confused.
I told him that patching those obvious vulnerabilities would immediately signal to international syndicates that we were a high-value target.
I said that by maintaining the illusion of baseline incompetence, we achieve absolute digital camouflage.
I asked him if his boutique firm didn't understand the fundamental concept of psychological network warfare.
He started aggressively backpedaling and nervously closing terminal windows on his screen.
He said his scan was just a preliminary assessment and he didn't want to disrupt my advanced architecture.
I generously offered to sign off on his security audit if he classified our vulnerabilities as strategic perimeter decoys.
He rewrote his 40-page compliance report to praise our innovative approach to threat management.
The CEO called me into his office the next day to personally thank me for outsmarting the hackers.
I didn't tell him the firewall was unpatched because I forgot the admin password 6 years ago.
I haven't logged into the security console since the Obama administration.
I billed the company $400 for a catered lunch with Connor.
I spent the afternoon watching a documentary about deep-sea fishing while the company felt safer than ever.
True security is just aggressive confidence in the face of absolute negligence.
neofito retweeted

Releasing the model weights and technical report of Kimi K3.
Kimi K3 is our most capable model: a 2.8T MoE model with native visual understanding and a 1M-token context window.
New model architecture: 2.5x the intelligence per unit of compute, not just more params.
Alongside Kimi K3, we're opening up more of the stack behind it — high-performance attention kernels, MoE communication library, and infrastructure for running agent environments at scale.
Model weights: huggingface.co/moonshotai/Ki…
Tech report: github.com/MoonshotAI/Kimi-K…
Tech blog: kimi.com/blog/kimi-k3

neofito retweeted
Dominio t.me de Telegram suspendido; enlaces caídos en todo el mundo
El dominio principal de Telegram, t.me, ha sido colocado en estado serverHold por el registro .me. Esta acción a nivel de registro elimina el dominio del DNS global, lo que provoca que todos los enlaces cortos de t.me dejen de funcionar en todo el mundo. Los registros WHOIS confirman que el dominio presenta ahora ocho banderas de estado, incluyendo restricciones de eliminación
blog.elhacker.net/2026/07/do…
