

Learn Deeply. Share Freely. My research and insights are free for everyone. You can become a supporting subscriber. https://teapawt.net/t.co/8SEhDctEiR
Joined December 2009
- Tweets3.1K
- Following1.3K
- Followers1.7K
- Likes2K




Pinned Tweet
blog.naver.com/4-fire/224166…
한국어로 보다 자세한 내용은 👆


$IONQ
Why did IonQ suddenly start talking about PQC?
🇺🇸netcreat.substack.com/p/why-…
🇰🇷 blog.naver.com/4-fire/224296…
What if IonQ’s real ambition isn’t to develop another encryption algorithm, but to control the security layer above it?
QKD, PQC, key management, Zero Trust, and trust orchestration may be pieces of a much bigger strategy.
I connected the dots in my latest deep dive.

Will Quantum Computers Break All Encryption? — A Beginner’s Guide
netcreat.substack.com/p/will…
There are three essential points.
Encrypt the data strongly.
Share and manage its secret keys securely.
Control access so that even when a system is compromised, the damage cannot spread.

양자컴퓨터가 발전하면 모든 암호가 깨질까요? — 입문편
blog.naver.com/4-fire/224462…

$IONQ
Is QSPM's Real Competitive Advantage in Deployment Architecture Rather Than Detection Sensors?
Full report here.
🇺🇸netcreat.substack.com/p/is-q…
🇰🇷 blog.naver.com/4-fire/224461….
There’s a world of difference between having absolutely no blind spots and having even just a few.

PQC Detection: Could Existing Switches Be the Key?
Originally written and published in Korean on November 1, 2026.
Original Korean version: blog.naver.com/4-fire/224461…
✅ The Potential of Elisity
To prepare for the era of quantum computing, we must first find out which devices are using vulnerable cryptography. It is much like walking through an entire hospital to identify rooms still secured with old, outdated locks.
Surveying how cryptography is used and managing the order in which it should be replaced is the role of QSPM. However, discovering vulnerable cryptography and actually replacing it are two different tasks.
✅ 1. Why Does the Conventional Approach Leave Blind Spots?
A CCTV camera at the front entrance can show who enters or leaves, but it cannot see every hallway inside the building. Likewise, a network firewall can analyze only traffic that passes through the paths it monitors.
Zscaler primarily analyzes internet and SaaS traffic passing through its ZIA service, while Palo Alto analyzes traffic traversing its firewalls and other relevant products. Internal communications that never pass through those paths may go unseen.
Forescout uses SPAN or TAP to copy switch traffic for analysis by sensors. This can also provide visibility into internal networks, but expanding the number of monitoring points may increase sensor and analytics resource requirements as well as operational overhead. That is why monitoring only one point on the WAN is not enough.
✅ 2. Elisity’s Use of Existing Switches Could Offer a Solution
Elisity already uses an enterprise’s existing switches as policy enforcement points called VENs. The VE (Virtual Edge), which manages them, can run as an App Hosting container on certain Cisco Catalyst switches.
What if a lightweight PQC analysis program could be added to this setup? One could envision a process in which a switch mirrors traffic → an on-switch container examines TLS/SSH cryptographic methods → risk information is sent to IdentityGraph. It would be like setting up a small inspection room inside an existing building.
Where on-switch analysis is not possible, mirrored packets could be sent over ERSPAN to an analysis VM running on an existing server. Combining firewall logs, active scanning, and management APIs could also help fill some of the gaps that packet inspection alone cannot cover.
Of course, there is no evidence that Elisity currently offers this PQC analysis capability as a commercial product. Cisco’s IOx-based, switch-hosted sensors provide a useful real-world precedent, not proof that Elisity has completed such a product.
✅ 3. Why Would This Matter If It Were Actually Implemented?
Rather than installing new physical sensors throughout the network, this approach could reuse existing switches, containers, and VMs as much as possible, while examining a wider range of internal communications that existing security products may miss.
If Elisity’s IdentityGraph could associate discovered cryptographic risks with actual devices and, when necessary, use policy enforcement capabilities on existing switches, deployment and day-to-day management might also become simpler.
However, not every blind spot would disappear. Switch CPU, memory, and traffic-mirroring capacity; supported hardware models; communications contained entirely within VMs; and HSMs and other areas invisible to packet inspection would remain challenges to solve.
Ultimately, the real competitive advantage may depend less on simply having a “detection feature” and more on how much actual visibility and operational efficiency can be improved while minimizing additional hardware. We will examine the technical details and validation criteria in the next article.
📌 References
See Elisity’s Hardware Compatibility Matrix, the explanation of VE and VEN, and Cisco’s documentation related to switch-hosted sensors.
The integrated PQC detection architecture for Elisity discussed here is a hypothesis about technical feasibility.
netcreat.substack.com/p/elis…

PQC Detection: Could Existing Switches Be the Key?
Originally written and published in Korean on November 1, 2026.
Original Korean version: blog.naver.com/4-fire/224461…
✅ The Potential of Elisity
To prepare for the era of quantum computing, we must first find out which devices are using vulnerable cryptography. It is much like walking through an entire hospital to identify rooms still secured with old, outdated locks.
Surveying how cryptography is used and managing the order in which it should be replaced is the role of QSPM. However, discovering vulnerable cryptography and actually replacing it are two different tasks.
✅ 1. Why Does the Conventional Approach Leave Blind Spots?
A CCTV camera at the front entrance can show who enters or leaves, but it cannot see every hallway inside the building. Likewise, a network firewall can analyze only traffic that passes through the paths it monitors.
Zscaler primarily analyzes internet and SaaS traffic passing through its ZIA service, while Palo Alto analyzes traffic traversing its firewalls and other relevant products. Internal communications that never pass through those paths may go unseen.
Forescout uses SPAN or TAP to copy switch traffic for analysis by sensors. This can also provide visibility into internal networks, but expanding the number of monitoring points may increase sensor and analytics resource requirements as well as operational overhead. That is why monitoring only one point on the WAN is not enough.
✅ 2. Elisity’s Use of Existing Switches Could Offer a Solution
Elisity already uses an enterprise’s existing switches as policy enforcement points called VENs. The VE (Virtual Edge), which manages them, can run as an App Hosting container on certain Cisco Catalyst switches.
What if a lightweight PQC analysis program could be added to this setup? One could envision a process in which a switch mirrors traffic → an on-switch container examines TLS/SSH cryptographic methods → risk information is sent to IdentityGraph. It would be like setting up a small inspection room inside an existing building.
Where on-switch analysis is not possible, mirrored packets could be sent over ERSPAN to an analysis VM running on an existing server. Combining firewall logs, active scanning, and management APIs could also help fill some of the gaps that packet inspection alone cannot cover.
Of course, there is no evidence that Elisity currently offers this PQC analysis capability as a commercial product. Cisco’s IOx-based, switch-hosted sensors provide a useful real-world precedent, not proof that Elisity has completed such a product.
✅ 3. Why Would This Matter If It Were Actually Implemented?
Rather than installing new physical sensors throughout the network, this approach could reuse existing switches, containers, and VMs as much as possible, while examining a wider range of internal communications that existing security products may miss.
If Elisity’s IdentityGraph could associate discovered cryptographic risks with actual devices and, when necessary, use policy enforcement capabilities on existing switches, deployment and day-to-day management might also become simpler.
However, not every blind spot would disappear. Switch CPU, memory, and traffic-mirroring capacity; supported hardware models; communications contained entirely within VMs; and HSMs and other areas invisible to packet inspection would remain challenges to solve.
Ultimately, the real competitive advantage may depend less on simply having a “detection feature” and more on how much actual visibility and operational efficiency can be improved while minimizing additional hardware. We will examine the technical details and validation criteria in the next article.
📌 References
See Elisity’s Hardware Compatibility Matrix, the explanation of VE and VEN, and Cisco’s documentation related to switch-hosted sensors.
The integrated PQC detection architecture for Elisity discussed here is a hypothesis about technical feasibility.
netcreat.substack.com/p/elis…

쉬운 버전입니다.
blog.naver.com/4-fire/224461…
이전 분석글에서도 언급했듯이 Micro-segmenation을 지원하면서 PQC 탐지기능 (QSPM과 유사)을 동시에 지원하는 업체는 아래 3업체입니다.
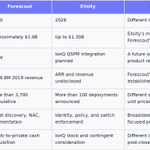
Forescout : $1.6B 2020년 인수가격
Paloalto $PANW : $299.6B (시총)
Zscaler $ZS : $38.8B (시총)
어느 하나 $IONQ 가 인수할 수 있는 저렴한 업체가 없습니다. 그리고, 이들이 지원하는 PQC 탐지 기능은 각각 제약이 있습니다.
제가 아는 IONQ는 Scalability, Efficiency 등의 GTM에 직접적으로 기여할 수 있는 잠재력이 있지만, 아직 미완성인 기업을 선호합니다.
다음엔 PQC 탐지 기능이 어떻게 구현되며, 각 업체별 장단점이 무엇인지 살펴보겠습니다.


이전 분석글에서도 언급했듯이 Micro-segmenation을 지원하면서 PQC 탐지기능 (QSPM과 유사)을 동시에 지원하는 업체는 아래 3업체입니다.
Forescout : $1.6B 2020년 인수가격
Paloalto $PANW : $299.6B (시총)
Zscaler $ZS : $38.8B (시총)
어느 하나 $IONQ 가 인수할 수 있는 저렴한 업체가 없습니다. 그리고, 이들이 지원하는 PQC 탐지 기능은 각각 제약이 있습니다.
제가 아는 IONQ는 Scalability, Efficiency 등의 GTM에 직접적으로 기여할 수 있는 잠재력이 있지만, 아직 미완성인 기업을 선호합니다.
다음엔 PQC 탐지 기능이 어떻게 구현되며, 각 업체별 장단점이 무엇인지 살펴보겠습니다.
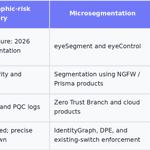
I couldn't justify $IONQ's $1.3B Elisity deal—until I revisited a 2020 cybersecurity buyout.
That company had no PQC discovery back then.
I compared seven vendors across six microsegmentation dimensions. The real question may be bigger:
🇺🇸 netcreat.substack.com/p/is-i…
🇰🇷 blog.naver.com/4-fire/224460…
What is IonQ actually buying?

I couldn't justify $IONQ's $1.3B Elisity deal—until I revisited a 2020 cybersecurity buyout.
That company had no PQC discovery back then.
I compared seven vendors across six microsegmentation dimensions. The real question may be bigger:
🇺🇸 netcreat.substack.com/p/is-i…
🇰🇷 blog.naver.com/4-fire/224460…
What is IonQ actually buying?
NIST’s PQC deadlines are approaching.
If Elisity delivers the QSPM $IONQ envisions—combining cryptographic discovery, risk mapping, and microsegmentation—does the $1.15B acquisition look different?
I’m comparing the technology, competitors, and valuations.
Report coming soon.

NIST’s PQC deadlines are approaching.
If Elisity delivers the QSPM $IONQ envisions—combining cryptographic discovery, risk mapping, and microsegmentation—does the $1.15B acquisition look different?
I’m comparing the technology, competitors, and valuations.
Report coming soon.
NIST가 PQC 전환 지침 최종 확정
blog.naver.com/4-fire/224457…
12월 31일2030
중요 연방 시스템의 PQC 키 설정 전환
12월 31일2031
중요 연방 시스템의 PQC 디지털 서명 전환
이후2035
양자 취약 공개키 암호 알고리즘 사용 금지
nist.gov/news-events/news/20…
$IONQ didn't just buy a foundry.
SkyWater's SP90 is building a quantum photonics stack: SiN routing, diamond memories, TFLN conversion, and cryogenic packaging.
But 493nm propagation loss is still 1.56 dB/cm.
What's real today—and what remains unproven?
🇺🇸netcreat.substack.com/p/ionq…
🇰🇷blog.naver.com/4-fire/224459…


$IONQ ’s $1.3B Elisity deal: Is the technology really unique?
Elisity vs. 6 rivals across 7 layers—from identity and AI policies to enforcement and PQC readiness.
The real value may lie beyond the technology. 👇
Seven Core Microsegmentation Technologies: A Comprehensive Comparison of Elisity and Its Competitors
🇺🇸netcreat.substack.com/p/seve…
🇰🇷blog.naver.com/4-fire/224458…

The UK’s Quantum Leap and Its Space Quantum Roadmap
🇺🇸 netcreat.substack.com/p/the-…
The UK did not announce another £2B quantum budget in October.
Its new space roadmap expands the scope of Quantum Leap, while ProQure Phase 1 awards remain worth watching.
I examine the funding, satellite QKD, and potential links to IonQ.
@Rick101284 이 공유해준 소중한 내용을 분석해봤습니다.
지난 4월에 발표된 Quantum Leap 대비 어떤 변화가 있는지 비교했고, $IONQ 의 기술과 어떻게 연결이 되는지 살펴봤습니다.
blog.naver.com/4-fire/224457…
이번 발표에서 특히 눈에 띄는 것이 Hybrid Optical Payloads 였는데, AFRL에서 후속 자금을 확보하면서 발표된 것과 일치하는 것으로 보입니다.
