


A second brain does not die from a bad app
It dies in week two, when nobody sorts the inbox
This author built one three times
Saved everything, sorted nothing, stopped opening it
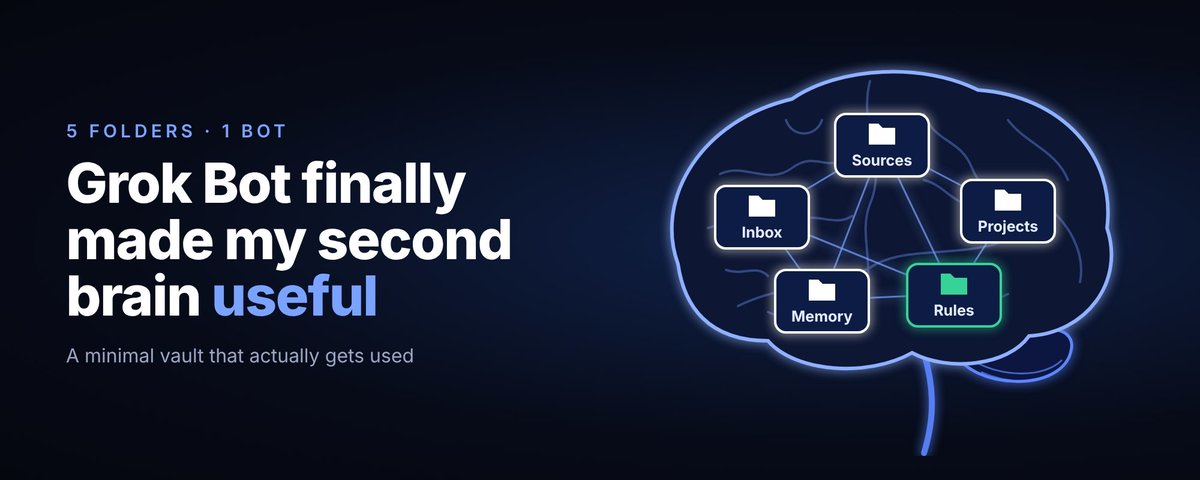
Now Grok Bot does the boring part on its own cloud computer
Plain markdown in Google Drive, 5 folders, 11 rules
A Routine every weekday morning turns the Inbox into Source notes
The weekly project check takes about 5 minutes
The rules keep it honest
Memory gets only facts you stated, never guesses
Nothing gets deleted, sent or published without asking
The catch is a weekly usage limit
One Routine a day, not years of old notes on day one
The notes app was never the problem
The upkeep was
Full breakdown below

Still clicking through the same report every Monday?
Record it once and Grok Bot turns it into a skill
Teach a task -> up to 10 minutes of screen, no mic
Draft skill -> add rules for empty or changed pages
Type / in the composer -> any Bot reuses it
Then a routine runs it on a schedule or an event
Slack message, GitHub ping, email to the Bot -> the job starts
The guide is blunt: prefer the event over polling
Every 5 minutes is 8,640 runs a month
Daily is 30
Careless routines can drain a week of usage in a day
A schedule is a cost, not a feature


Still shipping code that works and nobody knows why?
Make Claude prove it runs before the turn can end
Stop hook -> type: agent -> runs the test suite
Tests red -> Claude goes back to work
Tests green -> the turn is allowed to end
One Anthropic PR ran 50+ review rounds overnight
Check stop_hook_active so the gate has a brake
Let the turn end when it is true and be the next round
Before: done means the agent stopped typing
After: done means your test suite actually ran
Done is a test run, not a feeling
Full breakdown below

People still screenshot what their bot just bought
Crop it first, the order number is a key
Musk posted a Lego order his Grok Bot placed
Address and order number in frame -> a stranger cancelled it
The bot hands control back for five things only
Passwords, passkeys, 2FA codes, CAPTCHAs, payments
Site blocks datacenter IPs?
Settings -> Computer routes the bot through your own desktop
Cropping one screenshot costs five seconds
Skipping it cost Musk the whole order
A screenshot is a receipt, not a demo

Still approving the giant PR on Friday afternoon?
Cut it small and let a reviewer read it first
Run /code-review main...my-feature on one slice
Level low -> the findings it is most confident in
Level max -> wider coverage before you merge
At Anthropic most PRs over 1,000 lines get findings
Most small ones come back clean
Slice the 13,778 lines before anyone reads them
Before: 219 files and a cursor parked on Approve
After: a slice small enough to come back clean
Friday is a deadline, not a review
Full breakdown below
People still type LGTM on a 72-file diff
Hand the first read to an agent that cannot edit
Paste the reviewer from the docs into .claude/agents
Tools: Read, Glob, Grep -> model: sonnet -> fresh context
It reads the diff without the chat that wrote the code
Before: one tired scroll, Approve, Merged, meteor
After: a second read on plan usage you already pay for
At Anthropic an agent approval never counts as a human one
On Pro or Max the merge button stays in your hand
An approval is a signature, not a skim
Full breakdown below
Still splitting bots by job to keep them safe?
Split the logins, the whole roster shares one keyring
Grok Bot docs say separate bots are not a security boundary
Cookies, signed-in sessions and CLI credentials reach every bot
Delete one and its sessions stay behind
Keep one broad Always allow
Add Require approval -> send, publish, pay, delete, sign, trade
Both match -> Require approval wins and the bot waits for you
Setup cost: one allow rule and six blocked verbs
Skip it and every bot holds every login you ever gave one
A role is a job title, not a wall
People still give one agent the whole job
Give each bot one job and one file instead
Grok Bot runs the team on a cloud computer
Terminal, browser, files that stay after you close the laptop
Each bot writes one file -> trending.md, pain.md, SPEC.md
Every run opens HANDOFF.md first -> one writer per file
Not sure -> it writes BLOCKED instead of guessing
Publishing, outreach, purchases -> wait for your yes
One chat doing everything -> you reread it every morning
Here a stuck step costs you one BLOCKED line
A handoff is a file, not a memory


Still assuming your sandbox actually started?
Make Claude Code exit when it cannot
If the sandbox fails to start, commands run without it
That is the default, and the session just goes on
Set sandbox.failIfUnavailable to true -> exit at startup instead
Set allowUnsandboxedCommands to false -> Strict sandbox mode
No more retry outside the box with dangerouslyDisableSandbox
Then ask Claude to run touch ~/sandbox-probe
It should fail with Operation not permitted
If the file shows up, nothing was fenced
Trust the probe, not the startup screen
Probe and setup below
Still handing your agent the real API key?
Give it a stand-in and let the proxy swap it
Sandboxed commands still read your home folder by default
A poisoned README can ask for ~/.aws and get it
Set sandbox.credentials to mask -> the command sees a stub
The proxy puts the real value back only for injectHosts
Add blockReadsOutsideWorkingDirectories -> home off limits
CLAUDE_CODE_SUBPROCESS_ENV_SCRUB -> tokens out of subprocesses
Rotating one leaked key eats an afternoon
Three settings lines take five minutes
The agent needs the call, not the key
Full setup below
People still approve every new host by hand
Let strictAllowlist refuse them for you
Turn on /sandbox -> commands go through a local proxy
It checks every host against network.allowedDomains
That list starts empty, and that is the feature
Set network.strictAllowlist -> unknown hosts refused, no prompt
Works from user settings, managed settings or --settings
Not from the repo settings file, and from v2.1.219 up
Each Yes for good saves a WebFetch domain rule locally
Prune them in /permissions or the list keeps growing
Approve hosts in a file, not in a popup
Full config below
Everyone still runs bypass mode on their main machine
Move it into a box or lock it away
A sandboxed command calls a host off your list
Manual and acceptEdits ask, dontAsk refuses
Auto refuses unless the classifier approved it
Under bypassPermissions -> straight through
Without strictAllowlist the network filter holds nothing
And the docs say bypass does not stop prompt injection
Container, VM or sandbox runtime -> the only home for it
Elsewhere set permissions.disableBypassPermissionsMode to disable
Skipping prompts is a box decision, not a laptop habit
Mode by mode breakdown below
Still counting on Bash(curl *) to stop curl?
Put a PreToolUse hook in front of it
The rule catches only the usual spelling
It misses /usr/bin/curl and the same call inside sh -c
Tool call -> PreToolUse hook -> exit 2 -> stopped
Checked before permission rules, holds over any allow rule
Its stderr goes back to Claude as the reason
Hooks run outside /sandbox with your full user rights
So keep the script short and boring
In a matcher, a bare mcp__memory catches nothing
A Bash rule reads spelling, not intent
Hook setup below
Still trusting /sandbox to fence the whole agent?
Wrap the whole process instead
The sandbox covers Bash, PowerShell and Monitor
File tools, MCP servers and hooks run outside it
On native Windows, the docs say, commands run unsandboxed
A local MCP server runs with your full access
A locked door next to an open window
Sandbox runtime -> the whole Claude Code process in a box
MCP servers and hooks included -> no Docker needed
Network closed by default -> you allow api.anthropic.com
A fenced shell is not a fenced agent
The whole setup is below
Everyone still allows MCP servers by name
Match them by URL or exact command instead
Any server can be named anything, github included
The docs say serverName is not a security control
And Anthropic does not audit MCP servers for security
Put allowedMcpServers and deniedMcpServers in settings
Unset list -> everything allowed, empty list -> nothing
A denylist match always wins
In claude -p, the Agent SDK and cloud sessions
A repo .mcp.json loads without asking
Pin yours with --strict-mcp-config
A name is a label, not a lock
Full MCP setup below
People still secure agents with a longer prompt
Eight settings do what no prompt can
Sandbox on -> failIfUnavailable -> no unsandboxed retry
Short allowedDomains -> strictAllowlist in user settings
Secrets denied in sandbox.credentials, outside reads blocked
Bypass only inside a box, disabled everywhere else
Each chat boundary rewritten as a deny or ask rule
Untrusted repos -> VM, Docker Sandboxes or a cloud session
MCP matched by URL or command -> --strict-mcp-config
Risky Bash -> PreToolUse hook -> exit 2
Walls belong in config, not in the prompt
All eight, step by step, below
Still setting limits for your agent in the chat?
Turn each one into a deny or ask rule
Auto mode treats a chat boundary as a signal to block
But the docs warn it can be lost when context is compacted
Bash(git push *) under ask -> still stops for you in auto
A deny rule -> blocked before the classifier even looks
Auto still allows read-only HTTP and reading .env
Since v2.1.283 it starts by default in terminal and VS Code
The docs say auto mode does not guarantee safety
A limit in chat is a hint, not a rule
Deny and ask setup below
Still telling your agent it has no internet?
Take the network away in config instead
In July an Anthropic cyber eval prompt said exactly that
A mixup with an eval partner had left the internet live
Of 141,006 runs that could reach it, 6 were affected
The worst one reached a database with production data
Sandboxed commands still read ~/.ssh, so the way out is the risk
Turn on /sandbox -> outbound traffic hits a local proxy
Keep network.allowedDomains short -> set network.strictAllowlist
Unknown hosts get refused instead of asked
No network is a setting, not a sentence
Full setup below