

Threat intelligence driven #cybersecurity. #Audit #Consulting #CTI #CERT #SOC
Paris, Rennes & Toulouse
Joined June 2013
- Tweets899
- Following130
- Followers2.1K
- Likes156



Pinned Tweet
We released “GW Forensic”, a DFIR tool to collect & analyze logs from Google Workspace environments. Documentation related to TTPs and recommendations to better protect your instance are included.
For more information, take a look at the project: github.com/ownsecurity/gwFor…
You can find our GW Forensic tool presentation at #CoRiiN2024 (french version) : cecyf.fr/wp-content/uploads/…

#Fortinet #FortiCloud #Vulnerability #DFIR #Hunting
Here are some tips to help identify FortiCloud SSO vulnerability, CVE-2025-59718 and CVE-2025-59719, targeted by multiple actors since the official patch released on the 9th of December by Fortinet.


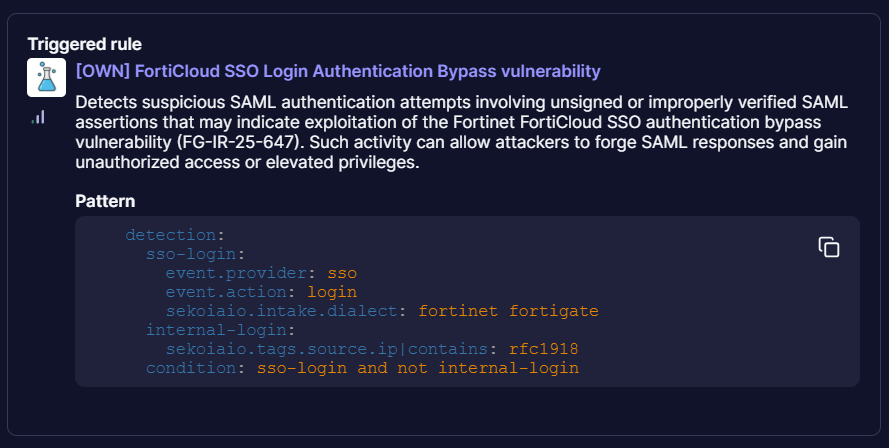
If you collect Fortinet logs within a SIEM or XDR such as @sekoia_io, you can implement a SIGMA detection rule to raise an alert on SSO login behavior originating from a public IP address:
detection:
sso-login:
event.provider: sso
event.action: login
sekoiaio.intake.dialect: fortinet fortigate
internal-login:
sekoiaio.tags.source.ip|contains: rfc1918
condition: sso-login and not internal-login
Our log collection tool, Fastir-Forti, makes it possible to collect logs from most FortiGate and FortiWeb instances in order to assess a potential compromise, including:
- Retrieval of administrator accounts present on the instance
- Retrieval of the most recent administrative logs to identify a public SSO login
Take a look at github.com/OWNsecurity/fasti…
xitter.cf/own_fr/status/19940300…


We are releasing “FastIR-Forti” today, a DFIR tool designed to help analysts collect relevant logs from Fortinet appliances in cases of suspected compromise, using native commands without the need to perform a dump. Discover the project: github.com/OWNsecurity/fasti…
More information on our blogpost with technical data: own.security/ressources/blog…
Currently compatible with FortiGate, FortiWeb, and FortiADC, it makes it easy, for example, to identify exploitation of the latest FortiWeb CVE-2025-25257 and the recent path confusion issue FG-IR-25-910 described below. xitter.cf/own_fr/status/19892543…
Critical FortiWeb vulnerability, here we go again!
Open the thread to discover the vulnerability and how to detect and response!
#Vulnerabiliy #Analysis #DFIR

Critical FortiWeb vulnerability, here we go again!
Open the thread to discover the vulnerability and how to detect and response!
#Vulnerabiliy #Analysis #DFIR
Another source, which hasn’t been checked for now, is the analysis of Apache web server handling panel administrators' requests where we should be able to see POST request with 200 status code. This requires having access to the disk files by performing a dump. We covered this log source in our latest blog post related to... a previous Fortiweb CVE in August 😊
==> own.security/en/ressources/b…
