

Takedown tools for small security teams Tweets about phishing kit analysis, takedown tips, and new tools https://xitter.cf/t.co/44hDmZ9xnj
Report phishing →
Joined May 2021
- Tweets1.4K
- Following138
- Followers1K
- Likes289




Pinned Tweet
We're excited to release IOK, our open source signature format for phishing sites! 🎣
You can write IOK rules to:
🗂 Track specific phishing kits
🪝 Identify obfuscation and evasion tactics
👤 Attribute threat actors
All 100% open source 💙
phish.report/IOK

🎁 Every day this advent, we're releasing a small phishing detection challenge where you can learn:
🎣 Good techniques for finding phishing sites
📝 How to write IOK rules (our open source rule language)
Here's today's introductory challenge: phish.report/IOK/learn/010-h…
We've seen a huge increase in the use of LiteSpeed's "Bot Verification" page over the past few months 📈
Using reCAPTCHA isn't a new tactic, but using LiteSpeed makes detection significantly harder


Every week we're sharing one interesting phishing kit/technique/tactic on the Phish Report community forum
Follow along here: community.phish.report/t/the…
Previously we could use the quirks of each reCAPTCHA implementation to distinguish between threat actors, but here thousands of sites are using an identical implementation
(though still possible to gain some intelligence through the re-use of reCAPTCHA API keys)
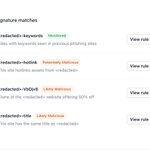
Alerts that don't explain themselves are bad alerts 👎
That's why our new analysis page shows you exactly why we think a website is malicious 💡

ALT Website section titled "Signature matches" with 4 rows describing different detection rules (and associated confidence levels) that a website has matched
❗️ Phish Report has identified a new organised phishing group (codename RedLungfish) who are targeting dozens of financial institutions
They employ multiple human operators who interact in real time to trick victims into handing over their credentials
phish.report/blog/red-lungfi…

During our investigation we:
1️⃣ Identified reliable indicators of when a phishing site is being operated by RedLungfish
2️⃣ Emulated the admin panel to discover its capabilities
3️⃣ Pivoted to identify threat actor infrastructure spanning the last six months
phish.report/blog/red-lungfi…
Phish Report retweeted
Nothing more satisfying than seeing a wall of flags, all of these are scanning locations available through Live Scanning on our urlscan Pro platform 😊 More to come in Q4!

Combatting brand impersonation is more than just reporting abuse to hosting providers. Here's the top 4 vulnerabilities we find in phishing kits that you can use to disrupt an attack 👇
4️⃣ CWE-425: Direct Request ('Forced Browsing')
Some more advanced phishing kits have admin panels that the phisher can use to monitor the status of their site. While these are usually password protected the implementation is poor and parts can be loaded without authentication.
See the full blogpost for more details: phish.report/blog/top-phishi…
How does VirusTotal's new Netloc YARA extension compare with IOK for detection malicious websites?
Netloc: extensive attributes you can match on, but proprietary and enterprise-only
IOK: more limited attributes available, open-source and self-hostable
phish.report/docs/netloc-vs-…

Most phishing sites aren't created from scratch, they're made by cloning a real webpage. Here's three ways to harden a page against cloning:
1️⃣ Install beacon assets: if done properly these evade the cloning process and will call back to your server with the clone's URL

3️⃣ Don't be generic: if your log-in page is simply titled "Log in" you'll have a hard time distinguishing a clone from all the other login pages out there. Include your brand name to make clones stand out (even if they've changed almost everything else on the page)
Read the rest of our guide here on hardening your login page against cloning: phish.report/blog/harden-aga…

There's many ways to submit suspicious URLs to Phish Report that aren't our homepage 👇
1️⃣ Put "phish.report/" in front of any URL and you'll be taken straight to our analysis of it