




Radman retweeted

You're back in the room, trapped with us - and a Citrix NetScaler Pre-Auth RCE (CVE-2026-8452)
Enjoy...
labs.watchtowr.com/youre-bac…

Radman retweeted
What do we even say at this point?
CVE-2026-8451, a zero-day Memory Overread that watchTowr Labs identified in Citrix NetScaler appliances in March, has just been publicly disclosed with patches.
We're not done yet... speak soon... ;-)
labs.watchtowr.com/citrixble…

New subdomain went live
Yii2 debug mode enabled → Full database credentials leaked in stack trace
Just 3 hours later → Access Forbidden
Continuous monitoring isn’t optional
Note: This subdomain was only discoverable via DNS brute-force
8
496
Radman retweeted

Hacking Google with A.I. for $500,000
brutecat.com/r/hacking-googl…

Radman retweeted

It's time for sharing, this is not a simple write-up, we are sharing our methodology and reasoning, detailing how we approached and hunted the flaw, I hope you like it :]
blog.voorivex.team/uxss-on-s…


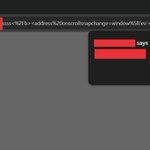
I just found a WAF bypass for Akamai and Cloudflare:
<address onscrollsnapchange=window['ev'+'a'+(['l','b','c'][0])](window['a'+'to'+(['b','c','d'][0])]('YWxlcnQob3JpZ2luKQ==')); style=overflow-y:hidden;scroll-snap-type:x><div style=scroll-snap-align:center>1337</div></address>


rXSS via url parameter
1. I discovered reflection in a URL parameter
2. All inputs I submitted were being HTML encoded
3. I submitted the following input: https://sss'"<>, and in the response, my payload was displayed without proper sanitization.
#xss #BugBounty #infosec


سال جدید رو به همه تبریک میگم امیدوارم سال خیلی خوبی برای همه باشه.
برای بچه های باگ هانتر هم سال پر از باگی باشه.
42
2,039
در جلسهای که با اعضای وزارت داشتم، آسیبپذیری بههمراه اکسپلویت آن گزارش شد. قرار است این آسیبپذیری بهزودی برطرف شود.
به امید اینترنتی امنتر.

یه باگی روی یکی از وزارتخونهها زدم که میتونم به تمام اطلاعات کاربرهاشون دسترسی پیدا کنم و چند بار هم بهشون ایمیل زدم ولی جواب ندادن. الان یک ساله که این باگ وجود داره
نمیدونم چی بگم پرام ریخته از این مملکت

7
109
7,872


Radman retweeted

New blog post with @infosec_au:
We found a vulnerability in Subaru where an attacker, with just a license plate, could retrieve the full location history, unlock, and start vehicles remotely.
The issue was reported and patched.
Full post here: samcurry.net/hacking-subaru

To initiate mediation on HackerOne, you need to submit a mediation request first.
@Hacker0x01

1
33
3,286
Radman retweeted

سلام با کلی بالا و پایین و پارگی تصمیم گرفتیم یه کنفرانس امنیتی/هانتری برگزار کنیم، امیدواریم که حرکت مثبتی باشه. تاریخ ۲۴ و ۲۵ آبان برگزار میشه، برای ارسال مقالات تا ۴ آبان وقت هست. یه سری موارد هم نمیگیم که سورپرایزطور باشه. کلیه جزئیات توی سایت:
vooricon.com

Radman retweeted
New writeup from @_specters_ and I: we're finally allowed to disclose a vulnerability reported to Kia which would've allowed an attacker to remotely control almost all vehicles made after 2013 using only the license plate.
Full disclosure:
samcurry.net/hacking-kia