

Human-led pentesting that helps organizations prove security, not just compliance. Secure. Validate. Improve.
Joined March 2020
- Tweets290
- Following8
- Followers2.1K
- Likes120




Pinned Tweet
🚨Cloud Hacking Tools🚨
AWS - github.com/RhinoSecurityLabs…
GCP - github.com/RhinoSecurityLabs…
Azure - github.com/Azure/Stormspotte…
Multi Cloud - github.com/nccgroup/ScoutSui…
Multi Cloud - github.com/aquasecurity/clou…
#bugbountytips #bugbounty #redteam #Pentesting #PenTest #infosec #aws #gcp #Azure

“It’s just a regular user account.”
the regular user account:
- can edit everyone’s permissions
- owns the domain
- is actually an admin account


From Carnival Life to Protecting Companies From Hackers. Have you read our CEO's unique journey?
#inc5000

Today's Thought: @vblakeflores, co-founder and CEO of @redsentry_tech, shares how her unique childhood prepared her to be an entrepreneur. @sandy_carter @likethecoins @securitybrew @TrackerPayton @megan_roddie - What do you think?
inc.com/lucia-auerbach/red-s…


Does SOC 2 actually require a pentest?
Not exactly.
The better question: What technical testing do your controls actually need?
We break down how to scope testing around your environment, controls, and audit evidence without overbuying or leaving gaps.
🔗 hubs.li/Q04ydRJF0

“We need a pentest.” But for what?
HIPAA, FDA submissions & customer security reviews can require different evidence, even when the testing overlaps.
Our latest blog breaks down the differences and where pentesting fits.
🔗 hubs.li/Q04xVvdX0

Q4 is around the corner. Is your pentest done?
Finding security gaps before they become incidents starts with actually testing your defenses.
If your 2026 pentest is still on the list, now’s the time.
Let our hackers find the gaps before they do. 🔴
Talk to our team → hubs.ly/Q04x7RgV0

🏆 July CTF results are in!
Huge congrats to the Top 3 from our Capture the Flag challenge with AP2T Labs:
🥇 Travanauts
🥈 ThreatExploit
🥉 ISP1337Hackers
Thanks to everyone who competed and put their skills to the test. 🔥
🔗 Full list of top performers in the first reply.
#RedSentry #CTF

Got SOC 2 questions?
Join us tomorrow for a casual SOC 2 AMA with Red Sentry + Rippling.
No slides. Just real questions and real-world answers. Link to register is in the first comment.
#soc2 #cybersecurity #compliance

DEF CON starts soon.
Travel light.
Don't use the Wi-Fi.
Keep your devices close.
Spend less time on your phone and more time exploring.
The best part of DEF CON is the people you'll meet.
See you there!
@vblakeflores
#DEFCON #HackerSummerCamp
Hacker Summer Camp is officially here 🎉
We're kicking things off at BSides today and will be at Black Hat and DEF CON all week.
Drink the coffee. Meet new people. Learn a lot. Have fun.
If you see the Red Sentry team, come say hi! 👋
@vblakeflores
#BlackHat #DEFCON #BSidesLV
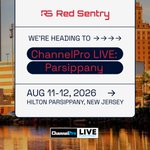
We're proud to sponsor #ChannelProLIVE Parsippany! 🎉
If you're attending Aug. 11–12, stop by and meet LaShawn & Megan to talk pentesting, offensive security, and how Red Sentry helps organizations stay ahead of threats.
See you there!
#Cybersecurity #MSP

Every breach is a chance to learn.
The latest DHS incident highlights why data classification matters. If your team can't distinguish between public, internal, confidential, and restricted data, it's time to start there.
#DHSbreach #Cybersecurity #DataSecurity