Brett retweeted
Thank you to everyone who made it out to our Defcon party this year, we all had a blast.
And thank you very much to everyone who helped make it happen. Looking forward to next year!
🤖 Made with AI
Brett retweeted
Next DC562 Meetup:
When: November 7
Where: A proper venue (weird huh)
What:
- Talks
- CS 1.6 LAN Party
- Head 2 Head CTF
- Pub Crawl
Hit up any DC562 member for details / invite!
Brett retweeted
DC562 party upgrade this year:
- 21+, full bar & kitchen, DJs + Dual Core & Crew
- PvP CTF w/ terminals
- Gaming consoles & plenty of stickers obv.
- Great conversations
- Hit up a member to get location
To help keep headcount in order please do not show up without an invite
Brett retweeted
Aaannnd we're back!
- Talks
- A.I. Challz
- Deathmatch CTF Demo
- Drinks
When: 3/8/25
Location: See GIF
Brett retweeted
This has been in the works for a while now and I am proud to finally release my research on some new DLL Hijacking techniques. #netsec #redteam blackhillsinfosec.com/a-diff…
Had some fun in procmon again exploring dll hijacking. Here are current working hijacks for common software you might come across. gitlab.com/rem1nd/dlljack/
Brett retweeted
Thrilled to release my latest research on Apache HTTP Server, revealing several architectural issues! blog.orange.tw/2024/08/confu…
Highlights include:
⚡ Escaping from DocumentRoot to System Root
⚡ Bypassing built-in ACL/Auth with just a '?'
⚡ Turning XSS into RCE with legacy code from 1996
Brett retweeted
Just because you get access denied accessing a folder, it doesn't mean you can't get access. A quick look at bypassing the security on the WindowsApps folder. tiraniddo.dev/2024/06/workin…
Even though I couldn't make it to LayerOne this year I still had a blast playing the CTF. Here are some super short solves for a few of the chals.
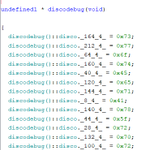
Disco Disaster(Reversing) chal was interesting. Another team member solved this one initially and I went back over it today to find the solution. I went through the discodebug function, sorted the positions, converted to ascii for the flag. An easier solve was available though
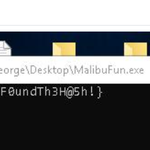
CyberSleuthAdventures(OSINT) offered a hash to be located. @Museifu_ found the hash on VT and from there we looked at the Zenbox full report which had multiple screenshots of the desktop with the program running. In the second screenshot we found the flag.
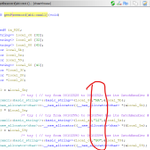
Dreamhouse(Reversing) was a straightforward chal that I solved by loading up the bin in Ghidra and reviewing the getPassword function. I threw the strings from that function at the binary to get the flag.
An update on me: still recovering from surgery after a nasty tibia plateau fracture. My leg no longer hurts but my ankle still feels compromised. My biggest concern is being ready to begin PT for my knee and not being able to stand on my leg due to my ankle. Hoping for the best


