

Threat Intel.
United States
Joined April 2019
- Tweets244
- Following38
- Followers736
- Likes408


Pinned Tweet
#strox runs an impressive #phishing op, #PHaaS, which removes barriers of entry into phishing.
#strox will rent you everything but the domain. e.g bulletproof host, phishing page, & market to sell the phished logins, etc
#cybersecurity #infosec #malware
lukeleal.com/research/posts/…


#Arkei #Stealer malware C2 panel using a login page that mimics the #WordPress login page but is actually connected to the C2 panel's database.
Used to evade detection so the panel can stay active on compromised websites for longer.
#malware #cybersecurity #C2

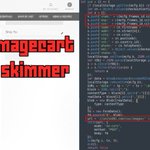
#JavaScript #skimmer overlayed onto payment page of an infected #Magento ecommerce store to steal payment card data from visitors
exfils to united81[.]com
#magecart #infosec #cybersecurity #malware
lukeleal.com/research/posts/…


It will be interesting to see how retailer's return policy changes will impact the existing #refunding service groups that charge users a fee for their #socialengineering skills that they use to obtain the #refund for the user.
cnn.com/2022/06/26/business/…
#cybercrime #cyberfraud


Luke Leal retweeted

[Tech blog] A cure for the obscure! PerimeterX researcher @ctrl__esc created a new open source #Javascript deobfuscator. Learn how it works. #infosec #supplychainattacks #magecart bit.ly/3v3hilm
Fake GTM tag loads #JavaScript #skimmer from jsdelivr[.]at on a hacked #magento store's checkout page to steal credit card data.
Skimmer URL: jsdelivr[.]at/js/jquery.ba.min.js
lukeleal.com/research/posts/…
#infosec #cybersecurity #malware


cdn-fonts[.]com used as the exfil for a #JavaScript #skimmer injected into the database on #hacked #Magento websites
URL: cdn-fonts[.]com/skin/loading.gif
lukeleal.com/research/posts/…
#infosec #cybersecurity #malware


staticounter[.]net injected into #magento db and loading #JavaScript on a hacked store's checkout page. Can't seem to identify a #skimmer in the loaded JS...
URL: js[.]staticounter[.]net/static/counter.js
lukeleal.com/research/posts/…
#infosec #cybersecurity #malware


#AnonymousFox 🦊 #FoxEx tool attempts LFIs on 80+ #WordPress plugin w known vulns.
If the wp-config.php gets read then it's a huge problem if the host allows remote #SQL connections (but also problem for local only).
#infosec #cybersecurity #cybercrime #webhosting


An overview of #AnonymousFox and their #PHP and #Python tools (e.g #FoxAuto) used for automating website exploits en masse & selling access to them on websites like #olux or #xleet.
#malware #infosec #cybersecurity #cybercrime #wordpress #webhosting
lukeleal.com/research/posts/…


An overview of #AnonymousFox and their #PHP and #Python tools (e.g #FoxAuto) used for automating website exploits en masse & selling access to them on websites like #olux or #xleet.
#malware #infosec #cybersecurity #cybercrime #wordpress #webhosting
lukeleal.com/research/posts/…
Don't use root login for #WordPress wp-config.php (or any website config)!
If someone is able to read the file (e.g vulns) then you've just made it much easier for them to get root access on the server.
#infosec #cybersecuritytips #iamroot #opsec #webhosting

Obfuscated #JavaScript found on legit bank login pages reveal a countermeasure that uses a tracking pixel to detect #phishing pages created from content scraping
images-cdn[.]info
content-cdn[.]com
lukeleal.com/research/posts/…
#infosec #cybersecurity #cybercrime


#JavaScript #skimmer found on infected #Prestashop websites and targeting Stripe payment data
exfiltrates stolen data to ccfresh[.]co (currently 0 detections on VT)
lukeleal.com/research/posts/…
#infosec #cybersecurity #malware


#javascript skimmer targeting #Magento websites and #psigate payment fields
exfil URL: dyneff[.]fr/health_check.php
lukeleal.com/research/posts/…
@Dyneff_ES #Dyneff
#magecart #infosec #cybersecurity #malware
big ups @liamsmith86 for sample


Large wave of recent #JavaScript #malware on #WordPress websites are grabbing their payload from trainresistor[.]cc which hides within img class tags instead of traditional <script> tags
lukeleal.com/research/posts/…
#infosec #cybersecurity #webdeveloper #webhosting


wtf() #skimmer continues to be used in-the-wild, targeting #WooCommerce #WordPress websites 💰 💳 ☠️
exfil: convert-server[.]com
#magecart #infosec #cybersecurity #malware #javascript

#S4LIM #phishing kit targets @n26 users w/ a multi-stage kit used for account takeover. Uses @PushoverApp API to send push notifications to attacker whenever a victim submits the first stage
@veehaitch @ActorExpose
#infosec #cybersecurity #cybercrime
lukeleal.com/research/posts/…


