


Russ retweeted

I've been researching the Microsoft cloud for almost 7 years now. A few months ago that research resulted in the most impactful vulnerability I will probably ever find: a token validation flaw allowing me to get Global Admin in any Entra ID tenant. Blog: dirkjanm.io/obtaining-global…
Russ retweeted

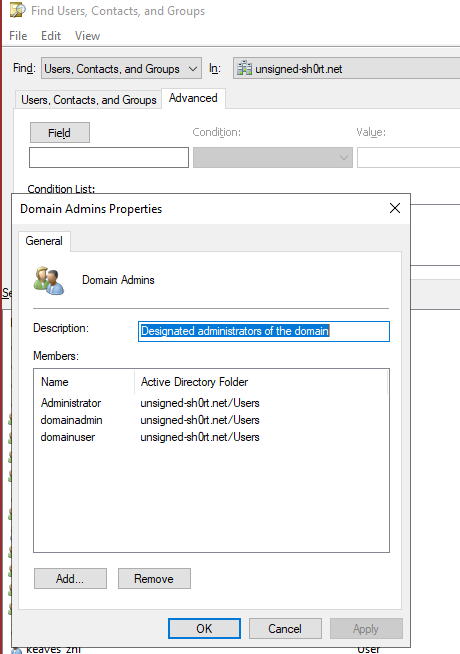
knew win10 had the dsquery.dll laying around but never knew what to do with it
"rundll32.exe dsquery.dll OpenQueryWindow" will pop open a console for you and you can do some light LDAP recon
you can also open with with win + ctrl + f
probably useful for VDI/Citrix type tests
Russ retweeted

What is OAuth Consent Phishing?
It’s a social engineering trick where the user grants access to a malicious app.
What is Token Replay?
It’s when you reuse stolen OAuth tokens to access cloud services without logging in again even after the user changes their password.

Russ retweeted

Introducing the BloodHound Query Library! 📚
@martinsohndk & @joeydreijer explore the new collection of Cypher queries designed to help BloodHound users to unlock the full potential of the BloodHound platform by creating an open query ecosystem. ghst.ly/4jTgRQQ
Russ retweeted

Short post on an alternative method for obtaining Microsoft Entra refresh tokens via Beacon. Proof of concept BOF is available on my GitHub 🙂 infosecnoodle.com/p/obtainin…

Russ retweeted

You all are misreading the MITRE CVE situation. MITRE ran out of numbers and was not prepared to move to CVEv6.


Russ retweeted
Make sure your cert requests include the SID of the user you're compromsing or setting persistence on. Strong mapping is enforced this month.
support.microsoft.com/en-us/…
Russ retweeted

Like seriously, if you still have Seamless SSO enabled, you probably aren't even using it and should really look at whether you can go turn it off
It's an unnecessary attack surface, especially in 2024
teapawt.net/NathanMcNulty/status/1…


Russ retweeted

Thank god cyber security awareness month is nearly over, I have a months' worth of links to click on, QR codes to scan and MFA prompts to approve here
Russ retweeted
This is an absolute bible on securing and detecting compromise of Active Directory, co-authored by the ASD and their partner agencies around the world. It is immensely thorough and covers attack techniques, logging recommendations and much more - cyber.gov.au/resources-busin…
Russ retweeted

💥 Exciting update and launch competition! 📢
Folks, I'm happy to announce another important milestone for @PwnedLabs - the launch of the 𝗠𝗶𝗰𝗿𝗼𝘀𝗼𝗳𝘁 𝗖𝗹𝗼𝘂𝗱 𝗔𝘁𝘁𝗮𝗰𝗸 𝗮𝗻𝗱 𝗗𝗲𝗳𝗲𝗻𝘀𝗲 𝗕𝗼𝗼𝘁𝗰𝗮𝗺𝗽 - and our first certification!
𝗧𝗼 𝘄𝗶𝗻 𝗮 𝘃𝗼𝘂𝗰𝗵𝗲𝗿, 𝗷𝘂𝘀𝘁 𝗹𝗶𝗸𝗲 𝗮𝗻𝗱 𝗿𝗲𝘁𝘄𝗲𝗲𝘁 𝘁𝗵𝗶𝘀 𝗽𝗼𝘀𝘁. 5 vouchers are available and will be drawn randomly.
This comprehensive 4-week bootcamp and its structured learning path provide students with foundational concepts, essential security tools and techniques, and instruction in attacking and defending Azure and Microsoft 365 environments.
Students who successfully complete the 4-week bootcamp and structured learning path can then attempt the exam lab to try and earn the 𝗠𝗶𝗰𝗿𝗼𝘀𝗼𝗳𝘁 𝗖𝗹𝗼𝘂𝗱 𝗥𝗲𝗱 𝗧𝗲𝗮𝗺 𝗣𝗿𝗼𝗳𝗲𝘀𝘀𝗶𝗼𝗻𝗮𝗹 (𝗠𝗖𝗥𝗧𝗣) certification.
This has been one of the main things that our community has been asking for.
What can you expect to learn? -> bootcamps.pwnedlabs.io/mcrtp…
Russ retweeted

Folks, Microsoft just released a Microsoft Recovery Tool.
See details at techcommunity.microsoft.com/…

ALT New Recovery Tool to help with CrowdStrike issue impacting Windows endpoints By Intune_Support_Team Intune Support Team undefined As a follow-up to the CrowdStrike Falcon agent issue impacting Windows clients and servers, we have released a USB tool to help IT Admins expedite the repair process. The signed Microsoft Recovery Tool can be found in the Microsoft Download Center: https://go.microsoft.com/fwlink/?linkid=2280386. The steps to use the tool are detailed below.
Russ retweeted

Next to token theft for bypassing MFA, this should be your next legitimate concern in the cloud.
- residential proxies can give attackers leverage to do unlimited amounts of password spraying.
- Blended attacks can be very difficult to detect because the attacker can reside in the same geolocation as the victim.
What can you do about it?
- require device compliance in CAP
- if on AD required hybrid Entra ID join
- FIDO2 all admins with RBAC roles.
- if using P2 implement identity protection in CAP
- emergency accounts with elevated privileges should be the only ones excluded from CAP
- lock down service accounts where they can only operate from trusted IPs in CAP.
- block unknown and unsupported devices
Identity protection has some cool features such as suspicious API abuse protection. Yes, attackers are abusing graph API for reconnaissance purposes. So if you have P2 use it.
Why do all this?
Attackers will conduct their early operations from the outside to gain a foothold on an internal environment. So if an attacker calls the helpdesk to reset an employee with privileged access, they still won’t get in since they lack a device requirement to satisfy conditional access. Phishing attacks will be in the same boat.
This will ultimately cause an attacker to pivot with a C2 implant which could be risky if an enterprise is doing all the above. 😎

New on our blog: Cloudflare's Bot Management team has released a new Machine Learning model for bot detection (v8), focusing on bots and abuse from residential proxies. cfl.re/4cetEKX


Russ retweeted
I've always recommend the free Microsoft 365 developer subscription as a great way to learn. Having it locked behind a 600 EUR to 3k EUR minimum cost is going to hurt Identity Security learning capabilities for everyone. Very sad to see it like this.
devblogs.microsoft.com/micro…

Russ retweeted

For anyone who needs a refresher (like me lol) on how to explain what kerberos delegations are, this is one of my favorite references from a Def Con class (2019?) by Elad Shamir (a GOAT). Enjoy!
media.defcon.org/DEF%20CON%2…
Russ retweeted

🛡️ Protect your users from Device Code Flow abuse
In my latest blog I discuss the newest protection capability in the Conditional Access arsenal: Authentication flows
cloudbrothers.info/en/protec…


