




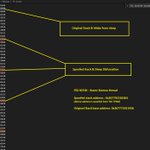
❗️Blog post alert
🌟Arm64/Arm64e internals
🌟Stack masking on Apple Silicon
@MDSecLabs
mdsec.co.uk/2026/08/arm64-st…

sabotage retweeted

I am very pleased to announce the official author team for the 7th edition of Gray Hat Hacking through @MHEducation. The book will be published in mid-2027.
Join me in welcoming: @chompie1337, @natashenka, @zodiacon, @ale_sp_brazil, @gf_256 to the team, along with 6th ed. authors @mosesrenegade & @htejeda!
A big thanks to @allenharper for carrying the book since the First Edition, as well as all authors across all editions.
Note: This is a mock up cover

sabotage retweeted
I've been fairly quiet about recent events for good reasons, but this popped up on my radar - netspi.com/mdsec-security-al…
I don't have much to say except some companies will forever lack class. For anyone looking for a new pentest, red team or c2 product vendor, there are many great ones out there and do your homework - the ones I am personally familiar with and would wholeheartedly recommend are @AmberWolfSec, @remotethreat, @SpecterOps, @OutflankNL and @TrustedSec ❤️
sabotage retweeted
Some unreal features coming in our next release - we finally made it to 1.0, well done @peterwintrsmith @s4ntiago_p @modexpblog @GigelV41464 @saab_sec 🙌🔥

sabotage retweeted

I decided to look into GDID after this, and reading the court document gave some hints. After poking at some stuff I can confidently say I figured out majority of the system end to end. Check it out at github.com/SmtimesIWndr/gdid…
p.s yes Claude helped don't come yell at me AI haters


> Peter Stokes
> Scattered Spider guy
> Arrested
> Microsoft helps FBI
> Read court documents
> Page 12
> Microsoft tracks Stokes from GDID
> Microsoft Global Device Identifier (GDID)
> Stokes used Windows
> Page 34
> GDID assigned to each OS install
> GDID unique to each device
> GDID only change if OS wiped
> Stokes GDID 6755467234350028
> GDID reported internet activity to Microsoft
> GDID showed Stokes using Ngrok
> GDID reported Stokes IP address
> GDID showed Stokes web activity
> GDID showed timestamps of web activity
> GDID mapped with video game activity
> GDID showed games played
> GDID undocumented
> GDID only mentioned in one MSDN document
> Azure UCDOStatus
> Azure Monitor Logging

sabotage retweeted
To confirm, we added cet masking support (the first to do so?) back in September '25 - xitter.cf/GigelV41464/status/202… - though this release adds 2 more new, completely different techniques

sabotage retweeted
I've been pretty quiet recently, mainly because we've been cooking up a few things at @MDSecLabs - some of which will be revealed over the next month or so. One of the most exciting things is a HUGE new @nighthawk_c2 release. It's packed with "stacks" of new OpSec - incl. 3 new CET compat masking. But most exciting of all, we have a super sexy new cross platform UI 🔥

sabotage retweeted

Fresh research from the team (@vkamluk / @juanandres_gs) - this one goes back quite awhile!
fast16 | Mystery ShadowBrokers Reference Reveals High-Precision Software Sabotage 5 Years Before Stuxnet
sentinelone.com/labs/fast16-…

sabotage retweeted

I decided to commit another part to the Applied Reverse Engineering series with an article diving into rolling your own primitive tracer for discrete purposes; coupled with an analysis on outrunning integrity checks.
revers.engineering/applied-r…

sabotage retweeted

Our latest post on the blog details a Windows EoP courtesy of @filip_dragovic... "Total Recall – Retracing Your Steps Back to NT AUTHORITY\SYSTEM" - mdsec.co.uk/2026/02/total-re…
sabotage retweeted
My thoughts are yes, red teaming has got significantly harder over the last few years. The knock on effect is:
1) engagements need more time,
2) teams who don't invest heavily in R&D (either in-house or outsourced) will be left behind,
3) there's less things shared publicly as a consequence,
4) lots of teams have tried to compensate by assuming breach, which as a result has led to less innovation in the IA space
However, I disagree that IA is anywhere near dead even targeting the top 1%. The vast majority of our engagements have a large IA component and we're still successful in >75% of cases. Yes the points mentioned are a pita - AWL is a great control, but there's equally a plethora of file formats that support scripting; get creative - Yes MOTW restricts some things - but there's a variety of ways around it if you're creative (and I'm not talking about ISOs 🙄)
You’re unable to view this Post because this account owner limits who can view their Posts. Learn more
sabotage retweeted

Don't do this. Don't make this mistake. Do something cooler. Listen to your peers when they recommend reviewing other peoples research.
malwaresourcecode.com/home/m…
sabotage retweeted
One of the new features we built for #Nighthawk customers is HawkEye. This is an AI bot built on Opus 4.5 that uses RAG to ingest all the #Nighthawk documentation, sample profiles, APIs, and sample source code. It's able to help explain features, build profiles, write source code for modules and much much more...

sabotage retweeted

Want to consume Microsoft-Windows-Threat-Intelligence but Antimalware-PPL getting you down? No problem! I will post a blog & POC soon - but this allows you to consume Threat-Intelligence without PPL _and_ w/o any kernel patching/driver loading gymnastics! Only need admin!
sabotage retweeted

Whether you're learning x86 instruction encoding or writing YARA rules, ZydisInfo is an amazing (yet slightly underrated) tool for the job.

sabotage retweeted

Today, we’re releasing watchTowr Labs’ @chudyPB’s BlackHat .NET research, owning Barracuda, Ivanti and more solutions.
Enjoy the read as Piotr explains a new .NET Framework primitive, used to achieve pre- and post-auth RCE on numerous enterprise appliances.
labs.watchtowr.com/soapwn-pw…

sabotage retweeted

New blog by Outflank’s @KyleAvery: Linux process injection leveraging seccomp to inject shared libraries into Linux processes without LD_PRELOAD, ptrace nor elevated privileges.
Parent-to-child injection at any ptrace_scope level 💪😎
Tech details here: ow.ly/KwBh50XGvrC
sabotage retweeted

Thank you all for helping me choose the cover for the Go Concurrency book. I didn't expect so much participation, and I really appreciate it!
Here's the final version, along with the table of contents.

sabotage retweeted
Low-Level Software Security for Compiler Developers
If you ever wanted a textbook-style guide to memory safety bugs, undefined behavior, exploit mitigations, side channels, etc.
All in one spot, this free book is it:
llsoftsec.github.io/llsoftse…

sabotage retweeted

New Amazon Threat Intelligence findings: Nation-state actors bridging cyber and kinetic warfare
aws.amazon.com/blogs/securit…
