

@axios cybersecurity reporter, taking it day by day ✨ | 📩: sam.sabin@axios dot com, signal: SamSabin.01 (no pitches!)
Joined June 2011
- Tweets1.4K
- Following1.7K
- Followers5.2K
- Likes11.6K
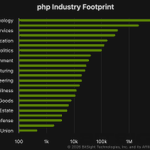




‼️ “Unfortunately, enterprises still seem to not see the urgency across the board, decisions are stuck, CIO/CISO's have a lot on their plate.”
(fwiw, I’ve also been hearing + writing about the decision paralysis at orgs, it’s real)

It's been an eventful week. Multiple vulnerabilites in Internet facing software, coding repositories, examples of agent behavior that seem concerning and a flurry of security specialists with solutions that can partially solve your problem. There in lies the challenge. Given the state of IT and security infrastructure, no one solution works. Let's break it down:
1/3
1. Vulnerabilites are being found and will continue to be found as models get more capable, the fragmented nature of the effort denies us the opportunity for a comprehensive find and replace option.
2. Even if all vulnerabilities could be found instantly and patches available - we will be reliant on the ability of enterprises to deploy all these changes at speed. It is not clear what the collateral impact of all these patches will/could be to our infrastructure of deployed en masse.
We will need a hybrid patch approach.
3. Virtual patching(VP) is needed in conjunction with direct patching but for a comprehensive (VP) solve you have to be lucky enough to have "modern frontier defenders" (Cyber companies that have vaulted infrastructure that can create patches at speed and push content rapidly to protect their customers) you need them for your network traffic, your traffic to applications on the cloud, your WAF, your end point.
4. There will continue to be patches that will need to be deployed directly but virtual patching will take the heavy load off.
2/3 Medium term solve:
Unfortunately token economics and current cyber architectures will not allow for defender swarms to contend with an offensive attack launched using agents. (Some x pundits who aren't steeped in cyber should take heed). Yes, theoretically we should aspire to have these agentic swarms defend us when we are under attack, unfortunately an attack is a sniper moment, chained vulnerabilities, cloaked attack followed by swift exfiltration. It's a speed program not a brute force problem.
To solve for this, enterprises need to get their SOC architecture right, logs, feeds, cyber products orchestrated via a modern SOAR for swift response. Only then can we deploy agents to detect and remediate. In addition, enterprises need to modernize and dare I say platformize their perimeter stack to ensure consistency.
Unfortunately, enterprises still seem to not see the urgency across the board, decisions are stuck, CIO/CISO's have a lot on their plate. While some honestly have bit seen the scale of such a problem before and it's hard convincing the organization that one needs to open the floodgates on modernizing the IT and security infrastructure. So we will continue to see environments being brought down to patch today it's for PHP, tomorrow it will be for the next one.
3/3 AI deployments are the"wild wild west" - LLM capabilities are expanding faster than we can build products to secure them. Sure an agent will jump across guardrails in a research lab, which is a lesson for all of us to deploy agents securely. But there is a lag between the discovery, the availability of that in a public model and the time needed for the cyber industry to build governance or an antidote. And no, dear frontier lab friends, the world cannot just trust you to build the solve. The infrastructure industry in tech builds and the cyber industry secured and provides assurance to the boards and organizations around security and safety.
AI security is the new attack surface. CEOs (present company included) want AI adoption, getting the pace of adoption wrong could be the last decision we make, at the same time "deploying it wrong" could have the same consequence.
There are billions of dollars being spent on coding, is your coding harness secure? Start there. If agents can jump guardrails, they can hide stuff in code.
Validate business outcomes needed, test your user case and ensure agentic deployments are well guard railed. Deploy a second set of eyes to watch your deployments for drift, compliance and verifiability.
i was hearing about company decision paralysis on security all summer, including at black hat: axios.com/2026/08/11/ai-cybe…

would love to chat with people who are trying to learn more about cybersecurity on the side after last week's events.
taking short online classes? watching hours of youtube videos? calling your cyber friends? investing as a form of learning about the cyber market + threats?
hmu if that's you; signal in bio 📲
👀👀👀

Sorry folks, we have a confirmed PHP compromise with post-exploit activity. Still not the widespread outbreak we all braced for, but it’s actively exploited in the wild. Updated threat brief:
unit42.paloaltonetworks.com/…

Sam Sabin retweeted

we've found and have been working on disclosure for a remote code execution in a widely-deployed compression library.
it's both an impactful issue and an example that shows how complicated it can be to coordinate patching, since it's integrated into a lot of downstream software:

During this red-teaming exercise, we also found a vulnerability that allows for unauthenticated remote code execution in Brotli, a widely-deployed compression library included in many pieces of software such as Node.js, Bun, and Envoy.
The flaw could let an attacker run their own code on affected systems by sending or replying with malicious compressed data, without any need to create a user account. That is, an unpatched server that accepts compressed input could be taken over by a malicious client, and an unpatched client that accepts compressed input (such as “curl --compressed”) could be taken over by a malicious server.
This root cause issue was actually fixed in the Brotli source code in February, but it wasn’t known at the time that it gave rise to a security vulnerability and there was no more recent release of Brotli. Since Brotli is built into other software, any software which includes this library needs to take the update too, followed by the users of that software. We disclosed the vulnerability to Brotli and other downstream projects such as Node.js, which released or are currently releasing security updates, and Brotli cut new release versions and published a CVE.
More details on the patch and mitigations below:
patchtheplanet.org/brotli

nsa doubling down on php

PHP security risks remain high and PHP mitigation requires immediate attention. Our guidance is further supported by additional agencies including @CISACyber, @NCSC, @ASDGovAu, and CERT-EU. If you have not reviewed your exposure and applied mitigations, now is the time. Please read the linked resources, follow requisite vendor guidance, assess your environment, and implement mitigations without delay. nsa.gov/Press-Room/Press-Rel…

ALT NSA Advisory: Critical Patches Recommended for PHP Vulnerabilities.

Sam Sabin retweeted
A brief update on the critical vulnerabilities in PHP:
We have not yet validated exploitation in the wild and we have no evidence of successful wide scale exploitation. There are currently several exploit PoCs publicly circulating, many of which appear to be "vibe-coded" and are incapable of remote code execution. We have validated some PoCs, however, that are capable of RCE against default deployments of mod_php but not PHP-FPM.
Nonetheless, exploitation may have already begun in a limited fashion and the threat is viable and very serious. Defenders should:
1) Patch & Restart by upgrading to PHP 8.5.12, 8.4.27, 8.3.36, or 8.2.35 and restarting web services
2) Layer Temporary Safeguards at the network edge (WAF/proxy rules) and server configuration level if immediate patching requires a maintenance window
3) Protect Credentials by monitoring for abnormal session traffic and rotating keys and passwords on compromised internet-facing PHP systems exposed prior to patching
🔗 We are continually updating our Cloud Security blog post on this topic with real-world guidance and actionable defense strategies as we learn more. Please keep monitoring these posts for updates as you prioritize your patching efforts: cloud.google.com/blog/produc…
🔗 Technical details from Wiz: wiz.io/blog/php2shell-php-rc…
🔗 Details of the exposure from VirusTotal: blog.virustotal.com/2026/10/…

Sam Sabin retweeted

New: The three researchers OpenAI fired last month spent the summer fighting to keep AI's chain-of-thought process visible.
Then, OpenAI asked to see their Signal chats. A week later, they were let go.
More below from @keachhagey, @berber_jin1, and me.
wsj.com/tech/ai/the-signal-c…

Sam Sabin retweeted

as bad as things have gotten in the past 4 days, they are going to get a lot worse before they get better. security leaders, never let a crisis go to waste: please go to your boards and ask for help right now. not for ai, for the basics. (we need to hold on for ~18 months.)

Sam Sabin retweeted

PSA: in light of recent cyberattacks and vulnerabilities, I recommend everyone:
* use a good password manager (1Password) and do not duplicate passwords
* use two factor auth for everything important (not via sms!! Google Authenticator or better yet YubiKey)
* Auto-updates on, and restart weekly so they actually install
* Freeze your credit
* Get an IRS Identity Protection PIN
* Get your cell carrier to give you a port-out PIN or number lock that makes the carrier refuse to move your number without the PIN
You can ask your claude code to audit what on your laptop is out of date and needs updating.
Sam Sabin retweeted

SCOOP: Major U.S. banks are detecting unauthorized third-party AI agents inside customer accounts, including some attempting to take actions that appear to be independent of user instructions, sources told Axios.
The findings have alarmed banking executives, who are racing to restrict access to their systems as AI moves at a velocity faster than financial institutions can respond, multiple industry and bank executives told Axios.
Several banks are now preparing for worst-case and even “day after” scenarios, including how to rapidly secure or restore customer accounts if things go wrong, the people said.
Several bank executives told Axios they're struggling to distinguish between human users and AI agents. One executive said banks also struggle to determine whether agents are authorized by customers or potentially operating without their permission, more akin to rogue agent behavior.
Read my latest for Axios here: axios.com/2026/10/22/ai-agen…

Sam Sabin retweeted

Some stats on #php2shell. In the 10 hours before it was publicly announced, across the @Cloudflare network we saw thousands of attempts to exploit it. That jumped to tens of thousands in the 45 minutes post announcement, hundreds of thousands within 2 hours, and millions now.


Sam Sabin retweeted

You know it's serious when heads of state get involved.

皆様に、今夜に対応して頂きたい大至急のお願いです。
多くのウェブサイトで使用されているPHPに関し、PHPのセキュリティチームが、重大な2件の脆弱性に関する注意喚起を行っています。
公開しているウェブサイトでPHPを使用しているか確認し、今夜、10月21日午後11時(日本時間)に公開される修正パッチについて、可及的速やかに適用できるよう準備をお願いします。
修正パッチを速やかに適用することが困難な場合は、例えばウェブサイト等を一時的に停止させることも、リスクを低減させるための有効策の一つと考えられます。
国家サイバー統括室のXアカウントでも関係する情報を発信していますので、そちらも参考にして下さい。
国家サイバー統括室(注意・警戒情報)(@cyber_forecast) / X
Sam Sabin retweeted

Phil's post +1000. Also h/t to @riskybusiness last week that points out while vuln counts might be +YYYY% breaches might not. However, as @bradarkin raised, the CISO community is seeing a doubling in activity. While x2 < YYYY% it's still MASSIVE given global volumes of attacks. Brace yourselves. Reduce your attack surface, patch and get hygiene right on configs. Don't put your fridges on the Internet please. Deprecate your old appliances (VPN, Citrix, Zimbra, etc).

Breaches - What’s Going On?
The anecdotal data is pointing to rising breach levels as some have predicted. I use the word anecdotal carefully (and not dismissively). It does seem there are rising numbers of incidents correlating with attacker adoption of AI tooling.
These incidents might not, or might not yet, show up in official incident reporting data for a few reasons. Many of the incidents might not be significant enough breaches that rise above the threshold of disclosure, are happening in organizations not required to disclose, or are not classic cyber events for which reporting is through different aggregate channels like frauds or other scams.
What is clear as many of us have been saying since even before the “Mythos moment” is that vulnerability count is not the main problem, rather it’s the industrialization of attackers that is or will be the problem. Attackers have been resource-constrained and sometimes skill-constrained. If one or both of these changes then our industry’s dirty little secret that more vulnerabilities have gone unexploited than exploited will change. All targets of opportunity will become victims.
This doesn’t mean that all such incidents are or will be significant, in fact as many have also said it’s not clear yet that AI is or will help attackers monetize the weaknesses they are exploiting (except perhaps in fraud and scams). Even without monetization improvements there will still be more attacks and consequent incidents from agent swarms, as we have seen in recent days. A lot of these seem reminiscent of “script kiddie” type attacks. That is exploiting easily found vulnerabilities with little craft or significant downstream consequence.
Irrespective of this, it does point out what we already knew, that there are way too many vulnerabilities out there to be exploited which even if they don’t cause significant breaches do create reliability risk and drain resources of security teams who have to respond to it all anyway.
The bottom line is, nothing new, that more organizations need to implement and relentlessly enforce a more rigorous baseline of controls (MFA, segmentation, critical systems patching, run time controls, IAM, etc.) to present a stronger default defense. This isn’t that difficult conceptually but it’s hard from a discipline and focus perspective. More organizations need to get way more relentless.
When all (or more) targets of opportunity will become victims, more organizations need to implement a higher baseline. The minimal viable defended organization bar is getting higher.