

Sub-brand of @0xbitslab. We're a Blockchain Security Team that Provides Proficient Audit Solutions for the Mass Adoption of Web3
Joined June 2023
- Tweets608
- Following247
- Followers3.3K
- Likes859






🛡️ Remediation
Qubic has ⚒️ fixed the Seed generation issue in wallet version v4.26.4. Further decisions on the recovery and disposition of the stolen funds will be made by the Computor quorum in accordance with network rules. ✅
A Seed-generation flaw affected certain wallets, while the underlying blockchain protocol remained unaffected. Computors halted the network at Tick 85,371,949. About 87.1% of stolen funds were frozen on-chain; the remaining 12.9% went to MEXC, where related accounts were frozen.


6/6 ScaleBit Security Insight 💡
A K-invariant check is useless if its math can overflow.
✅ AMM/DEX audits should test integer widths, casts, extreme reserves, invariant enforcement, router access, and fuzz testing.
#ScaleBit #EtherVista #DeFiSecurity #SmartContractAudit
5/6 Why SafeMath Didn’t Help 💨
Elsewhere, EtherVista uses uint(reserve0).mul(reserve1), casting to uint256 before multiplying. But swap() uses reserve0 * reserve1 directly.
⏳ SafeMath in one code path doesn't protect another. Router access can't fix a broken invariant.
4/6 A Simple Example 🔦
If reserve0 = reserve1 = 2^60, the true product is 2^120. But in 112-bit arithmetic:
2^120 mod 2^112 = 0
🧾 The check may pass even when the actual reserve product drops sharply.
Illustrative numbers, not the actual attack parameters.
3/6 Root Cause ⛓️
require(balance0 * balance1 >= reserve0 * reserve1, "K");
balance0/1 are uint256; reserve0/1 are uint112.
In Solidity 0.5.16, multiplying two uint112 values can wrap modulo 2^112, leaving the K check with a falsely low baseline.
2/6 What Happened 👾
Public analysis points to two crafted swaps through an attacker-controlled, authorized router. The swaps passed the contract’s K check even as the pool’s actual reserve product fell.
📡 How the router was authorized remains unverified.
🔍 EtherVista Exploit: An Integer Overflow in an AMM’s K Check
On Oct 9, EtherVista reportedly lost 💸~$18.6K in WETH and VISTA. The issue was in EtherVistaPair.swap(): an overflow broke the constant-product check, letting invalid swaps drain liquidity.
Here's how it works🧵👇

8/8 | ScaleBit Security Insight
✍️ Cross-chain audits must test trust boundaries, access control and consistency from accounting to settlement.
ScaleBit, sub-brand of @0xbitslab , focuses on multichain smart contract security. ✊
7/8 | Audit takeaway
🔦 Cross-chain smart contract audits must cover the full flow:
Deposit → Balance Accounting → Withdrawal Authorization → Settlement.
🥏 Test proof-to-balance consistency, nonce replay resistance and asset conservation across failures and edge cases.
6/8 | Fund movements
🔑 Bitquery traced USDT swaps into BNB and transfers through fresh wallets. About 76% was converted to BTC, some funds reached exchanges, and ~$822k moved via NEAR Intents itself.
On Oct 2, Alex Shevchenko said the stolen ~$3.8M was fully returned. ✊
5/8 | Root cause: what's known?
💼 NEAR Intents confirmed a flaw involving Omni infrastructure and its contracts. The failing function remains undisclosed.
💡 Audit checks: valid balance burns, proofs bound to chainId/token/amount/recipient/nonce, and replay-safe settlement.
4/8 | Signed withdrawals
A valid signature doesn't prove a withdrawal is fully backed.
🛢️ A destination vault relies on upstream balance accounting, withdrawal state and proof issuance. If an improper withdrawal gets signed upstream, the vault may still accept it.
3/8 | Attack timeline
Bitquery traced two test withdrawals (10 and 11 USDT), then five more over ~6 hours:
💸 800k → 1.2M → 1.5M → 330k → 35k USDT.
Only 10 USDT in prior BNB Chain deposits was traced to the attacker. Their full cross-chain balance is unverified.
2/8 | How withdrawals work
Per HOT Omni Bridge docs, Locker contracts hold and release assets; Omni Balance manages balances on NEAR; MPC validators sign withdrawals.
After a burn on NEAR, the destination vault checks the signature and nonce before releasing funds.
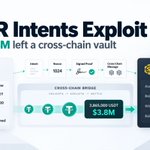
🚨How did $3.8M leave a cross-chain vault?
On Oct 1, @near_intents disclosed an exploit involving its Omni deposit/withdrawal system. An attacker withdrew 3.865M USDT from a BNB Chain vault in five transactions, each accepted with signed withdrawal proofs.
Here's how it works👇
