

Infosec and Bug Bounty
Spain
Joined June 2020
- Tweets1.2K
- Following150
- Followers1.6K
- Likes3.2K



Pinned Tweet
Recently I don't tweet much, but today has been a beautiful day that made me feel better after some other disappointments:
9th in Spain 🇪🇸 and a great impact!
A year or so ago this was unthinkable for me 📈
Thanks #BugBounty


𝕵𝖔𝖙𝖆 | jotita3 retweeted

🚀 Your next security finding could earn you double the rewards.
@Deriv has launched a two-week bug bounty campaign on HackerOne, offering 2× bounty rewards for eligible Medium, High, and Critical vulnerabilities.
Running from November 10–24, the campaign gives security researchers an opportunity to put their skills to work, uncover meaningful vulnerabilities, and help strengthen Deriv's security.
Ready to take on the challenge? 🎯
Explore the campaign and submit your findings: bit.ly/4fp9Pnz

ALT Deriv bug bounty campaign
𝕵𝖔𝖙𝖆 | jotita3 retweeted
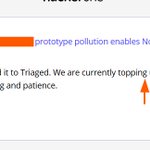
• Triage is extremely slow or practically nonexistent: This is something affecting all platforms, and from what I understand, Bugcrowd has recently expanded its triage team, which seems like a positive step. It's also true that, since my account is "new", I probably don't get much priority in the queue. But even so, the delays are honestly ridiculous.
• Reports get closed with canned responses such as:
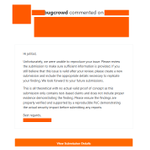
‣ "We were unable to reproduce your issue" → OK, fair enough, but can we discuss what went wrong? Why immediately close it as N/A and call it a day?
‣ "If you still believe that this issue is valid after your review, please create a new submission" → So the solution is to keep flooding the triage queue instead of keeping the entire discussion in a single report? Am I supposed to submit the same issue X times until I finally get a triager who can reproduce it?
‣ (This one is probably my favorite lol) "This is all theoretical with no actual valid proof of concept as this submission only contains text-based claims" → What exactly do you mean by "theoretical" and "no PoC"? Isn't source code, raw HTTP requests, and step-by-step reproduction instructions a PoC? Does the vulnerability suddenly cease to exist? Or, put differently, if I fill my report with screenshots and pretty decorations, does that suddenly make me a super hacker? (This is a made-up example: Do I really need to attach a screenshot of alert(1) so you don't have to test the vulnerable request that triggers that same alert(1)?)
• I open blockers (= requests for Bugcrowd's intervention, somewhat similar to mediation on H1) and, of course, nobody from Bugcrowd responds.
Examples
• In one report, the company's own staff opened a blocker requesting Bugcrowd to assess the impact. Since Bugcrowd never responded, the company had to handle the entire report and pay the bounty without any assistance from the platform (which, I assume, they're paying for...). And here's the cherry on top: once the company had already paid, the vulnerability had been fixed, and everything was resolved, Bugcrowd finally showed up!!! And what for, you might ask? Well, to update the report status and award me some internet points (Very useful!!! Please note the sarcasm.)
• I gained access to a company's Dropbox through a leaked API key exposed on a subdomain associated with one of its programs. A pretty serious impact, in my opinion, and certainly not the kind of access you'd want a real attacker to have. Well, the solution was simple: N/A. Because, of course, since the subdomain wasn't explicitly listed in scope, we should apparently understand (sarcasm again) that we can't act ethically and report unauthorized access to a service because, oops, I happened to inspect the source code of an OOS subdomain... (As if the root issue in my report were a vulnerability in that subdomain rather than an API key leaked through whatever means.)
2/4 🧵

𝕵𝖔𝖙𝖆 | jotita3 retweeted
I also want to share my experience with @Bugcrowd, since it seems I'm not the only one:
Initial context
Since incorporating AI into my workflow, I've been able to significantly increase the number of vulnerabilities I discover and report while spending roughly the same amount of time on Bug Bounty as before.
Instead of simply doubling my submissions to HackerOne, I wanted to diversify and give Bugcrowd a try. It was a platform I was barely familiar with (in terms of how they operate, what programs they offer, etc.), but I found it interesting because of the well-known companies running programs there and bounty tables comparable to those on H1
My experience with the platform
Since August this year, I've been submitting reports with genuine enthusiasm and confidence about starting my journey here. Unfortunately, the experience has been nowhere near what I imagined.
Here are my main issues and criticisms:
1/4 🧵

Triaging experience at @Bugcrowd is extremely bad, even the valid demonstrated findings with POC and high - critical impacts are being marked N/A with templated comments.
I also want to share my experience with @Bugcrowd, since it seems I'm not the only one:
Initial context
Since incorporating AI into my workflow, I've been able to significantly increase the number of vulnerabilities I discover and report while spending roughly the same amount of time on Bug Bounty as before.
Instead of simply doubling my submissions to HackerOne, I wanted to diversify and give Bugcrowd a try. It was a platform I was barely familiar with (in terms of how they operate, what programs they offer, etc.), but I found it interesting because of the well-known companies running programs there and bounty tables comparable to those on H1
My experience with the platform
Since August this year, I've been submitting reports with genuine enthusiasm and confidence about starting my journey here. Unfortunately, the experience has been nowhere near what I imagined.
Here are my main issues and criticisms:
1/4 🧵
Triaging experience at @Bugcrowd is extremely bad, even the valid demonstrated findings with POC and high - critical impacts are being marked N/A with templated comments.
Conclusions based on my own experience and small sample size
• Poor management of report volume, especially given the current state of vulnerability research.
• Overwhelmed triagers whose easiest option seems to be closing reports, trusting that the researcher will submit a new one that better matches whatever the triager expects, requiring the least possible effort on their part. I fully understand that researchers should make the triager's job easier, but that's very different from expecting every vulnerability to be a one-click or one-step exploit so the triager can just chill.
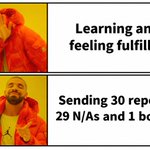
• The meaning of N/A seems completely distorted compared to other platforms. How is it possible that there's no room for technical discussion within reports and that potentially valid bugs are being lost because N/A is being handed out as if those reports were spam?
• Canned responses with no real value or transparency. It doesn't matter whether you submit a P1/P2 that, for whatever reason, the triager can't reproduce. In practice, you'll receive the same N/A as someone reporting a missing security header lol.
• A terrible initial experience due to submission limits and little to no prioritization in the triage queue simply because you're "new". And I understand the reasoning behind that, but shouldn't we be taking researchers' track records on other platforms into account? If I have almost 2.5K reputation points on HackerOne and a historical signal above 6.3, shouldn't that count for something when establishing credibility on your platform? Instead, you're actively pushing me away from it.
3/4 🧵
1
12
887
Clarifications
• I'm not trying to single anyone out. There are better and worse professionals everywhere, as in any industry.
• I'm not questioning the triagers' level of expertise or technical knowledge.
• I believe the real issue lies with Bugcrowd's management and leadership for neglecting both their customers and researchers.
• I don't wish the platform any harm. I genuinely want what's best for the ecosystem and for everyone involved to benefit. A win-win for all.
4/4 🧵
1
10
785
Incredible bugs still waiting to be discovered, and companies already running out of bounty budgets...
What a crazy time to be alive in the AI era. But today, I'm happy!
#bugbounty #hackerone

💡Tip:
It was a bit more complex, but take a look at this lab to get a basic understanding 👉 portswigger.net/web-security…
Done! Now let’s go for 100!🚀
#bugbounty #hackerone


I've reached 20 thanks from companies on @Hacker0x01 ! For many, it may be a small achievement, but for me, it's really exciting!
On to 50😎

2
20
635
I see people doing really well on @Bugcrowd, while my experience has been absolutely horrible. Am I the only one?
1
152
𝕵𝖔𝖙𝖆 | jotita3 retweeted

It’s a numbers game.
If my AI slop bot submits a few thousand submissions, at least one or two should be valid and pay out.
Overall, I’m not having my best day today... and when I’m having a bad day, I tend to come here to vent... sorry lol. Let me tell you what’s going on:
The thing is, my income and the number of reports I submit have improved massively since AI became part of our lives. And yet, I don’t feel happier, quite the opposite.
I feel more like a slave to it. Like we’re just “manufacturing” money now. Like there’s no longer much point in enjoying the technical side of things. I see newcomers achieving in days what took me months or even years of effort to accomplish. Now it feels like we’re all competing on equal terms, but without necessarily having the same level of knowledge or experience.
I also feel like all of this could disappear from one day to the next, or that I have to keep farming more and more every single day because otherwise the person next to me will sweep everything up and take the opportunities before I do.
And then there’s seeing all these unfair flexes on social media, which inevitably creates FOMO, especially when they come from people who sometimes seem to have very little actual knowledge...
I’m not enjoying the moment... I don’t know how to deal with this situation. AI has messed with my dopamine.

I wasn’t sure whether I was going to report it... sometimes your favorite report gets closed, and other times an unexpected one makes your morning. Nice program!
That’s just how bug bounty goes 😅
Have a great day everyone!

𝕵𝖔𝖙𝖆 | jotita3 retweeted

Mañana Bugs & Talks - #4 @moblig_
Video: youtu.be/C6J_fR32pcc?si=TfcA…
#bugbounty #podcast #ciberseguridad

𝕵𝖔𝖙𝖆 | jotita3 retweeted

Seguimos desvelando el cartel del #BugSummit y este nombre viene con una charla que promete dar mucho que hablar.
El próximo 20 de junio subirá al escenario de La Nave Juan Antonio Rodríguez Bautista @sec_jota, más conocido como Jotita3, una de las caras más reconocidas del panorama nacional del Bug Bounty y alguien que ha demostrado, una y otra vez, cómo pequeños fallos pueden convertirse en grandes compromisos de seguridad.
En su ponencia, "𝗔𝗰𝗰𝗼𝘂𝗻𝘁 𝗧𝗮𝗸𝗲𝗼𝘃𝗲𝗿: 𝗘𝗹 𝗮𝗿𝘁𝗲 𝗱𝗲 𝗰𝗼𝗻𝘃𝗲𝗿𝘁𝗶𝗿 𝗯𝘂𝗴𝘀 𝗲𝗻 𝗰𝘂𝗲𝗻𝘁𝗮𝘀 𝗿𝗼𝗯𝗮𝗱𝗮𝘀", compartirá casos reales de Bug Bounty donde vulnerabilidades descubiertas en entornos reales terminaron derivando en compromisos completos de cuentas.
Analizaremos fallos directos y escenarios más elaborados que permitieron tomar el control de cuentas, entendiendo el impacto real, la causa raíz detrás de cada hallazgo y las lecciones aprendidas durante el proceso.
Casos reales, metodologías prácticas y la visión de alguien que ha vivido este tipo de hallazgos desde dentro.
Será, sin duda, una de esas charlas imprescindibles para cualquiera que quiera entender cómo un bug aparentemente inofensivo puede acabar convirtiéndose en un Account Takeover.
Si quieres aprender de quienes viven el hacking en primera línea, la cita es el próximo 20 de junio.
Consigue tu entrada aquí 👉secur0.com/es/feria-de-emple…
#BugSummit2026 #BugBounty #AccountTakeover #Ciberseguridad #EthicalHacking #TechConference


