Secureframe is the automated compliance platform built by compliance experts. We're transforming how businesses and MSPs manage security & compliance programs.
San Francisco, CA
Joined January 2020
- Tweets1.7K
- Following150
- Followers2.2K
- Likes561
People keep asking me for the SOC 2 controls list. There isn't one. You pick controls to cover up to 61 requirements, and in a Type 2 a single skipped access review can become a written exception. Best breakdown I've seen: hubs.li/Q04BMCl50

Redspin: about 47% of 131 DIB contractors are still pursuing third-party CMMC certification despite the Phase 2 pause, and 60% cite customer and prime expectations. If you've done the work, make it easy to see: hubs.li/Q04BMCl40

A stolen ConnectWise Cloud Backup credential got attackers into at least 162 Microsoft 365 tenants, per Huntress. They never had to break into those orgs. The vendor's access was already inside. The third-party stats here are worth a look: hubs.li/Q04BMC-W0

MITRE's ATT&CK v20 now lists the 2026 water utility attacks as a campaign: 30+ Minnesota utilities, internet-exposed PLCs, default credentials, operators locked out. If your shop floor runs PLCs, this NIST 800-82 primer is worth your time: hubs.li/Q04BMFs20


The attacker behind Denmark’s national register breach (8.8M people) claims they got in through a vendor account with the password “123456.” Reportedly three accounts used it, admin included. Your policy is only as strong as your vendor’s: hubs.li/Q04B19y30

Attackers cranked up fridge temps at hundreds of French supermarkets and stretched defrost cycles to delay alarms. Not a DIB incident, but if a vendor can reach your plant equipment remotely, so can an attacker. Know what comes back first? hubs.li/Q04B19wJ0

DoW opened October with a Brilliant at the Basics push covering IT and OT. Then NSA released zero trust guidance for OT, written partly for DIB owners. When the government keeps pointing at the plant floor, contractors should look too: hubs.li/Q04B19x30

Third parties were involved in 48% of breaches this year, up 60% (Verizon). What surprised us more: only 23% of them fully fixed missing or weak MFA on their cloud accounts. Vendor risk is a remediation problem now: hubs.li/Q04z6lHs0

Cybersecurity Awareness Month exercise: run your top risk through the ALE math. A $12K/yr control that cuts expected ransomware loss from $20K to $4K a year pays for itself. Six methods to try: hubs.li/Q04z6lCY0

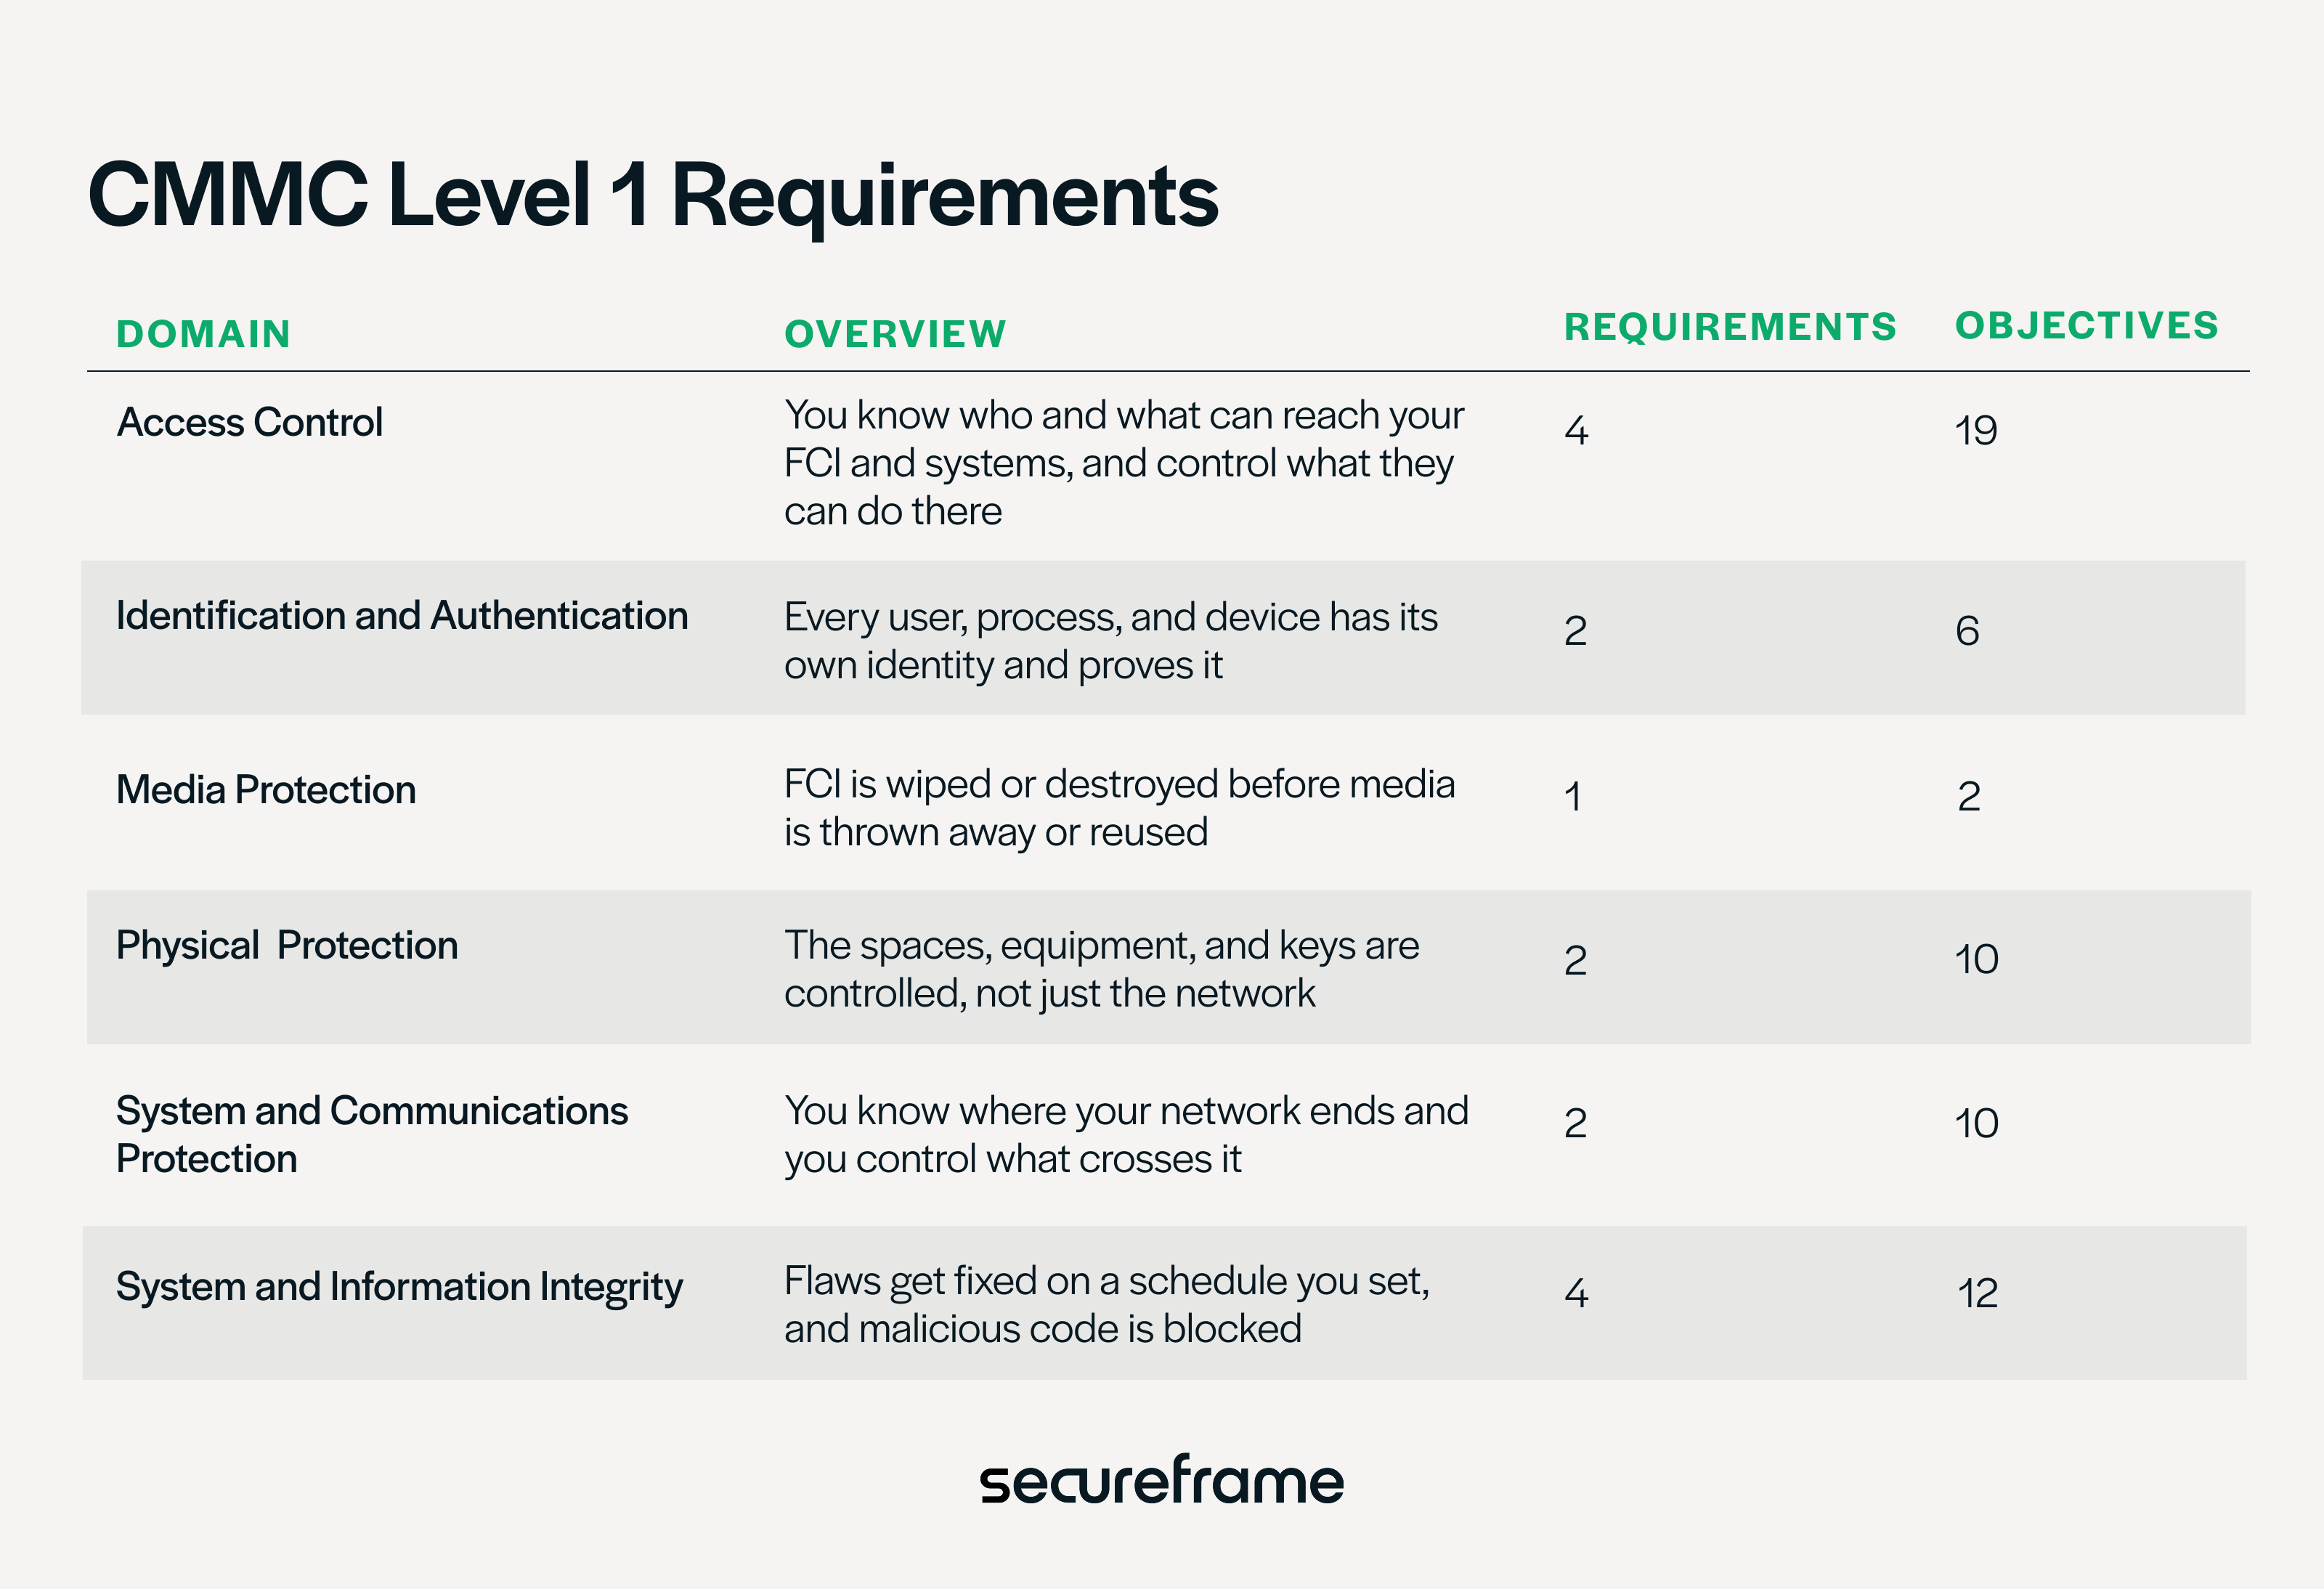
No CMMC task force report yet, but Level 1 self-assessments are still required. The catch: 15 requirements hide 59 objectives, with no partial credit and no POA&M. This guide says exactly what to do for each: hubs.li/Q04z6lGP0