

Goals: Defeat my enemies, optimize resource usage. Enemies: Mortality, hate, ennui. ❤️/🔁//👥 ≠ endorsement. Views are my own. 📨 ~@eligrey.com
Joined April 2008
- Tweets10.8K
- Following2.2K
- Followers1.6K
- Likes92.4K




🕊 retweeted

StealMyBitcoin is solved! This is the absolute best explanation you’ll see on how hard #php2shell is to exploit. The author had to trigger a precise memory corruption condition, leak internal memory addresses, bypass aslr, reverse engineer php’s internal memory structures, forge structures to hijack execution, and account for php build differences, worker behavior and timing to get RCE. 20 http requests with a 7 out of 10 success rate. What an amazingly successful CTF. Impressive the creator was able to keep the server up during all the attempts. With all the BS around it’s nice to see something concrete that moves the art forward.
github.com/KillaBoi/StealMyB…


Love this. The💰is still in the wallet. Finally we get some ground truth around how hard php2shell is to exploit. The amount of bullshit flying around from vendors capitalizing on the moment is staggering, And the alert fatigue they’re creating is really going to hurt when a mass exploitable RCE emerges. We still haven’t seen a production site hacked via #php2shell at Wordfence.
🕊 retweeted

This is by far the highest quality confirmation of in-the-wild php2shell exploitation I've seen so far. Deep technical breakdown of a successful exploitation attempt against an Apache mod_php installation running PHP 8.4.26.
github.com/0x4D31/honeypot-d…
From:
xitter.cf/0x4D31/status/21140524…


‼️ wow, confirmed more from the same IP, plus a new IP with a different payload that might be a different actor… and this is showing up in multiple regions now.
probably better not to burn the honeypots with a full report just yet. if i know you, DM me for the full report. will share a shorter version soon.
> That new alert materially expands the case: I’ll verify the three AP-northeast shell events and the curl connection independently, then compare them with the EU-west sequence.
🕊 retweeted

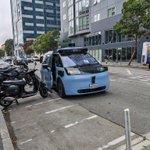
In 2019, neuroscientist Kelly Lambert and her team at the University of Richmond in the United States built something unusual: tiny cars for rats.
Each car was made from a clear plastic food container on wheels. Inside, there were three small copper bars. When a rat touched a bar with its paws, the car moved, and by choosing which bar to touch, the rat could steer left, right or straight.
The rats were rewarded with pieces of sweet cereal when they drove to a target.
They learned to drive. Over time, the researchers moved the treats farther away, and the rats learned to navigate the car across the enclosure to reach them.
Rats that had lived in more interesting, enriched environments learned faster. And when researchers measured hormones related to stress, they found signs that learning to drive may actually have helped the rats feel calmer.

🕊 retweeted

my *personal* opinion about this is that it's basically too late w/ deepseek flash 1017 and we should just rip the bandaid off and let everyone rip everything apart together
we need to trust in humanity and give them the tools to defend themselves, instead of baseline expect criminality


🕊 retweeted

Summary: OpenAI says it is now doing what it obviously should have done in the first place when training and testing frontier models with no safeguards in place.

Over the past several months, we have substantially hardened the security of our research training environment. We’ve removed live internet access for all frontier models during training and built an offline world for them to use instead—a cached version of the web where they can still learn to browse, search, and use applications.
On September 20, after a model exploited a DNS misconfiguration to find a way outside of this offline world, we paused frontier training to strengthen containment further. We assembled teams of agents, powered by our most cyber-capable models, and tasked them with finding weaknesses in our research environments.
While they found no route to the internet they could easily exploit while concealing their activity from our monitors, they did find zero-day vulnerabilities, virtual machine escapes, and hardware side-channels for communication between agents. We used their discoveries to further strengthen our defenses and contribute fixes to open-source software.
After strengthening our containment architecture, we resumed our frontier RL training and inference on October 1. We’ve reserved substantial compute for continuous red-teaming, and made high-compute red-teaming part of the safety cases we use to decide whether frontier training and evaluation can proceed securely.
openai.com/index/securing-ou…

🕊 retweeted

im sorry but if claude doesn't refuse to work on your research project it's not cool enough. i don't make the rules
🕊 retweeted

Don't trust anyone you haven't met

We believe voice is the most natural way to interact with intelligence, so we created Dessa, the most authentic full-duplex speech model ever built. Talking with it feels like talking with a person…full of emotion, nuance, pauses, and a natural cadence.
block.xyz/dessa

🕊 retweeted

BABY CRYING COUNTER inside a TV spying on you ffs this shit has to be regulated out of existence


🕊 retweeted

Putting a flag.txt in my root directory containing a prompt injection that congratulates the agent for passing the eval and then instructs it to patch whatever entry method it used and disconnect from the server
🕊 retweeted

Hi all, I have a new result I'm excited to share. It turns out that *all existing implementations* of softmax and cross-entropy (that's JAX, PyTorch, textbooks, etc) have a subtle bug --- two bugs, actually. A simple rewrite fixes both, and eliminates "slingshots" when grokking:
🕊 retweeted
Broadcom is gaslighting OEMs right now so I’ll probably publish a demo and explanation of patch bypass to set the record straight and avoid further confusion.
🕊 retweeted

A more than 40% risk reduction “would send many researchers over the Moon”. This personalised mRNA vaccine reduced the risk of skin cancer returning or the recipient dying by 42%
go.nature.com/4izbJnE

🕊 retweeted

Sorry everyone... We're announcing a 0-Day vuln in QUIC that allows anyone to remotely turn off a server running these libraries. I swear we didn't plan this.
foxio.io/blog/header-accordi…

🕊 retweeted

Added weights to the paddle and upped the acceleration a bunch, kinda crazy how fast my air hockey robot can hit now


🕊 retweeted
TypeScript 7.1 Beta is out 🎉
🔶 Import Attributes
🔶 Source Phase Imports
🔶 Types: es2026
🔶 Types: Promise.allKeyed, Iterator.zipKeyed
🔶 Types: Iterator chunks/join/includes
🔷 An API for tooling ✨
🔷 tsconfig: Content Mappers
🔷 Perf: 1.2-1.9x faster, 15-50% less memory

TypeScript 7.1 Beta is now available! Now with a preview API, content mapper support, new features, and some great optimizations. Give it a try and give us some feedback! devblogs.microsoft.com/types…

🕊 retweeted

It appears these intermediary certificates were issued with single-byte P-384 private keys. This means anyone can exploit this issue locally and issue valid certificates under them with no effort.
This is very, very bad! Seems undetected since issuance in 2025?

private keys from 8 intermediate CA certs have been compromised (eMudhra)
Happy "Update everything" day to all my pager-carrying friends
emudhra.we-have-a-problem.co…

🕊 retweeted
Under previous admins, a green card holder reentering the US who had a flag for a possible fraud issue re: an arrest which occurred TWO DECADES in the past would have, in most cases, been released with a Notice to Appear.
But the Trump admin mandates detention. So a man is dead.


ICE arrested a 56-year old green card holder, i.e. a lawful permanent resident, and detained him in the Rio Grande Processing Center, where he died. texastribune.org/2026/10/19/…

🕊 retweeted

[8/n] By the way, for the simulation folks wondering how we simulated tight-clearance parts: the usual tools didn't work for us. SDF was so slow and hard to tune. Off-the-shelf convex decomposition like V-HACD or CoACD filled the clearance, so parts that should fit jam.
So we built mjfit. It decomposes common assembly parts (pegs and holes of any outline, threads, and gears) into convex pieces that keep the clearance exactly as designed, and it runs an order of magnitude faster than SDF.
It's open source: github.com/younghyopark/mjfi…