
Offensive Security Researcher @Intel @STORMTeamIntel. Previously @vu5ec
Amsterdam, The Netherlands
Joined November 2008
- Tweets379
- Following304
- Followers535
- Likes1.3K



Sebastian Österlund retweeted

BTW I still keep updating the VMX capabilities table at pulsedbg.com/vmx.html
Check out new features for Panther Lake CPUs.
Sebastian Österlund retweeted

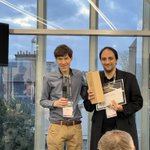
At Linux Security Summit Europe in Amsterdam.
Current talk is on FineIBT Enhanced, with Scott Constable & @sirmc
lsseu2025.sched.com/event/25…
Follow event info here: social.kernel.org/LinuxSecSu…
#linuxsecuritysummit

ALT Peter Zijlsrtra, Sebastian Österlund, Scott Constable.


Sebastian Österlund retweeted
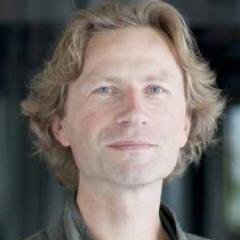
Happy to report that our InSpectreGadget paper won a Distinguished Paper award at @USENIXSecurity:
download.vusec.net/papers/in…
@vu5ec @SanWieb @HBitmasks @c_giuffrida
Here is @SanWieb presenting the paper:

Sebastian Österlund retweeted

🚀 kAFL release v0.9 !
✨kernel upgraded from 6.0 ➡️ 6.8 (fixes compatibility issues with last gen CPUs)
github.com/IntelLabs/kAFL/re…
Sebastian Österlund retweeted

This took a significant amount of time and money, and now we know what DRAM vendors are doing in their sense amplifiers! Lots of research opportunities moving forward. All the images and the reverse engineered circuits are now publicly available.

For the first time, we imaged and reverse engineered 6 modern DDR4/5 DRAM chips (comsec.ethz.ch/hifi-dram)
Due to the incredibly small feature size of modern ICs, we use SEM combined with FIB reaching pixel resolutions as low as 3.4nm. Then we evaluate 10 years of DRAM research.
Sebastian Österlund retweeted

Interested in low-level hacking, embedded systems, and trusted execution environments? We currently have a PhD opening, feel free to reach out for more information! Application deadline: April 1st 2024.
Sebastian Österlund retweeted
We have open PhD/PostDoc positions in the COMSEC group at ETH. If you want to build the next high-profile hardware attack, come up with new analysis techniques, or work on strong software/hardware mitigations at the OS/compiler/HDL level, you should apply! comsec.ethz.ch/join
Sebastian Österlund retweeted

Emulated full system snapshot fuzzing by Intel 👀
haunted.computer/@novafacing…
Sebastian Österlund retweeted

A year ago I made a video about the RIDL CPU vulnerability. In case you haven't seen it, here it is uploaded to Twitter directly!
The most interesting part of this has been learning about the prior research that later lead to the discovery of these modern side-channel vulnerabilities.
I also spend more time explaining "speculative execution" and how these CPU cache timings can be used as a side-channel.
If you haven't seen it yet, give it another chance :)
Sebastian Österlund retweeted
Our Quarantine @RAID_Conference paper is online! Quarantine enforces strict CPU core-based isolation to mitigate transient execution attacks vs. cloud VMs. Joint work by Mathé Hertogh @manuwiesinger @sirmc @nSinusR Nadav Amit @herbertbos @c_giuffrida: download.vusec.net/papers/qu…
Sebastian Österlund retweeted
Our uncontained paper @USENIXSecurity is online! Find out how the Linux kernel is the "container of" several type confusion bugs, detected by our sanitizer & static analyzer. Joint work by @JakobKoschel @borrello_pietro @dcdelia @herbertbos @c_giuffrida: vusec.net/projects/uncontain…
Let’s see how long it takes until they start playing a loop of Swan Lake on TV…
youtu.be/Xd2nTXsivHs
Sebastian Österlund retweeted
🚀 RELEASE: kAFL v0.6
➡️ 6.0 kernel
➡️ new repo: IntelLabs/kafl.actions: github.com/IntelLabs/kafl.ac…
What if you could integrate kAFL in your favorite Github Action pipeline ?
Now you can ! ✨
Sebastian Österlund retweeted
📢 We are hiring! If you are into the security of low-level things such as kernels, compilers, hardware designs and like to do your PhD in ETH's top-notch environment, you should definitely consider applying! #PhD #Security #HDL #RISCV #Rowhammer #Spectre jobs.ethz.ch/job/view/JOPG_e…
Sebastian Österlund retweeted
Disclosing CHOP, aka how attackers can bypass commodity return address protections such as stack cookies by hijacking the exception handling process. Paper to appear @NDSSSymposium: download.vusec.net/papers/ch…. Joint work by @victor_duta Fabian Freyer @pagabuc @nSinusR @c_giuffrida
Sebastian Österlund retweeted

LibAFL QEMU full-system mode is a thing! Check out the example that fuzz a small ARM FreeRTOS firmware at github.com/AFLplusplus/LibAF…
Next step: fast memory and devices snapshots
Sebastian Österlund retweeted
How I started chasing speculative type confusion bugs in the kernel and ended up with 'real' ones
@JakobKoschel gave a talk at the @linuxplumbers conference about the tool for discovering speculative type confusion bugs in the Linux kernel.
Video: youtu.be/KkOdMwZRpYY?t=2843
[1/2]
Sebastian Österlund retweeted

#tbt to @LiveOverflow's partnership with #ProjectCircuitBreaker on discovering vulnerabilities in Intel CPUs. Check it out here: youtu.be/x_R1DeZxGc0
Sebastian Österlund retweeted
I forgot to tweet out my last video on finding bugs in CPUs 😱
It’s one of my all time favorite videos and I’m very proud of it! A lot of effort went into researching and making the video.
Thanks again @sirmc and @IntelSecurity for making it happen 🥰
youtube.com/watch?v=x_R1DeZx…
Sebastian Österlund retweeted
#ProjectCircuitBreaker x @LiveOverflow? Oh, what a treat! Check out this new video on cutting-edge tips to discovering #vulnerabilities in #Intel CPUs: intel.ly/3zQn7Ej & info on Project Circuit Breaker: intel.ly/3AfQCkh