

DFIR Researcher / Software Developer
Tokyo, Japan
Joined June 2020
- Tweets1.2K
- Following408
- Followers411
- Likes2K





Pinned Tweet
イベントログを見るときの備忘録をまとめています。
君たちはどうWindowsイベントログを調査するか - SIPDEP sumeshi.github.io/posts/know…
#DFIR #CyberSecurity


S.Nakano retweeted

when my wife calls me in an angry voice I have to follow the exact commands that follow. #wife2shell
まぁ今の状況だと個人情報を人質に取られるより、システムのどこが脆弱だったかを事細かに説明されるほうが効くよね。
仮にその手口が根付くとしたら、社会への効果的にはどっちがホワイトハッカーなんだかわからなくなるけど。
S.Nakano retweeted
One other awesome thing...well 2.
Mftecmd now supports full $logfile as well as usnjrnl rollback for historical directory names, etc!
Logfile csv is easy to use and has all the things. Another source for timestomp detection
S.Nakano retweeted
1/ EZ Tools 2026.10 is out, all on .NET 10 (LTS)
✅ More accurate: 331K more event log records, hive logs replayed as Windows does, every test hive loads
⚡ Faster: up to 9x; EvtxECmd and Registry 2x
📉 Less memory: up to 82% less
Update with Get-ZimmermanTools 🧵 #DFIR


S.Nakano retweeted

The six-step IR process has no instruction for the moment your scope breaks. @joswr1ght rebuilt it. The result is Dynamic Incident Response, a book introducing the Dynamic Approach to Incident Response (DAIR) model. Currently $0 on Kindle: amazon.com/dp/B0HK2V88SX

ALT The image features a book titled "Dynamic Incident Response: A Framework for Security Teams" by Joshua Wright, with an endorsement from SANS. Next to the book is a person smiling, framed in a circular cutout. The text highlights the book’s focus on modern incident response, authored by SANS faculty, and promotes that it's free to download, share, and adapt.


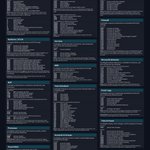
Based on my article, "How Do You Investigate Windows Event Logs?", I put together a reference poster of useful Windows Event IDs for investigations.
Available in English and Japanese.
sumeshi.github.io/archives #dfir


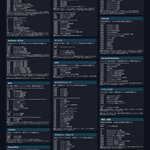
「君たちはどうWindowsイベントログを調査するか」で取り上げたイベントID一覧をポスターにまとめてみました。
sumeshi.github.io/archives


S.Nakano retweeted

macOS起動時からMacに接続されたボリュームの自動マウントをブロックできるようになった「MountMate v6」がリリース。 applech2.com/archives/202610…


