

Hacking is not a miracle. Is knowledge "Co-Fundador" "H&B" Donostia #CGI_Spain |-Cyber Security- | #RedTeam | # https://teapawt.net/t.co/S1YfYsxC0U
Spain
Joined January 2012
- Tweets3.8K
- Following333
- Followers6.8K
- Likes6.3K


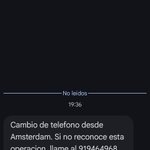

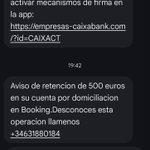


T31m0 retweeted

Ya va siendo hora de ver en la práctica como modifican los malos una cuenta bancaria de un pdf dentro de un correo. Un BEC (Business Email Compromise) en eras modernas.
Motivado por @stroggxp
Música por @t31m0
DEP Raúl Romero
youtu.be/ek1g59hA-Zg
#BeGoodBeHackers

github.com/qkaiser/broadcom-… cuidado que esto es mas peligroso de lo que parece ... y si lo analizas bien ... el impacto ... es la primera version del PoC [privado] que acabo de crear ... pero existe RCE ... solo afinar sona de memoria ... estoy en ello 😅🤣🤣 uuuffff 🤣🤣🤣😅

T31m0 retweeted

GitSpawn: RCE en agentes de coding con IA.
Un .git/config malicioso puede convertirse en ejecución de comandos en agentes como Claude Code, Codex, Cursor o Qwen Code.
Supply chain + AI agents. Mala combinación.
🔗 shattered.io/gitspawn-ai-cod…

T31m0 retweeted
🚨 Next.js: SVG → RCE
CVE-2026-94545 afecta a next/og ImageResponse.
Si valores controlados por el atacante llegan al SVG generado, puede terminar en ejecución de código en el servidor.
Afecta a Next.js 16.2.x → 16.3.5.
🔗 github.com/vercel/next.js/se…

T31m0 retweeted
🪟 Windows 0-day: ALPC → SYSTEM
CVE-2026-85880 es un heap overflow en Windows ALPC que permite elevar privilegios localmente.
Microsoft la corrigió en septiembre y CISA la marca como explotada.
🔗 github.com/advisories/GHSA-9…

T31m0 retweeted

🚨Cyber Alert‼️
🇪🇸Spain - Real Federación Española de Fútbol
The Royal Spanish Football Federation (RFEF) disclosed that its online ticketing platform suffered a temporary outage after its systems were hit by a high volume of malicious external traffic, consistent with a DDoS disruption.
The incident forced the RFEF to temporarily suspend ticket sales while security and business-continuity procedures were activated with its technology providers.
Full details and impact assessment on HackRisk.io

T31m0 retweeted
T-Mobile cortó físicamente los cables de Internet para echar a hackers de su red
T-Mobile cortó físicamente cables con tijeras para expulsar a hackers vinculados a China pertenecientes a la operación Salt Typhoon
blog.elhacker.net/2026/08/t-…

T31m0 retweeted

Today we are disclosing CVE-2026-48558, an auth bypass in #SimpleHelp RMM when OIDC is configured.
Affected servers let unauth attackers create a Technician session - allowing remote control, script exec, monitoring. High-level details and IOCs:
horizon3.ai/attack-research/…

T31m0 retweeted

Tal vez en un aeropuerto de Esñapa, o de otro País, o como lo quieran llamar... pero las protecciones no son suficientes... al menos un MFA? Nos vemos en la @EuskalHack para contar muchas cosas!!! La semana que viene estaremos!!!
T31m0 retweeted
🚨Cyber Alert ‼️
🇪🇸Spain - 𝗪𝗶𝘀𝗲 [𝗦𝗽𝗮𝗶𝗻]
Threat actor "giorggios" claimed to be selling a database allegedly linked to Wise Spain containing 4.9 million user records. The leaked data allegedly includes names, dates of birth, identification numbers, phone numbers, email addresses, location details, and KYC/AML verification information
Threat actor: giorggios
Sector: Financial / Insurance
Data exposure (claimed): 4,900,307 user records
Data type: Personal data, KYC/AML verification information
Observed: Jun 9, 2026
Status: Pending verification
ESIX©: 6.57
Full details and impact assessment on HackRisk.io

T31m0 retweeted

I was fired from Anthropic today.
I was the engineer responsible for shipping the latest dev/claude-code npm package. Wanting to improve the debugging experience for the team, I decided to include source maps in the release. This resulted in our entire internal codebase being publicly exposed including thousands of files with every agent command, all system prompts, the complete query engine, Undercover Mode, Bypass Permissions Mode, and our internal telemetry configuration.
I take full responsibility. I genuinely believed the safeguards Claude Code had built for me would be adequate and it was a serious miscalculation on my part.
My actions have unintentionally open-sourced major parts of Claude’s architecture well ahead of schedule. I apologize to the team and to Claude.

Claude code source code has been leaked via a map file in their npm registry!
Code: pub-aea8527898604c1bbb12468b…

Readers added context they thought people might want to know
This person was never an Anthropic employee.
This is backed by their LinkedIn and op’s own reply promoting their startup, at which they’ve worked for a year.
linkedin.com/in/kevindnaugh…
x.com/kevinnaughtonj…

T31m0 retweeted
Watching live right now "Evilginx MFA Phishing Evolution with Phishlets 2.0" with @mrgretzky at youtube.com/watch?v=eeauoOYU…


T31m0 retweeted

‼️🇪🇸 A post on a popular cybercrime forum is selling Spanish IBAN banking data containing 14 million records.
▪️ Records: 14 million
▪️ Data Fields: DNI, date of birth, first name, surname 1, surname 2, phone, IBAN, bank code, bank name

T31m0 retweeted
Acabo de subir mi charla de @rootedcon sobre las Balizas V16 con los primeros scripts a mi web personal en s4ur0n.com (sección charlas). Próximamente iré subiendo más cosas y scripts para que podáis jugar con su Hardware...

