
Symantec and Carbon Black's threat hunters bring you the latest threat intelligence from the IT security world.
Joined July 2009
- Tweets16.5K
- Following365
- Followers115K
- Likes248




Threat Intelligence retweeted

I want to post our analysis first on X (later on our website) on the Fast 16 malware that was done in parallel to analysis by @KimZetter and @symantec
“Fast 16 Malware Aimed at Undermining Proliferant State Nuclear Weapons Programs, Iran was a Credible Target” by the Institute for Science and International Security
Highly interesting analysis that Kim Zetter and the Symantec’s Threat Hunter Team were able to develop after Sentinel One publicly revealed the Fast16 malware, which is dated to about 2005 and was a multi-year sustained operation. The malware looks to be targeting a nuclear weapon program’s hydrodynamic calculation group working on implosion systems using weapon-grade uranium as the nuclear explosive material.
Fast 16 targets the LS DYNA and AUTODYN software and specifically manipulates the values during simulations of explosively driven compressions of very dense materials. These software packages are very useful and capable to model the whole hydrodynamic process starting with the detonation of the high explosives, the development of a shock wave accelerating a high density metal flyer plate that strikes the core with tremendous force, causing compression of a central dense core to very high pressures and temperatures, exactly the hydrodynamic process in an implosion-type, solid core, levitated design, common to many early nuclear weapons programs. The software packages enable the solution and characterization of a very difficult problem involving full transient physics of matter under extreme compression. It turns an extremely fast, and opaque physical process into a fully resolved, designable system, with an exact geometry, driver, and timing that produces the pressure, density, and uniformity desired.
Although the malware looks first for specific high explosive equation of state (EOS) packages in either LS DYNA or AUTODYN, that seems just to be a first step in locating a worthwhile target, or a way to narrow its search. The ultimate target is a material being compressed that is far denser than the high explosive materials and far denser than the metals commonly studied in commercial applications of LS DYNA and AUTODYN.
The target metal appears to be uranium. The software lists a value of 19, where 19 g/cc is the density of solid uranium at atmospheric pressure. The manipulation of the simulation output was to start when the density of the compressed material would reach 30, which again indicates uranium. The density of 30 g/cc is the point at which the lattice structure of solid uranium is soon to collapse, and the material starts to liquify under shock. A density of 30 g/cc is further assessed to be a compression within reach of an early nuclear implosion weapons program. This indicates that a core of uranium is the target and shows the malware starting to act in a particularly important region where the uranium is starting to undergo a phase change from solid to liquid. This region is particularly important to a nuclear weapons team that wants to understand how to increase the uranium’s density, and ultimately help achieve a higher explosive yield, but also a region that is very difficult to study experimentally. The accuracy of predicted pressures, densities, and phase states becomes increasingly uncertain at high compression because of limitations in available uranium equation-of-state data and the complexity of its phase behavior, leaving the designer more dependent on the model rather than experimental data.
Target Iran?
While we cannot exclude other target countries working on nuclear weapons in the early 2000s, such as North Korea or possibly Syria, the timing, the access required for creating the faulty driver memory, and the focus on uranium point to Iran’s nuclear weapons efforts being the target. It is also known from a variety of academic publications that both LS DYNA and AUTODYN were being used in Iran in this time period.
In the period of 2003 to 2005, Western intelligence agencies believed that Iran had an active nuclear weapons program concentrated on building warheads for ballistic missile delivery, with active calculation and simulation teams modeling the nuclear explosion. Although Western intelligence was unaware in 2005 that Iran had ended the program, codenamed the Amad Plan, dedicated to building five nuclear weapons as fast as possible, Iran instituted a new nuclear weapons program on a reduced scale which was likely more dependent on computer calculations and simulations. In either case, malware targeting the results of these complex calculations characterizing a region of high pressure and density posed a serious threat to the program.
Despite missing Amad’s shutdown, Western intelligence in 2005 had penetrated Iran’s nuclear weapons program in multiple ways, and within a few years afterwards learned that the Amad Plan had shut down. The penetration could have been sufficient that someone could have inserted the malware into the internal computer networks used by the nuclear weapons teams, a requirement since the malware does not transit via the internet.
Iran’s nuclear weapons program in 2003, at the end of Amad, was suffering problems in its nuclear weapons design. The 2018 seizure by Israel of the Nuclear Archive, a detailed library of the Amad Plan, contains discussions about the state of the nuclear weapons effort as of late 2003. In summing up the challenges that remained when the Amad Plan was ending, the leaders of the program met and noted difficulties in the design section, defined as calculations and analysis, production, and test. They cited the lack of scientific knowledge of design, where the main problem is the reduction in the scientific studies of the project. The head of the program concluded that the design team had to specify a set of questions so that these questions become the instructions for other teams such as production and test. These problems likely persisted into the time when the malware was active, and the reorganized nuclear weapons team was running computer codes.
One further indication of Iran’s on-going multi-year efforts to conduct satisfactory hydrodynamic simulations is that the IAEA reported that Iran in 2008 and 2009 was modeling spherical geometries consisting of a weapon-grade uranium core subject to shock compression.
If Iran was the target, Iran’s nuclear weapons program would have had a hard time doubling the core density in 2005, likely also today. Achieving such high densities in uranium poses several challenges in a single HE-flyer plate-solid core system. Moreover, in 2003, Iran was looking to achieve only an explosive yield of 10 kilotons, further suggesting that the nuclear weapons team was not working to achieve such high densities. This would suggest that the actual densities being achieved were less than double and closer to 31 or 33 grams per cc, close to the activation density of the malware and after the solid would undergo a phase change to a liquid.
Action of the Malware
The Symantec threat hunter team identified multiple mechanisms, called by them as A, B, and C, in the malware sample that was detected and analyzed. Mechanism A was judged as naive and not further assessed. B appears to target LS DYNA, and C targets AUTODYN.
Beyond the malware authors’ apparent confidence in the worthiness of the effort, thus far, it is not possible to fully establish the malware’s impact on a nuclear weapons program. Simply put, both mechanisms B and C manipulated Equation of State results for the compressed weapon-grade uranium, or its stand-in natural uranium, metal, and specifically lowered the calculated pressure experienced by the uranium by a factor determined by the actual pressure being calculated by the EOS program.
If this or these values are lowered too much, the inconsistencies in the resulting physics should be noticeable or discoverable by the user. But if the change is less, lowering the results artificially, it may not be noticed by the user of the software. If pressure is the output value lowered, the manipulated results would indicate to the user that the uranium is “softer” and more easily compressed than it is in reality. However, it would also indicate the shock wave propagating through the material, intended to sustain super criticality throughout the core as well as initiating the neutron source at the center, is weaker than expected and the phase change to melting may appear to onset earlier or later or the dense-fluid region look broader or narrower. The accuracy of predicted pressures, densities, and phase states becomes increasingly uncertain at high compression because of limitations in available uranium equation-of-state data and the complexity of its phase behavior. Thus, a misperceived result of this region may be more believed because of these uncertainties, particularly because of the difficulty of testing experimentally in this density region.
The impact of a malware’s change in the pressure in the region above 30 grams per cc can complicate efforts to improve the design and even send programs down wrong paths. The calculational team may recommend more force on the core or more efficient transfer of force to increase the compression. This may put pressure on manufacturing teams to make and test new components to enable these changes. This could complicate miniaturization efforts, a critical concern to ensure the warhead fits into a ballistic missile re-entry vehicle. The effect could be to waste time, resources, and lower the overall morale of the program. If “fixes” are made and the program runs again, unsatisfactory values will be generated anew.
If the results are accepted as valid and no further work is done, then the nuclear weapons program ends with a mistaken view of the performance of the imploding core, leading to potential distortions when the code is combined with neutronic codes. The sum total may result in a system that will not work, or will underperform, when detonated.
Thus, the results would undermine confidence in the overall workability of a simulated design, and if the scaling in the pressure went unnoticed, could potentially lead to structural design changes in the components of the weapon to rectify the perceived problems. In any case, the malware appears intended to disrupt the development and construction of a nuclear weapon.
Threat Intelligence retweeted
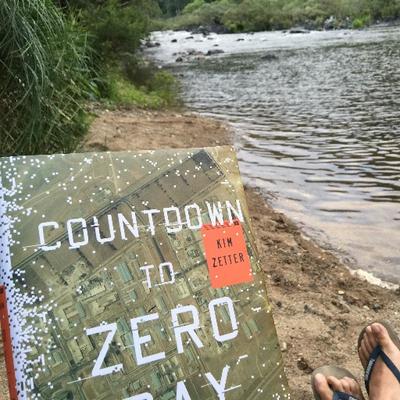
Exclusive: Fast16 malware has raised questions about what it was designed to do. Researchers at @symantec finally confirm that it was subverting software used to simulate nuclear weapons explosions. Nuclear experts tell me Iran was the likely target zetter-zeroday.com/experts-c…

Threat Intelligence retweeted

Review the latest information on Daxin #Malware #APT activity against governments and other critical infrastructure targets from @CISAgov and @threatintel. go.usa.gov/xzgre #Cybersecurity #InfoSec
Threat Intelligence retweeted
Breaking. #ESETResearch discovered a new data wiper malware used in Ukraine today. ESET telemetry shows that it was installed on hundreds of machines in the country. This follows the DDoS attacks against several Ukrainian websites earlier today 1/n
Threat Intelligence retweeted
Read our blog on Apache Log4j Zero-Day.
Symantec products will protect against attempted exploits of critical CVE-2021-44228 vulnerability. symantec-enterprise-blogs.se… #Log4Shell
Threat Intelligence retweeted
Think you know what happened in the Bangladesh Bank heist? Think again. Get the inside scoop from our own Eric Chien on Episode 4 of @BBCWorld's #podcast "The Lazarus Heist" Listen now 👇 bbc.in/3bhC7PR #LazarusHeist
Threat Intelligence retweeted

Outstanding #germany 10 points !!! - deputy inspector of the #German cyber command #CIRBw and chief information officer #CISObw of the German armed forces #bundeswehr, general major Jürgen Setzer, released #vulnerability #disclosure #policy bit.ly/3ojwNAm

Liebe #IT-SicherheitsforscherInnen!
#CISOBw ruft dazu auf, die #Bundeswehr ab sofort aktiv auf Schwachstellen in ihren #IT-Systemen auszutesten & hinzuweisen 😱. Ja, Sie lesen richtig - wir haben jetzt eine #Vulnerability #Disclosure #Policy. Kleine Challenge?
#DuFuerDeutschland
Threat Intelligence retweeted

Thanks to the team at Symantec @threatintel for sharing this report on Sodinokibi ransomware with @CyberAlliance members early! A great blog on recent incidents where actors scanned for PoS software, probably looking for more ways to make $$$. #EmpoweringCTA

#Sodinokibi -#Ransomware Attackers also Scanning for PoS Software, Leveraging Cobalt Strike. Read more: bit.ly/2VoiWfB #REvil #infosec

Threat Intelligence retweeted
Use the force Luke - #NIST drafts #Ransomware #Detection and #Responds Guides bit.ly/3bnxHFA – call for comments extended to 20th of march @threatintel @teamcymru #cybercrime #infosec

Threat Intelligence retweeted

The FBI’s #ThinkBeforeYouPost campaign is designed to help schools & parents educate students before they make a poor choice that could impact them for years . Learn more about building a digital defense against hoax threats in this week's #TechTuesday flashalert.net/id/FBIOregon/…

Threat Intelligence retweeted
Does privacy even exist anymore? Here, we take a look at the privacy considerations of the smart home and beyond: iotworldtoday.com/2019/09/03…

Threat Intelligence retweeted
Ever played with the greatest team in the world – WE @symantec are a proud part of the german blue team bit.do/bt11 @bundeswehrInfo @Fraunhofer_FKIE @BSI_Bund @BWI_IT @Siemens in #LockedShields 19 the biggest cyber defense exercise on this planet operated by @ccdcoe
Threat Intelligence retweeted

In the new threat landscape, living off the land and supply chain attacks are a staple in attackers’ arsenal. Learn what this means for your organization during tomorrow’s Internet Security Threat Report (ISTR) webinar. Register now: symc.ly/2YvsGnR

Threat Intelligence retweeted
Thanks to @orlacox and the @symantec team for sharing this research with @CyberAlliance members early!
Check out our latest research on the Elfin espionage group (aka #APT33). They've been highly active of late, attacking at least 50 different orgs in the past three years. symc.ly/2TDK5wc #Elfin

Threat Intelligence retweeted
Ransomware shows early signs of decline, but new stealthier attack methods are emerging in its place. Our 3/28 webinar walks you through our latest Internet Security Threat Report 2019 #ISTR. Register now >> symc.ly/2Ye0I07

Threat Intelligence retweeted
Cyber criminals have a new favorite attack method: formjacking. @FortuneMagazine has the details about this year's #ISTR. symc.ly/2Xk104K
Threat Intelligence retweeted

Formjacking Surpasses Ransomware and Cryptojacking as Top Threat of 2018 - by @serghei
bleepingcomputer.com/news/se…

Threat Intelligence retweeted
Cyber-thieves set sights on hijacking payment data bbc.in/2DU9yqq

Threat Intelligence retweeted
It’s finally here. The biggest threats you may (or may not) have seen coming. Get a glimpse into this year’s #ISTR. symc.ly/2XeEMkH
Threat Intelligence retweeted
Here are the #cybersecurity trends and activities most likely to affect organizations, governments and individuals in 2019 and beyond. symc.ly/2RjSvUd