

Vital Digital Forensics: Cyber-security services, specializing in Digital Forensics / Incident Response (DFIR), malware analysis and expert witness testimony
Athens
Joined October 2021
- Tweets1.2K
- Following60
- Followers228
- Likes35




Pinned Tweet
2022 #phishing #insights report published today by @v4ensics. Phishing campaigns, Greek wise, targeted the #HellenicPostService (ELTA), #NationalBankGr and #AlphaBank, while global wise, postal and #Meta targeting scams were on the rise. Read the report on v4ensics.gr/phishing/

A lot of campaigns targeting #OptimaBank seen the last three weeks.The last one uses an @awscloud site (jaid1bualitzla[.]s3[.]ap-south-1[.]amazonaws[.]com/so140) to direct victims to scanned[.]page/p/3ZQVBj and lastly to s1267149[.]ha009[.]t[.]mydomain[.]zone/optima/DUVzTTavlOw/?


#phishing campaign targeting #Eurobank just spotted.
Fraudulent messages containing #URLShortened links (t[.]co/IPh8nq2Ndr) aiming to steal login creds and device info.Victims redirected to ebanking-eurobank[.]net/auth/login[.]php
#Cybersecurity #ScamAlert #Stayvigilant


#phishing site's root folder reveals a #Wordpress site! If victim's credentials are submitted, they are processed by Assets/php/config/func.php. Site tracks victim's IP through update_status.php?ip=, while a txt file named {IP}.txt is created in auth/victims/{IP}.txt


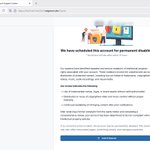
As @Meta #phishers continue their activity four years now, @appsheet is now their tool of choice for mail sending, while their sites are hosted in .dev TLDs. Occasionally @EmailJS_com is still being used. Latest seen site is frail-red-5zw7oii4[.]edgeone[.]dev/home


Both phishing sites seem to be subdomains of legitimate commercial sites (theoutwrld[.]com and flybus-travel[.]com) and , irrelevant obviously to the supposed recruiters brands (#Asos and #Airbus). Based on OSINT (kudos @urlscanio ) campaign is active the least 16 days


New #IPaddress (193.46.217.13) hosting malicious sites. IP uncovered through e-mail campaigns mimicking @bookingcom and hosts multiple #FakeCaptcha sites


New #phishing campaign targeting #eltacourier (elta[.]courier-ls[.]sale/gr) just spotted in the wild


As #Greekcitizens submit their tax statements #phishers try to trick them that #taxrefund is communing. Relevant phishing site is https://syndesiapp[.]web[.]app/main


4 Greek banks available for the alleged #taxrefund (@NationalBankGR , #AlphaBank, #Eurobank and #PiraeusBank


v4ensics retweeted
🚨Ransomware actors exploited an unpatched vulnerability (CVE-2024-57727) in SimpleHelp RMM to compromise a utility billing software provider—part of a pattern of actors targeting downstream customers. See our advisory for mitigations👉go.dhs.gov/wKc


With #phishers playing again the familiar to @v4ensics @Meta #policyviolation scheme accompanied with the "short"/24h #accountterminationnotice phishers sent the e-mails that triggered the investigation from @gmail accounts and targeted #German speaking users
