

Pentester | MD (Intensivist & Healthcare Simulation in another life) | Infosec, Geopolitics, Defense, Hybrid warfare, DCS, Gaming, Metal Opinions are my own
(OU=FR,DC=EUROPE,DC=WORLD)
Joined July 2008
- Tweets30.2K
- Following6.1K
- Followers1.7K
- Likes6.2K


💻🥷 WarthogTK 🩺 retweeted

📘Le rapport d'information portant recueil d’auditions de la commission sur la guerre hybride et continuum de conflictualités est en ligne 👉assemblee-nationale.fr/dyn/1…. #DirectAN #Defense

💻🥷 WarthogTK 🩺 retweeted

hashcat v8.0.0 released!
The largest update in the history of hashcat, with PCFG attacks, hash recipes that crack hashes without a hash-mode, and bcrypt on FPGA boards.
Release notes: github.com/hashcat/hashcat/b…
Download: hashcat.net/hashcat/

💻🥷 WarthogTK 🩺 retweeted

‼️ Researcher Erica Windisch skipped coordinated vulnerability disclosure and published 11 unpatched Tailscale flaws.
In her lab, Tailscale SSH race conditions let one hacked device get root on other servers and add a rogue node.


Readers added context they thought people might want to know
The Tailscale SSH findings require prior authorized access on the tailnet per the researcher's report; Tailscale stated issues concern post-authorization behavior only and did not recommend disabling SSH for everyone.
tailworm.com
x.com/IntCyberDigest…
💻🥷 WarthogTK 🩺 retweeted

Syswhispers4
github.com/JoasASantos/SysWh…

💻🥷 WarthogTK 🩺 retweeted

Un créateur de haine , dans un magasin de haine.
La forme et le fond.
C’est pas venu tout seul.
L’un fait du fric l’autre fait des voix …
Les conséquences , ils s’en lavent les mains…

💻🥷 WarthogTK 🩺 retweeted

🔴 Fusillade de Trappes : "J'espère qu'on sera capable de voir les plus grandes autorités de ce pays défiler ensemble", appelle Ali Rabeh, maire (Génération.s) de Trappes. Il espère "réunir des élus qui sont capables de dire que le Ggrand remplacement n'existe pas."
#canal16
💻🥷 WarthogTK 🩺 retweeted

You do not need an RF jammer or a cyber exploit to knock a drone out of the sky. In 2015, security researchers proved that playing an 8.2 kHz sound wave at an unprotected flight controller forces it to drop instantaneously.
This is an acoustic resonance attack, and it exploits a mechanical vulnerability in the micro-electro-mechanical systems (MEMS) inside consumer gyroscopes and hard drives.
1. The anatomy of a vibrating silicon spring
Inside a drone's flight controller sits an Inertial Measurement Unit (IMU). The core of that IMU is a MEMS gyroscope measuring less than four millimeters across.
Inside the chip, a microscopic silicon proof mass is suspended above a substrate by silicon micro-springs. The internal drive circuit vibrates this mass back and forth at a known drive frequency.
When the drone rotates along its pitch, roll, or yaw axis, the Coriolis force deflects the proof mass toward fixed capacitive comb fingers.
The deflection shifts the electrical capacitance by fractions of a femtofarad. The chip's analog front-end converts this capacitance change into voltage, feeds it through an Analog-to-Digital Converter (ADC), and passes raw angular rates to the flight controller over SPI or I2C.
2. The 8.2 kHz acoustic exploit
Every physical structure suspended on micro-springs has a mechanical resonant frequency.
In a 2015 USENIX Security study, researchers tested 15 commercial MEMS gyroscopes. Seven were vulnerable to acoustic resonance. Gyroscopes from STMicroelectronics (like the L3G4200D) resonated in the audible band between 2.5 kHz and 8.2 kHz along their X and Y sensing axes.
When airborne sound matches that mechanical resonant frequency, the acoustic energy transfers directly into the silicon lattice.
The proof mass vibrates with severe physical amplitude. The sensing comb fingers saturate the ADC to its maximum railing limits, feeding false angular rates into the flight controller.
3. Why the drone drops
The drone's flight controller runs a proportional-integral-derivative (PID) loop at 500 Hz to 1,000 Hz to maintain level flight.
When sound noise at 8.2 kHz hit the gyroscope, the sensor reported massive erratic rotation spikes. The PID control loop immediately tried to counteract rotation that did not exist.
In real-world flight trials, the controller responded by throttling motors to their minimum and maximum limits simultaneously. The drone lost balance and dropped to the ground instantaneously on all 20 test flights.
4. The same physics in the datacenter
In 2018, researchers at Michigan and Zhejiang demonstrated the same physical failure mode on enterprise hard disk drives.
In a mechanical hard drive, the read/write head floats on an air bearing less than 10 nanometers above spinning magnetic platters, with track widths narrower than 75 nanometers.
Playing an audible 5.0 kHz tone at 115.3 dB SPL caused tracking errors on Western Digital drives. Pumping that tone to 117.2 dB SPL forced off-track vibrations so severe that the drive firmware halted all write operations to prevent physical head crashes on the platters.
With sustained acoustic noise, operating systems experienced complete I/O timeouts, remounting ext4 file systems as read-only.
5. The physical constraints and modern defenses
Acoustic attacks have clear physical limitations:
* Inverse square law: In the drone flight trials, researchers attached a small speaker 10 cm directly above the flight controller at 113 dB SPL. Projecting that sound pressure over 30 meters would require a 140 dB directional acoustic device (LRAD).
* Axis isolation: Modern InvenSense gyroscopes resonate in the ultrasonic range (above 26 kHz) along the Z-axis only, which flight software easily counteracts by cross-checking magnetometer yaw data.
* Mechanical dampening: Wrapping the IMU in dense silicone grommets or acoustic foam blocks airborne sound pressure before it hits the silicon package.
* Asymmetric dual-IMU fusion: Pairing two gyroscopes with mismatched mechanical resonant frequencies (such as 8 kHz and 26 kHz) allows flight software to identify and drop the saturated outlier.
Software algorithms cannot filter a corrupted sensor measurement if the silicon spring itself is physically vibrating.
💻🥷 WarthogTK 🩺 retweeted
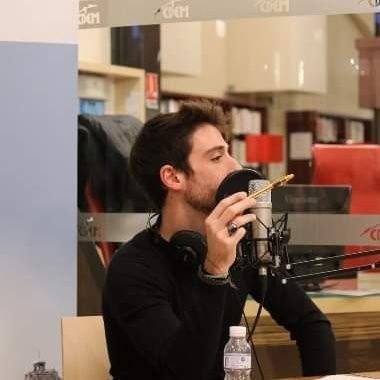
On ne va pas se mentir, même pour un podcast d’histoire de la guerre, on a déjà traité des sujets plus fun.
Mais c’est une question tellement centrale et pivotale (et par ailleurs tellement discutée), que ça valait bien une émission et quelques interrogations méthodologiques.

Pour ce nouvel épisode du Fil de l'épée avec @andreloez, #LeCollimateur plonge dans les violences de guerre et les meurtres de masse du XXe siècle avec Nicolas Mariot (@CNRS), auteur de "Tuer. Comment expliquer les violences de masse".
lerubicon.org/collimateur-23…

💻🥷 WarthogTK 🩺 retweeted

⚠️ Python packages are vulnerable to remote code execution via the same node2shell CVE-2026-111497.
You may be affected if you are using the Brotli library. Note this is a very popular dependency (⬇️100m/month)
Other major services likely affected. We will communicate ASAP when we are able to.
Aikido detects this. Patches available.

💻🥷 WarthogTK 🩺 retweeted
Network edge devices can give threat actors a direct path into an organization.
In a campaign linked to threat actor #k0t, Group-IB and NyxLab observed large-scale targeting of internet-facing FortiGate, FortiWeb, and Palo Alto GlobalProtect systems, with more than 70,000 exposed credentials and related data identified.
The operators combined vulnerability exploitation and brute force activity to gain initial access, then moved deeper into victim environments using tools such as NetExec, Mimikatz, and Impacket, while MeshCentral and AdaptixC2 provided persistence and command-and-control. The investigation also observed data exfiltration through Rclone to Wasabi S3 and MEGA.
Overlaps with organizations later listed by #ransomware groups including #Qilin and #TheGentlemen raise the possibility that the operators may be acting as Initial Access Brokers, although the relationship remains unconfirmed.
Read the full technical analysis: link.group-ib.com/4yDaMQY

💻🥷 WarthogTK 🩺 retweeted

1/2
LDAP signing was supposed to stop NTLM relay to LDAP. I found a way to relay coerced SMB auth to a DC with LDAP signing and channel binding enforced.
Patched in October.
Blog: specterops.io/blog/2026/10/2…
PoC: github.com/grayhatkiller/swi…

💻🥷 WarthogTK 🩺 retweeted
Pendant 8 minutes je répond aux questions @ETopona au sujet des combats entre l’EI et le JNIM, leur impact sur les pays du Sahel et l’erreur de croire que ces combats joueront en faveur des militaires au pouvoir dans les 3 pays dw.com/fr/zone-des-trois-fro…

💻🥷 WarthogTK 🩺 retweeted

‼️ALERT - Two new unpatched CVSS 9.0 RCE flaws in #Linux's KSMBD SMB server were disclosed on public kernel mailing lists before fixes were ready.
One can be triggered WITHOUT authentication.
Neither has a mainline kernel fix.
Details here ↓ thehackernews.com/2026/10/tw…

💻🥷 WarthogTK 🩺 retweeted

🚨 UPDATE: A public PoC demonstrates RCE on PHP 8.5.12, even after the October 21 security patches.
The attack is separate from the patched php2shell CVEs and requires specific session configurations and application weaknesses.
Our earlier concerns about PHP session handling remain relevant.
We've updated php2shell-protection with additional hardening guidance.
#php #cybercurity
github.com/syhunt/php2shell-…

💻🥷 WarthogTK 🩺 retweeted

Sorry everyone... We're announcing a 0-Day vuln in QUIC that allows anyone to remotely turn off a server running these libraries. I swear we didn't plan this.
foxio.io/blog/header-accordi…

💻🥷 WarthogTK 🩺 retweeted

Great tool for hardening your Active Directory automatically, based on solid references like the CIS Benchmark.
I'd recommend using it to audit your own AD, provided you have internal authorization to do so.
It detects misconfigurations and suggests how to remediate them, so cool!
hardenad.net/


How do I harden Active Directory? Look no further...
github.com/LoicVeirman/Harde…
Version 2.9.9 was released last year. There's no excuse 💪


💻🥷 WarthogTK 🩺 retweeted
🚨 PHP2Shell detection is now available in Burp Suite Professional & Burp Suite DAST.
Most of the web is powered by PHP, which means most of the web is vulnerable to these critical unauthenticated remote code execution flaws (CVE-2026-109618 / 109619). You can already detect it in Burp Suite using:
🟧 ActiveScan++ v2.0.13 (portswigger.net/bappstore/31…)
🟧 Bambda scan checks (github.com/PortSwigger/bambd…)
🟧 BChecks (github.com/PortSwigger/bchec…)
Start scanning for the vulnerability now → portswigger.net/bappstore/31…

💻🥷 WarthogTK 🩺 retweeted

🔴 INFO LES JOURS. Nous avons obtenu l’enregistrement de Charles Alloncle lors d’une conférence du 15 septembre dernier. Sous couvert d’humour, il a multiplié les remarques racistes, les blagues grivoises, et dit avoir voulu régler ses comptes avec Nagui.
lesjours.fr/obsessions/rn-de…


💻🥷 WarthogTK 🩺 retweeted
Windows 11 26H2 ships 32 new GPO with AI & MCP controls but the big one for me is about NTLM.
👉🏻 "NTLM Enhanced Blocking" GPO (System\NTLM) block NTLM by account type, device role or app type, with a shared allow-list. 4 rules, each set to Audit / Enabled / Disabled.
From the Oct 2026 security update, Windows 11 (26H2/25H2/24H2) + Server 2025 restrict NTLMv1-derived SSO credentials by default. Watch Event ID 4024 (audit) and 4025 (blocked) in Microsoft-Windows-NTLM/Operational.
📄 Microsoft ref: microsoft.com/en-us/download…