

Software Engineer building sports apps and prediction market agents sometimes. some previous work: @myriadmarkets | @3landersnft #CarolinaCulture #keeppounding
Joined February 2009
- Tweets4.1K
- Following963
- Followers2.1K
- Likes47.2K





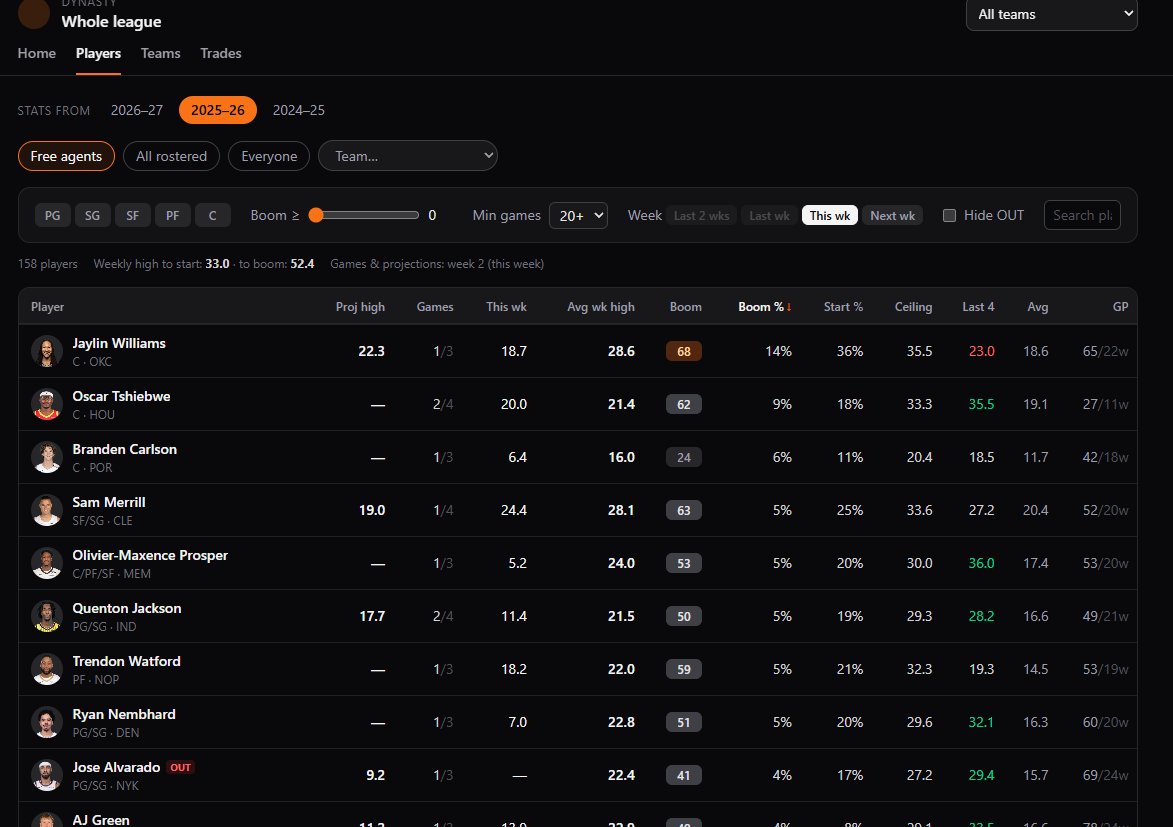
This week I built an app for my dynasty basketball league on @SleeperHQ, built around our Lock-In style scoring, since the Sleeper app is more geared towards total and avg points.
Since we only lock one game per player each week, how you evaluate players is completely different. So everything here focuses on avg weekly highs, “boom” potential, and how often a player gives you a lockable week.
Was fun to build, and shoutout Sleeper for the easy to use api. My league is enjoying this tool
When evaluating free agents, I found it quite difficult to use the Sleeper app to filter based on our league's scoring needs. I don't care about total points or average points, but more so how often they "boom" or have lockable games. So I have weekly highs, avg wk high, etc


I dislike the boring gray that the Canes seem to like so much. Bring me the @CheckersHockey retros


Canes Fans,
@The_JerseyNerds is saying this is the Canes Hometown Remix jerseys with 'near certainty'.
If this is the look, what grade are you giving it?
#CarolinaCulture

Was a bit shocked to see my Foursquare contact number show up when I booked a hotel on Booking . Com.
Forgot about that goated app. It was such a cool experience having all these businesses hooked in, giving discounts for checking in. My favorite dive bar gave free shots out for like every 5th check in lol, an amazing deal for a college student at the time.
Anyways, then I see this post about Foursquare’s final ending, and it’s a bit sad to read.


Foursquare was acquired last month. The outcome was disappointing. It's taken me a while to write this, but I think I'm finally done grieving it. Here are some thoughts on our final years, an effort to honor the team who helped build & maintain FSQ's legacy, and my attempt to finally get some closure. teendrama.substack.com/p/som…

yonder retweeted

Railway is compromised, rotate all API keys as soon as possible
Deployments are down so don’t wait to redeploy
Attackers are draining keys in real time, we didn’t lose much but can confirm this is still an active attack
Stay safe friends
Stacked af day for sports this afternoon
Charlotte 49ers going for their first win
WNBA finals
UNC vs Duke
Hurricanes
Charlotte FC
I can barely fit the game notis on my phone lol

Oh my god I love hockey. Wish I got into it sooner (outside of NHL 98 on PC).
Of the four games I watched last night, 3/4 went to OT.
Islanders vs Senators: Shootout!
Sharks vs Predators: Shootout!
Jets vs Blackhawks: OT!
Flyers vs Red Wings: Late game winning goal!
Whew okay here’s tonight’s NHL predictions that my agent made.
Novig filled on all 4 games
Kalshi and polymarket 3
Idk about this one , although my agent is on like a 14+ game winning streak. Will the luck continue??


My sports prediction market agent’s filled bids from last night.
Went 4-0, although per usual the games were super close (missed FG at end of one game, a shootout win in another game, tie game going into final period in another)
Can see here which platforms had bids filled and for what price.

Pivoted from my short list. I’m starting the new Carrie show.


For the past ~10 years, every October I try to watch at least 1-2 horror/halloween movies or episodes of a show per weekend.
This weekend I FINALLY watched:
- Obsession
- Train to Busan
Does anyone have any recommendations for what to watch next?
On my short list: Backrooms, Hokum, 28 years later: bone temple, Crystal Lake (bc I love Linda Cardellini)
yonder retweeted

Attention BAYC Holders: 413 of you, and roughly ~1000 apes are at risk (10% of the supply) and have approvals open to a Blur contract. With only 2.6% of the collection listed, the majority of these are certainly old approvals.
Once you've revoked your BAYC containing wallet to it, let us know! Oh, and do us a favor and put it in a wallet address you don't use for frequent (or any) transactions!
Other collections have similar ratios, so please don't wait!

Last month, the contracts powering Magic Eden were exploited to the tune of millions of dollars. I was lucky enough to be in a position to rescue a good portion of that, but it highlighted the danger of leaving approvals open as adversaries get access to better and better tools for finding holes in contract logic.
Today, Blur announced that they will be deprecating their frontend.
I've investigated Blur and found no exploits within the current contracts. However, the Blur contracts are upgradable, meaning that they could turn malicious at any time.
They currently have eight figures worth of NFTs approved to them. The safety of those NFTs effectively hinges on the opssec of the Blur team, which appears to be disbanding at this time.
If you have open approvals to Blur, I recommend you remove them immediately. Use revoke.cash or similar to ensure that you are protected in case of a contract exploit or later upgrade.
Don't wait. The time is now.

yonder retweeted

Last month, the contracts powering Magic Eden were exploited to the tune of millions of dollars. I was lucky enough to be in a position to rescue a good portion of that, but it highlighted the danger of leaving approvals open as adversaries get access to better and better tools for finding holes in contract logic.
Today, Blur announced that they will be deprecating their frontend.
I've investigated Blur and found no exploits within the current contracts. However, the Blur contracts are upgradable, meaning that they could turn malicious at any time.
They currently have eight figures worth of NFTs approved to them. The safety of those NFTs effectively hinges on the opssec of the Blur team, which appears to be disbanding at this time.
If you have open approvals to Blur, I recommend you remove them immediately. Use revoke.cash or similar to ensure that you are protected in case of a contract exploit or later upgrade.
Don't wait. The time is now.

For the past ~10 years, every October I try to watch at least 1-2 horror/halloween movies or episodes of a show per weekend.
This weekend I FINALLY watched:
- Obsession
- Train to Busan
Does anyone have any recommendations for what to watch next?
On my short list: Backrooms, Hokum, 28 years later: bone temple, Crystal Lake (bc I love Linda Cardellini)