

Security researcher & Founder of @yoursaudit
Joined July 2025
- Tweets1.4K
- Following328
- Followers329
- Likes12.2K





Pinned Tweet
discord.gg/hwzqHcm9E We now have Discord channel for yoursAudit You are welcome 😊

Byte | yoursaudit retweeted

🥦 26+ years writing exploits! (Since wu-ftpd)
But failed to build a reliable RCE *blind* exploit for Node.js fetch() Brotli
"Made me the Brotli exploit in 5 hours"
🤖 No
Working exploit chains, mem leaks, and many .md notes.
What I learned:
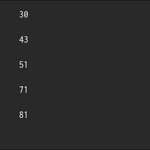
I have currently ranked into overall leaderboard of openkernalchallenge.dev at 30 - 40 😙


Learning fine tuning quantization and more
ai literally open thousands of doors Literally!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!




Who the fuck is burning 1 SOL

The Firedancer bug bounty platform is live at bounty.firedancer.io! Now thru Nov 20th: 2x rewards across the board; 3x for Alpenglow.
We’re sharing our experience running a $1,000,000 bounty contest: how Firedancer’s security model works, notable bugs researchers found, what we learned, and some lessons about triaging AI-assisted reports at scale.
Read it here. jumpcrypto.com/resources/har…


