

Occasionally rt cyber security things & I’m not responsible for your assumption
Selangor, Malaysia
Joined December 2013
- Tweets9.7K
- Following501
- Followers212
- Likes29.5K





Pinned Tweet
Develop some tool in my free time, here's my first one. A simple google dork tool written in golang. Check it out!
github.com/7imbitz/goGO-Dork

adib retweeted

if this PHP vulnerability allows remote code execution, doesn't that mean we can use the vulnerability to auto-patch all vulnerable servers?

adib retweeted

1st blog post since my unemployment arc started. I have a chance to test BoxCompute by @farhanhelmycode and found a cross-tenant security vulnerability issue on it. Reported and fixed swiftly by the developer.
I'm currently open for any freelance job.
rz.my/2026/10/cross-tenant-s…
adib retweeted
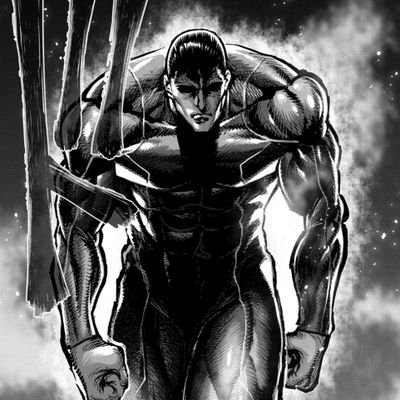
Dude this looks incredible omg, they really matched how the manwha felt to read with this style

The quietest kid in school hits the hardest 🥊
The Boxer is coming soon to Crunchyroll #NYCC
adib retweeted

The guys who made RAM so expensive are singing their hearts out to “Uptown Funk.”
Look how happy they are. 😂
Made on two DGX Sparks using MiniMax H3.


adib retweeted
Can't stop thinking about this:

"Wasting time" might be one of the strangest accusations we've ever invented.
Apparently you can waste 2:00 p.m. by sitting under a tree doing nothing. The afternoon was going to pass either way. The Earth was going to rotate either way. But because you didn't convert those hours into money, errands or improvement, we decided the time itself was wasted. As if simply being alive isn't enough to justify an afternoon.


adib retweeted

A big thank you to 𝗡𝗲𝘁𝗕𝘆𝘁𝗲𝗦𝗲𝗰 for supporting #ParallelPulse2026 as our 𝗕𝗥𝗢𝗡𝗭𝗘 𝗦𝗽𝗼𝗻𝘀𝗼𝗿!
Registration is open until 𝟮𝟰𝘁𝗵 𝗦𝗲𝗽𝘁𝗲𝗺𝗯𝗲𝗿 𝟮𝟬𝟮𝟲, 𝟭𝟮𝗮𝗺.
Tickets here: tickets.nanosec.asia/nanosec…
#NetByteSec #CyberSecurity #NanoSec #SIAGAInformatics


adib retweeted

sure can!! sorry for the late reply, I uploaded it here: speakerdeck.com/lilacj4de/mc…

adib retweeted
Anatomy of a macOS ClickFix Crimekit that Weaponises EtherHiding
notes.netbytesec.com/2026/08…
adib retweeted

Found a heap overflow vulnerability in Windows SMB that leads to RCE and reported it to MSRC in June.
The vulnerability has now been addressed with CVE-2026-62800 in the August Patch Tuesday updates.
msrc.microsoft.com/update-gu…


adib retweeted

CertiGhost (CVE-2026-54121) deserves much more attention than it is getting right now, from my point of view.
In a common/default AD CS setup, a low-privileged domain user can create a rogue machine account, trick the CA into issuing a certificate with the identity of a Domain Controller, authenticate as that DC via PKINIT, gain replication access and basically compromise the whole domain.
So if you run on-prem Active Directory with AD CS and your CA is still unpatched, an ordinary domain user may currently have a path to the highest privileges in your domain.
Patch it, obviously, or apply the temporary mitigation. But if you patched only recently, the harder and from my point of view more important question is: did someone already exploit it?
A patch closes the hole. It does not unfuck a domain that was already compromised.
I put a list of things I would check in the first reply.
Overview:
linkedin.com/posts/martinsoh…
Technical details:
gist.github.com/H0j3n/a5ef26…
PoC:
github.com/aniqfakhrul/CVE-2…
Microsoft advisory:
msrc.microsoft.com/update-gu…
Temporary mitigation:
xitter.cf/aniqfakhrul/status/208…


adib retweeted

If you want to hunt for signs of Certighost (CVE-2026-54121) by @h0j3n and @aniqfakhrul in your #XDR environment try this query.
1. Exclude DCs
2. Identify ADCS servers
3. Check for LDAP or SMB connectivity to any non DC from ADCS
BP for SMB possible!
gist.github.com/f-bader/8c44…

adib retweeted

Yes, CVE-2026-54121 is bad with a public working exploit out now (CertiGhost)… although it’s still worth noting that proper network segmentation would mitigate this. Also, the attacker must have a way to run a fake LDAP server, which is not hard if you already have access to the victim machine. Here’s a flow chart to visualize how bad this is:
Attacker
(low-privileged user)
|
| 1. Creates a
| computer account
v
Starts fake LDAP server
|
| 2. Requests a
| certificate for
| Domain Controller
| DC01
v
Certificate Authority
|
| "I'll contact the
| LDAP server you
| told me about..."
v
Fake LDAP server
controlled by attacker
|
| "Yep, that's DC01"
v
❌!!! VULNERABILITY !!!❌
CA trusts the LDAP response
WITHOUT properly verifying
that it came from the real
Domain Controller.
|
v
CA issues a Domain Controller
certificate to the attacker
|
v
Attacker authenticates
AS the Domain Controller
|
v
Performs DCSync
|
v
Full Active Directory
compromise ✅
msrc.microsoft.com/update-gu…
adib retweeted

New AD CS vulnerability and writeup by @H0j3n and @aniqfakhrul

Happy to share a technical analysis by @h0j3n on our recent CVE-2026-54121 a.k.a Certighost. glhf🔥
Technical analysis: gist.github.com/H0j3n/a5ef26…
POC: github.com/aniqfakhrul/CVE-2…
