

BCON COLLECTIVE is Bridewell’s cyber threat intelligence team, helping organisations build threat-informed defences through timely, and actionable intelligence.
United Kingdom
Joined March 2023
- Tweets71
- Following42
- Followers787
- Likes16






🚨Here are the top malicious infrastructure threats observed during October 2026, based on intelligence collected by BCON.
Last month, CyberStrikeAI was the most frequently observed threat, and Amneisa stealer saw increased activity from September. ➡️go.bridewell.com/4BBcWTb

67


Take a look at our latest live analysis of credential theft malware targeting UK Critical National Infrastructure, pulled directly from the Ransomware. Live PRO API and enriched with infostealer intelligence by BCON Collective.
Read more ➡️ go.bridewell.com/4yttnhf
#CTI #Malware

1
111
🚨BCON Collective tracked 65 ARTEX IPs across 13 locations, led by the US, China and Hong Kong. Some hosts also exposed Cobalt Strike, Gophish or Adaptix signatures. These are investigation leads; compromise is not established.
Read more: go.bridewell.com/4jNlcc3

104
🚨Here are the top malicious infrastructure threats observed during August 2026, based on intelligence collected by our CTI team.
Last month, CyberStrikeAI was the most frequently observed threat, while Cobalt Strike, AdaptixC2 saw increased activity. ➡️go.bridewell.com/3TkHneQ

114
We are tracking an intrusion cluster using email subscription bombing as a precursor to social engineering. One victim received 1,000+ emails in 40 minutes, followed by an external Microsoft Teams chat impersonating IT support.

DPRK IT workers exploit a problem many organisations already have: security signals scattered across Recruitment, HR, IT, IAM, SOC, Procurement and Finance.
Our guide shows you how to join them into one defence ➡️go.bridewell.com/4bUvl1V
#BCONCollective #CTI #DPRKITWorker

Over the coming days we’ll be publishing Defending against DPRK IT Workers: An Implementation and Operational Guide.
The operation crosses Recruitment, HR, IT, IAM, SOC, Procurement and Finance. No single team sees the whole picture.
Watch this space.
#DPRK #InsiderThreat
1
166
View our new live analysis of credential theft malware targeting UK Critical National Infrastructure, pulled directly from the Ransomware. Live PRO API and enriched with infostealer intelligence by BCON Collective. ➡️ go.bridewell.com/4wp4mmo
#BCONCollective #CTI #Ransomware

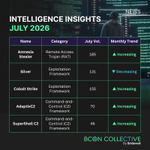
🚨Here are the top malicious infrastructure threats observed during July 2026, based on intelligence collected by our CTI team.
Last month, Amnesia Stealer remained the most frequently observed threat, while Cobalt Strike, AdaptixC2, and SuperShell C2 all saw increased activity.

2
3
217
Tycoon 2FA quickly returned after a temporary disruption, highlighting how resilient phishing-as-a-service operations have become. Discover what this means for defenders.
Read more ➡️go.bridewell.com/44O4CQJ
#BCONCollective #CTI #Tycoon2FA

2
164
Threat actors continue to exploit trusted brands. We analysed a phishing campaign targeting the hospitality sector and explain what security teams can learn from the attackers' tactics.
Read more ➡️go.bridewell.com/4wYDryu
#BCONCollective #CTI #Phishing

Of the three ShinyHunters victims that appear in our recent blog, the average time between domain creation/update is 12.7 days. The time to identify and block is less than that. Make sure proactive monitoring for domain impersonation and COM registration patterns is in place.
Speak to our BCON Collective if you want someone doing this for you: bridewell.com/cyber-threat-i…

1
84
Last week, we shared intelligence on an active campaign observed targeting one of Bridewell's customers - sharing domains indicating wider com-affiliated activity. Today, another org in our data set (RingCentral) has been published by ShinyHunters.

1
230
Have a read of blog here:
bridewell.com/insights/blogs…
IOCs here: github.com/Bridewell-CTI/IOC…

52
LegacyHive is a new, unpatched local privilege escalation vulnerability that targets the Windows User Profile service. Disclosed in July by independent researcher, Nightmare Eclipse, this exploit enables a standard user to mount, read or modify another user's registry hive.


Explore Bridewell’s 2026 Cyber Threat Intelligence Report for insights on identity-led compromise, infostealers, ransomware fragmentation, evolving social engineering and AI-enabled tradecraft.
Download the report: go.bridewell.com/4fPgnwm
#ThreatIntelligence #CyberSecurity

🚨 From a fake IT support ticket to uncovering a wider Com-affiliated vishing campaign.
Bridewell is tracking an active, accelerating wave of Com-affiliated vishing activity. Here’s how one vishing call against a customer led to a much broader investigation. 🧵
#BCONCollective

7
2
204
Visit our new BCON Collective Cyber Threat Insights web page to explore our latest research and discover more about our threat intelligence services: go.bridewell.com/4fnCjxm
#BCONCollective #CTI
3
613
Welcome to BCON Collective, Bridewell’s cyber threat intelligence team, now operating under a new identity. BCON Collective gives us a dedicated platform to share high-quality, actionable intelligence that helps organisations understand the threats they face.
#BCONCollective
We've just published a new report on a Widespread Credential Harvesting Campaign.
Moving forward, all our CTI updates will come from our main account @bridewellsec, so give us a follow to keep up with our latest updates.
#ransomware #threatintelligence

Joshua Penny, our Senior Threat Intelligence Analyst has analysed a widespread credential harvesting campaign. The threat actors are utilising the Dadsec platform to conduct widespread phishing of global organisations to steal Microsoft 365 credentials.
The threat actors are using Cyber Panel, an open-source web development panel, hundreds of Domain Generated Algorithm (DGA) domains that are created daily to host credential harvesting pages.
For more information, including Indicators of Compromise (IoCs) and associated infrastructure, see our full report 👉 bridewell.com/insights/blogs…
@AnyRun_App
#BridewellCTI #ThreatIntelligence
