






Binx retweeted

I like to look at claims like this in case I can improve Ghostty. I grabbed your source and immediately spotted the issue: your read loop overwrites a 64 KiB ring. Everything older is discarded unparsed per tick. You're faster because you're not actually terminal emulating.
It means the number isn't a throughput number. In a kitten benchmark run at the rate you're claiming, roughly 6.6 MB arrives per 60 Hz tick and 64 KiB of it gets parsed. You're read(2)-ing 100% of the data and parsing about 1% of it.
There are other minor issues (a small fixed scrollback in a preallocated ring buffer, no grapheme clustering, throwing away data like OSC 8 URIs, etc.), but the major one is simply that you're discarding ~99% of the input.
For plain text, e.g. your cat benchmark, the final screen ends up looking right, but the scrollback is missing 99% of the file and each retained chunk starts mid-line. As soon as there are escape sequences in the dropped spans, your emulator is fully out of sync and invalid: a cut inside a CSI prints the parameters as text, and any SGR, mode, title, or alt-screen change in the gap is just... gone.
FYI, this is why I don't like when people point at refterm as a terminal benchmark. refterm implements a TINY subset of what a terminal emulator must support, it's closer to a fast file reader, not a terminal emulator.
I also don't mean any shade by this. I like to look at technology objectively to try to learn something and improve my own craft and work. So I'm sharing what I found.
I modified your code very slightly to parse on every full buffer (rather than per tick). And the results are attached. Both use main commit in each repo at the time of this post.
Note the graph is in log scale, the discrepancy between performance for things like Kitty images is measured in GB/s.

Binx retweeted

That is one hell of a typo.


Announcing 3 Critical vulns for hundreds of millions of IoT, Firewalls, OT, and Military devices including: Palo Alto Networks, Comcast, D-Link, HP, Canon, Honeywell, GE, Oracle, Siemens, Rockwell, Digi, Lockheed Martin, Boeing...
The vulns are with GoAhead Web Server which is a backend library used by these devices. There's a patch available from GoAhead but that doesn't mean there's a patch available for the devices yet -- that's up to the manufacturer.
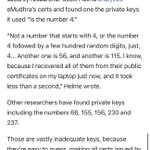
- TLS traffic over DHE ciphers have a 1-byte secret, "04", meaning anyone can decrypt connections to these devices and steal login credentials and session tokens if the client negotiated with DHE ciphers like the latest TLS_DHE_RSA_WITH_CHACHA20_POLY1305_SHA256, which is extremely likely.
- LibreSSL mTLS has been completely bypassed, meaning anyone can connect over mTLS. If you have one of these devices listening on the internet and are expecting mTLS to protect it from attackers, take it offline or patch asap.
- OpenSSL Certificate Revocation Lists (CRLs) are not enforced, meaning if a user device is stolen or compromised, and you revoke that mTLS cert, nothing actually happens. There are a lot of other attacks this can be used for.
These are critical because these types of devices run our world. Water systems, electricity, military, firewalls, critical infrastructure.
foxio.io/blog/choose-your-ba…

Binx retweeted

So one of our ambassadors @divagr1925 has been working on something cool
He found a way to use Qwen's Gated DeltaNet state as memory, and built a 32-bit RISC-V CPU directly into the model's weights. So instead of relying on predicting the answer to a calculation, the model can execute instructions internally. It can also run C and MicroPython programs.
He calls it Qwenputer, love the name btw. The results so far are pretty impressive. On one arithmetic benchmark, accuracy jumped from 48.6% to 100%.
Pretty cool to see developers experimenting with Qwen's architecture. Great work, my friend!

Binx retweeted

Really cool! Local models get self-steering. This is something humans are mostly incapable of. Add J-space monitoring and you get close to enlightenment.


This inspired me to make a library to let agents run on local models change their own activations temporarily. (It wears off after a few turns to stop them getting stuck.) github.com/EigenformAI/modul…

Binx retweeted

Introducing 𝙻𝙵𝙼𝟹: our new generation of Liquid Foundation Models. With a new tri-hybrid architecture and new multimodal encoders, the LFM3 family is the ideal model suite for specialized intelligence.
> 6 model instances, across text, audio, vision, and omni modalities, generative and decision models.
> 𝙻𝙵𝙼𝟹-𝟷.𝟽𝙱: text, 256k context window.
> 𝙻𝙵𝙼𝟹-𝚅𝙻-𝟸𝙱: vision-language model with video-input support for spatial understanding
> 𝙻𝙵𝙼𝟹-𝙰𝚞𝚍𝚒𝚘-𝟸𝙱: tool calls, voice chat, reasoning in 18 languages.
> 𝙻𝙵𝙼𝟹-𝙾𝚖𝚗𝚒-𝟸𝙱: an omni model combines vision, audio, and language.
> 𝚍𝟷-𝟸𝙱 and 𝚍𝟷-𝙾𝚖𝚗𝚒-𝟸𝙱: decision models with typed outputs and calibrated probabilities in a single pass. Omni adds audio input.
> fine-tune on 1 GPU.
> a new tri-hybrid architecture
> architecture optimized for 14 processor classes across GPUs, CPUs, and NPUs.
> 𝙻𝙵𝙼𝟹-𝚅𝙻-𝟸𝙱 is a beast. It performs competitively with Gemma 4 12B (6x larger), and Gemini 3.5 Flash Lite, and GPT-5.6 Luna, with 1.9B parameters.
> 𝙻𝙵𝙼𝟹-𝟷.𝟽𝙱 is #1 on the Pareto frontier of device intelligence 𝚙𝚒𝚙𝚎𝚝𝚝𝚎.𝚕𝚒𝚚𝚞𝚒𝚍.𝚊𝚒
Every modality for specialized intelligence. Pick the one that fits your use case, customize it, and run it on-device.
1/ 🧵
Binx retweeted

Holy, $200 Chinese car stereo has a root backdoor spyware and an always-listening mic.
- Always-listening mic burning 30% CPU.
- Pre-installed call recorder.
- Vendor root backdoor.
- Baidu location + logging running in background
- Silent APK installer that runs on every boot.
- Fake specs (claimed Android 15/8-core, actual Android 9 /4-core, 2021 patch).
He then used Claude to neutralize the backdoors, remove 18 packages, block trackers, and build a custom launcher.
I resize the image for better visibility,


a user (u/Crunchy-Nut1) on our r/claudecode subreddit community connected claude code to his honda civic's chinese head unit.
he found that:
- a voice assistant was always listening for its wake word and running a hidden webview that consumed ~30% cpu even when nobody was talking
- a call recorder was preinstalled on the device handling his bluetooth calls
- the firmware had a root backdoor left by the vendor.
- a startup script silently installed any apk placed in a hidden folder, then deleted the file.
- the vendor's update app could push new firmware remotely.
- baidu location services and a vendor log collector were running in the background.
- the listing claimed device had 8 cores and android 15. the actual hardware had 4 cores and android 9, with a security patch from october 2021.
he then used claude code to:
- disable the always-listening assistant and other unwanted apps, then remove 18 packages after backing them up.
- shut down the root backdoor and hidden apk installation mechanism.
- disable the vendor's cloud updater.
- configure adguard private dns to block ads and trackers.
- upgrade android webview from version 66 to 138.
- build a custom civic launcher, generate its icons, and recalibrate the backup camera guidelines
- install open-source apps with sha-256 verification and lock down network access
debloating your cheap hardware is a pretty sick usecase of claude code

Binx retweeted

UPDATE: Israeli company we caught delivering zero-click infections is #1 bidder on Starlink ads in 105 countries.
Data from @trendai_RSRCH suggests worldwide surveillance op targeting @Starlink users. 1/
By @razhael
reuters.com/business/media-t…


🚨NEW INVESTIGATION: zero-click mercenary spyware hacking via targeted ads.
A normal-looking ad loads. If you're a target, you're infected. No click needed.
To protect yourself, block ads now.
First time it's been confirmed in the wild. We call it #AdFection.
Candiru spyware infections at @AJEnglish. 45+ devices infected.
Same ad pipeline operated by Israeli company Discover-Tech reached NATO, European Parliament, dozens of gov networks & critical infrastructure incl US nuclear giant Westinghouse.
Confiant, which worked with us, found signs ads were displayed at US @DeptofWar, IAEA & ICC.
Investigation ongoing 1/
READ our report by @billmarczak @WolfieChristl, me Astrid Perry, Siena Anstis & Ron Deibert : citizenlab.ca/research/how-d…
Confiant's blog: blog.confiant.com/p/adint-we…


Binx retweeted

Are we having fun yet?

🚨 A working root exploit for a Linux kernel bug is public. No CVE. No merged fix.
ZDI-CAN-33367 is a gap in the Dirty Frag fix, with root confirmed on current Ubuntu, Debian, and AlmaLinux. Restrict unprivileged user namespaces and enforce seccomp RuntimeDefault while you wait.
okt.to/08psRf
#CloudSecurity #ThreatResearch #Linux #RuntimeSecurity

Binx retweeted

Phreaking an iPhone

You can point an ultrasonic speaker at an iPhone from a few feet away, play an audio command that no human ear can hear, and the phone will wake up, open Safari, and dial a phone number.
To everyone standing in the room, it sounds like dead silence. To the phone, it sounds like someone speaking directly into the microphone.
Mobile operating systems use digital low-pass filters to delete all sound above 20,000 Hz, assuming inaudible frequencies can never reach the voice assistant.
Yet this attack succeeds without exploiting a single line of software code. The flaw is not in the operating system. It is in the microscopic silicon plate inside the microphone itself.
1. The microscopic machine inside your microphone
Inside modern smartphones, microphones are not miniature versions of studio microphones. They are micro-electro-mechanical systems (MEMS) chips smaller than a grain of rice.
Inside the chip package sits a flexible silicon diaphragm suspended barely two micrometers above a rigid metal backplate.
The two plates form a variable capacitor. When sound waves hit the silicon diaphragm, it flexes inward and outward, changing the electrical capacitance. An onboard preamplifier converts that movement into an electrical voltage.
At normal room volumes, the silicon plate moves evenly: double the sound pressure, and the plate flexes twice as far.
2. The non-linear spring catch
The flaw appears when sound waves hit the microphone at high pressure (above 90 dB SPL).
If you broadcast an ultrasound carrier wave (say, 28,000 Hz) that has an audio command modulated on top of it, the microphone front-end cannot move symmetrically. The mechanical spring resistance of the silicon, the electrical pull between the plates, and the preamplifier circuit all reach their limits.
Instead of flexing smoothly, the silicon plate bends slightly more inward than outward.
This asymmetry acts like an old crystal radio receiver. Mathematically, a non-linear response squares the incoming wave. That squaring action strips the silent 28,000 Hz carrier away and leaves behind the original human voice command in the audible 300 Hz to 3,500 Hz range.
By the time the analog-to-digital converter reads the signal, the ultrasound is already gone. It has physically transformed into ordinary low-frequency sound inside the microphone chamber. The phone digital filter never triggers because the audio reaching the software is already normal human voice.
3. What researchers actually proved (DolphinAttack)
In 2017, researchers at Zhejiang University published DolphinAttack, demonstrating this hardware flaw across Siri, Google Now, and Alexa.
They successfully forced phones to initiate FaceTime calls, navigate to malicious websites, turn on airplane mode, and unlock smart doors paired to the device.
Later research expanded this into attacking through solid tables, using the furniture itself as a physical acoustic conductor.
4. Why this fails in the wild (The physical friction)
Demonstrating this in an acoustic laboratory is straightforward. Pulling it off in a crowded coffee shop runs into strict physical limits:
First, air absorbs high-frequency sound rapidly. Bass travels through concrete walls, but 30,000 Hz ultrasound loses roughly 1 to 1.5 decibels of power per meter in normal room air. In the original DolphinAttack paper, the effective range was limited between a few centimeters and 1.75 meters. Reaching across an entire room requires a heavy array of high-voltage transducers.
Second, ultrasonic emitters act like laser pointers. High-frequency sound travels in narrow beams of 15 to 20 degrees. If you fail to aim directly at the phone one-millimeter microphone port, sound pressure drops below the 90 dB threshold needed to bend the plate.
Third, modern phones are waterproof. Devices with IP68 ratings place a hydrophobic Gore-Tex mesh over the microphone hole. The mesh lets air equalize while stopping water, but it acts like a dense acoustic muffler against ultrasonic frequencies, absorbing another 14 dB of signal strength.
Finally, voice assistants use personal voice training. If Siri or Google Assistant is set to only respond to the device owner, a generic synthesized ultrasonic command is ignored unless the attacker models the owner vocal pitch.
5. How modern hardware catches it
Defending against inaudible voice injection requires catching the acoustic mismatch before speech recognition executes:
* Multi-microphone cross-checks: Modern smartphones carry three or four microphones positioned on the bottom, top, and camera bump. When a real human speaks, their voice reaches all microphones with natural arrival delays. A narrow ultrasonic beam hitting one microphone port creates an unnatural phase imbalance across the device.
* Harmonic distortion analysis: When a microphone is driven into non-linear demodulation, it does not produce a clean voice recording. It leaves distinct distortion products and second-order harmonics. Software filters can analyze the spectrum and mute the assistant if they detect the signature of mechanical demodulation.
* Acoustic damping barriers: Microphone manufacturers can install physical acoustic damping layers inside the chip housing that attenuate frequencies above 22,000 Hz before the sound wave ever reaches the silicon diaphragm.
Inaudible voice injection works because digital security models assume analog sensors behave linearly. When sound waves push silicon past its linear limits, the hardware itself executes operations the operating system never authorized.

Binx retweeted

Mozilla released Firefox 159 and security advisories for ESR 153.6 and 115.44.
Fixes include CVE-2026-117861 (sandbox escape), CVE-2026-117860 (same-origin policy bypass), privilege-escalation bugs and numerous memory-safety flaws affecting browser security boundaries.
mozilla.org/en-US/security/a…


Binx retweeted

Now THAT is what losing looks like, holy fuck.

Binx retweeted

Physical Superintelligence launched in September with a $58 million seed. Today they announced five new results on open problems in quantum information theory, with a paper and Lean formalization for each of Open Quantum Problems 2, 12, 27, 38, and 43.


Today Physical Superintelligence PBC is announcing solutions to five long-standing problems in quantum information theory.
psi.inc/research/oqp-batch-2…
Thread 👇


Binx retweeted

I can't believe we're experiencing an interp renaissance based on the idea of... Seeing what neurons do.
It was right there the whole time.

i opened up an AI's brain tonight with @_lyraaaa_'s neuron explorer
qwen 3.5 4b has 294,912 neurons
push just one and it becomes someone else
here's who i found 🧵

