
A peculiar digital creature of some sort. Streamer/Youtuber, IT/infosec pro, Captain. I inspire people when able. Otherwise I do w/e chaotic fun.
Finland
Joined September 2010
- Tweets7.1K
- Following2K
- Followers328
- Likes14.3K


Tatu / dTA retweeted

No fucking way
ITS 4 AGAIN
DIFFERENT BUG


Announcing 3 Critical vulns for hundreds of millions of IoT, Firewalls, OT, and Military devices including: Palo Alto Networks, Comcast, D-Link, HP, Canon, Honeywell, GE, Oracle, Siemens, Rockwell, Digi, Lockheed Martin, Boeing...
The vulns are with GoAhead Web Server which is a backend library used by these devices. There's a patch available from GoAhead but that doesn't mean there's a patch available for the devices yet -- that's up to the manufacturer.
- TLS traffic over DHE ciphers have a 1-byte secret, "04", meaning anyone can decrypt connections to these devices and steal login credentials and session tokens if the client negotiated with DHE ciphers like the latest TLS_DHE_RSA_WITH_CHACHA20_POLY1305_SHA256, which is extremely likely.
- LibreSSL mTLS has been completely bypassed, meaning anyone can connect over mTLS. If you have one of these devices listening on the internet and are expecting mTLS to protect it from attackers, take it offline or patch asap.
- OpenSSL Certificate Revocation Lists (CRLs) are not enforced, meaning if a user device is stolen or compromised, and you revoke that mTLS cert, nothing actually happens. There are a lot of other attacks this can be used for.
These are critical because these types of devices run our world. Water systems, electricity, military, firewalls, critical infrastructure.
foxio.io/blog/choose-your-ba…

Tatu / dTA retweeted

Riot Games opened today’s Worlds broadcast with a tribute to Lauri "Cyanide" Happonen 🇫🇮 following news of his passing.
"You will never be forgotten, please join us in a moment of silence as we honor his legacy"

Sad news

We are deeply saddened to learn of the passing of Lauri “Cyanide" Happonen earlier this year.
During his four-year spell at Fnatic, Cyanide made history as the youngest ever player to win Worlds at just 16. He leaves behind a legacy that will never be forgotten.
Our heartfelt condolences go out to his family, friends, and everyone whose lives he touched.
Rest in peace, Cyanide. 🧡🖤

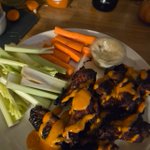
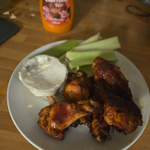
Hot wings with celery, carrots, buffalo sauce and horseradish infused mayonnaise #food #cooking #cookingwithtatu #omnomnom



And they don't stop coming and they don't stop coming

Ruby’s turn 😅
Remember the GitLab bug? Well now it moved upstream into Ruby.
Multiple 10.0 CRITICAL exploits.
Patch now 🚨
Happy Friday 🤠
ruby-lang.org/en/news/2026/1…

Tatu / dTA retweeted

There are a lot of uncomfortable conversations going on in boardrooms across America and elsewhere this morning.
Leadership is asking questions which make them squirm like
"How come we didn't know we had all these vulnerable software packages in our environment?"
And they're being told, by technical people who are terrified of losing their jobs, facing uncertain futures with all this AI crap and misinformed leadership making increasingly poor decisions which only make things worse, that the reason this is all happening is because for years they were hamstrung and prevented from doing those jobs, BY THAT SAME LEADERSHIP.
Patching.
Updating software.
Documentation.
Asset Management. I wrote a book on it. Check it out.😉
How can you protect your assets if you don't know how many you have and what they are and where they are?
No, you can't have that money in your budget to do your work because we have to use it to spend it on stupid things like tokens.
No, you can't take down a production system in the middle of the day and we're not going to approve any overtime either so figure it out.
Except it wasn't figured out because in order to update it the system needs to be taken offline.
And the technical people need to be able to do those updates without having some megalomaniac breathing down their neck asking the dumbest questions like ETA? 🙄
ETA.
When it gets done, dumbass. That's when.
Is this harsh? Yes.
Once again this is a revealing incident showing that all these companies who love to brag how secure they are, really aren't in reality.
But that is not the fault of the technical staff.
That's the fault of the guys and gals in the top echelon who are supposedly managing all these businesses but doing a very poor job of it.
They never get called out though.
I think we need to change that.
I think all layoffs need to be in a moratorium status because it's clear to me that the very last thing you want to do is get rid of the individuals in your company who are going to help you clean up from all the vulnerabilities which need to be patched in the coming days weeks and months.
Yesterday was a precursor.
A taste of what is to come.
Now is not the time to be laying off those who have the technical skill to help you recover from the fallout.
Stop worrying about vibe coding idiotic projects that aren't going to make your company any money and start worrying about protecting the assets you have today.
Invest in the people whose work got you all that money you are spending on this AI shit and prioritize giving them the tools to make your organization even stronger.
AI models are not alive.
They do not have consciousness now and they're not going to.
Play books that they are running right now are based on human technical experts notes. They aren't inventing anything new.
They are reading what it is we have done in reality and mimicking that.
And they are going to be successful in hacking you because you haven't allowed your technical staff to do their jobs which you hired them to do.
Listen to your cybersecurity staff.
Listen to your information technology staff.
Instead of restructuring your human assets start shuffling around money and shoring up technical budgets so that they can do those jobs properly.
And stop with the bullshit excuses.
Do you want to get sued?
Because that's where this is going to end up if you don't start getting your technical houses in order.
That starts with everything I said above.
And the very first thing that you need to take offline is those stupid AI chatbots that you put on your websites.
Your customers hate them.
They loop.
They want to speak to a human.
And you should try it yourselves.
There's a number of them working for you.
That's how you get paid the ridiculous salaries you make.
How's about talking to them for a change, instead of at them? 🙄


Tatu / dTA retweeted

Some stats on #php2shell. In the 10 hours before it was publicly announced, across the @Cloudflare network we saw thousands of attempts to exploit it. That jumped to tens of thousands in the 45 minutes post announcement, hundreds of thousands within 2 hours, and millions now.
Tatu / dTA retweeted

So basically, today PHP got two critical bugs that let anyone run code on your server without even logging in, which is bad, and then the details leaked before the patch was even out, which is worse, and it works on WordPress and MediaWiki and Magento and Joomla and Laravel, and Censys says like 1.5 million servers are running a version with no fix, so the NSA was like "take your system offline," and the FBI was like "take your system offline," and CISA and the UK and CERT-EU were all like "take your system offline," and then the Prime Minister of Japan, the actual Prime Minister, posted at 5:55 in the morning telling 48.8 million people to take their system offline, so everyone took their system offline, like the Dutch cybersecurity agency took its own website offline, and the Dutch parliament went offline, and the Port of Rotterdam went offline, and Finland and France and Denmark started pulling government sites, and Wikipedia went down, and Archive.org went down, and Asana and GOG and Something Awful went down, and the University of Vienna's webmail went down for some reason, and that's just PHP. Because GitLab also dropped a CVSS 10.0, which is the highest score they give out, for a bug that's been there since 2014, so that's every self-hosted GitLab for twelve years, and then LiteLLM 1.107.0 got hijacked and shipped a credential stealer and a remote access trojan in every single wheel and the Docker images, including latest, and you didn't even have to import it, just installing it was enough, and it's the second time this year, and then Railway paused every deployment on the entire platform because someone got into the environment variables, so now everyone has to rotate every secret they've ever stored there, and TiDB Cloud said someone was walking around inside with stolen credentials for basically a month and an extortion group says they took 10.6 terabytes, and Zeabur got breached for the second time in two months and is just shutting down, like the whole company, and Node.js patched remote code execution and a TLS bypass, and CISA says Plex is being actively exploited, and someone took over 300 Tor exit relays to steal SSH passwords, and SafePay ransomware has hit over 600 critical infrastructure orgs, and India's biggest bank filed a data loss incident, and Japan has been in an official state of emergency in cyberspace since October 9, which honestly explains the 5:55 AM post. Oh, and eMudhra, a certificate authority that's issued over 60 million certificates, whose entire job is proving websites are who they say they are, was supposed to be using private keys that are random numbers over a hundred digits long, and one of them was 4. Just 4. And the others were like 66 and 237. Anyway, it's Wednesday.

Tatu / dTA retweeted
"On October 21st at 07:41 UTC, more than six hours before the coordinated release, Chainguard unilaterally broke the embargo and published built images containing the fix. Like other distributors, Chainguard had received the patch in advance so its users could update the moment the vulnerabilities were disclosed. Any attacker could now study the fix in binary form while every other PHP user was still waiting for the release. This disregarded weeks of work by many parties toward a coordinated disclosure."
thephp.foundation/blog/2026/…

Right lets take a look at this PHP vuln | gaming after twitch.tv/digitalta

Tatu / dTA retweeted

More private keys by the Indian certificate authority have been discovered. These are all small numbers.
People are suspecting that they interpreted 384 bit keys to mean that they should pick numbers from 1-384 to use as their private keys.


Hey @kibawoo I watched the debut VOD. Random question if you'll indulge me, what is your favourite sauce with the chicken wings? From the color in the debut slide I'd guess it is the horseradish-imbued stuff but figured I'd ask
