


Magn4 retweeted
@nullcon x German @Hacker0x01 Club: Community LHE and Bug Bounty Meetup 🧑💻
For the first time, the German HackerOne Club is heading to Nullcon Berlin 2026!
📆 November 5 – 6, 2026
📍Maritim proArte Hotel Berlin
(1/2)
#BugBounty #Meetup #LHE #Nullcon #Hackerone #Berlin


Magn4 retweeted
New Video Out 🙌
In this one i explained how hackers use the Dev tools to find client side bugs, and bypass restrictions.
And to not only focus on theory, i have used the dev tools live to find 2 vulnerabilities.
Hope you guys will enjoy it 🫡
youtube.com/watch?v=bVL_m0qe…
Magn4 retweeted

So, do you want to do Bug Bounty in Mobile Apps? 💰📱
🤔 Frida maybe a headache with actual modern RASP protections, so I published my personal method to Bypass SSL Pinning on Play Store Android Emulators WITHOUT Frida!👇
#bugbountytips #bugbounty #hacking
mfumis.com/posts/bypassing-s…

Magn4 retweeted

Had a Self-XSS chain that I struggled to exploit alone, but after some brainstorming and help from @J0R1AN, I was able to successfully exploit it using disk cache
here is the writeup
medium.com/@spoderx555/escal…


Magn4 retweeted
Hacking Meetup "Friendly Edition" 🇳🇱 vs 🇩🇪
The @Hacker0x01 Club Netherlands and HackerOne Club Germany are teaming up for a cross-club bug bounty competition - inspired by the HackerOne Ambassador World Cup.
#BugBounty #Meetup
(1/3)

Magn4 retweeted

Found a very cool CSPT bug where a low privilege user can delete every account in the org + the entire org itself with 0 interaction at all🔥
Thanks to @Magn4_ for explaining CSPT so well 👌
Need a writeup? Follow me on Medium 👇
mugh33ra.medium.com

Magn4 retweeted

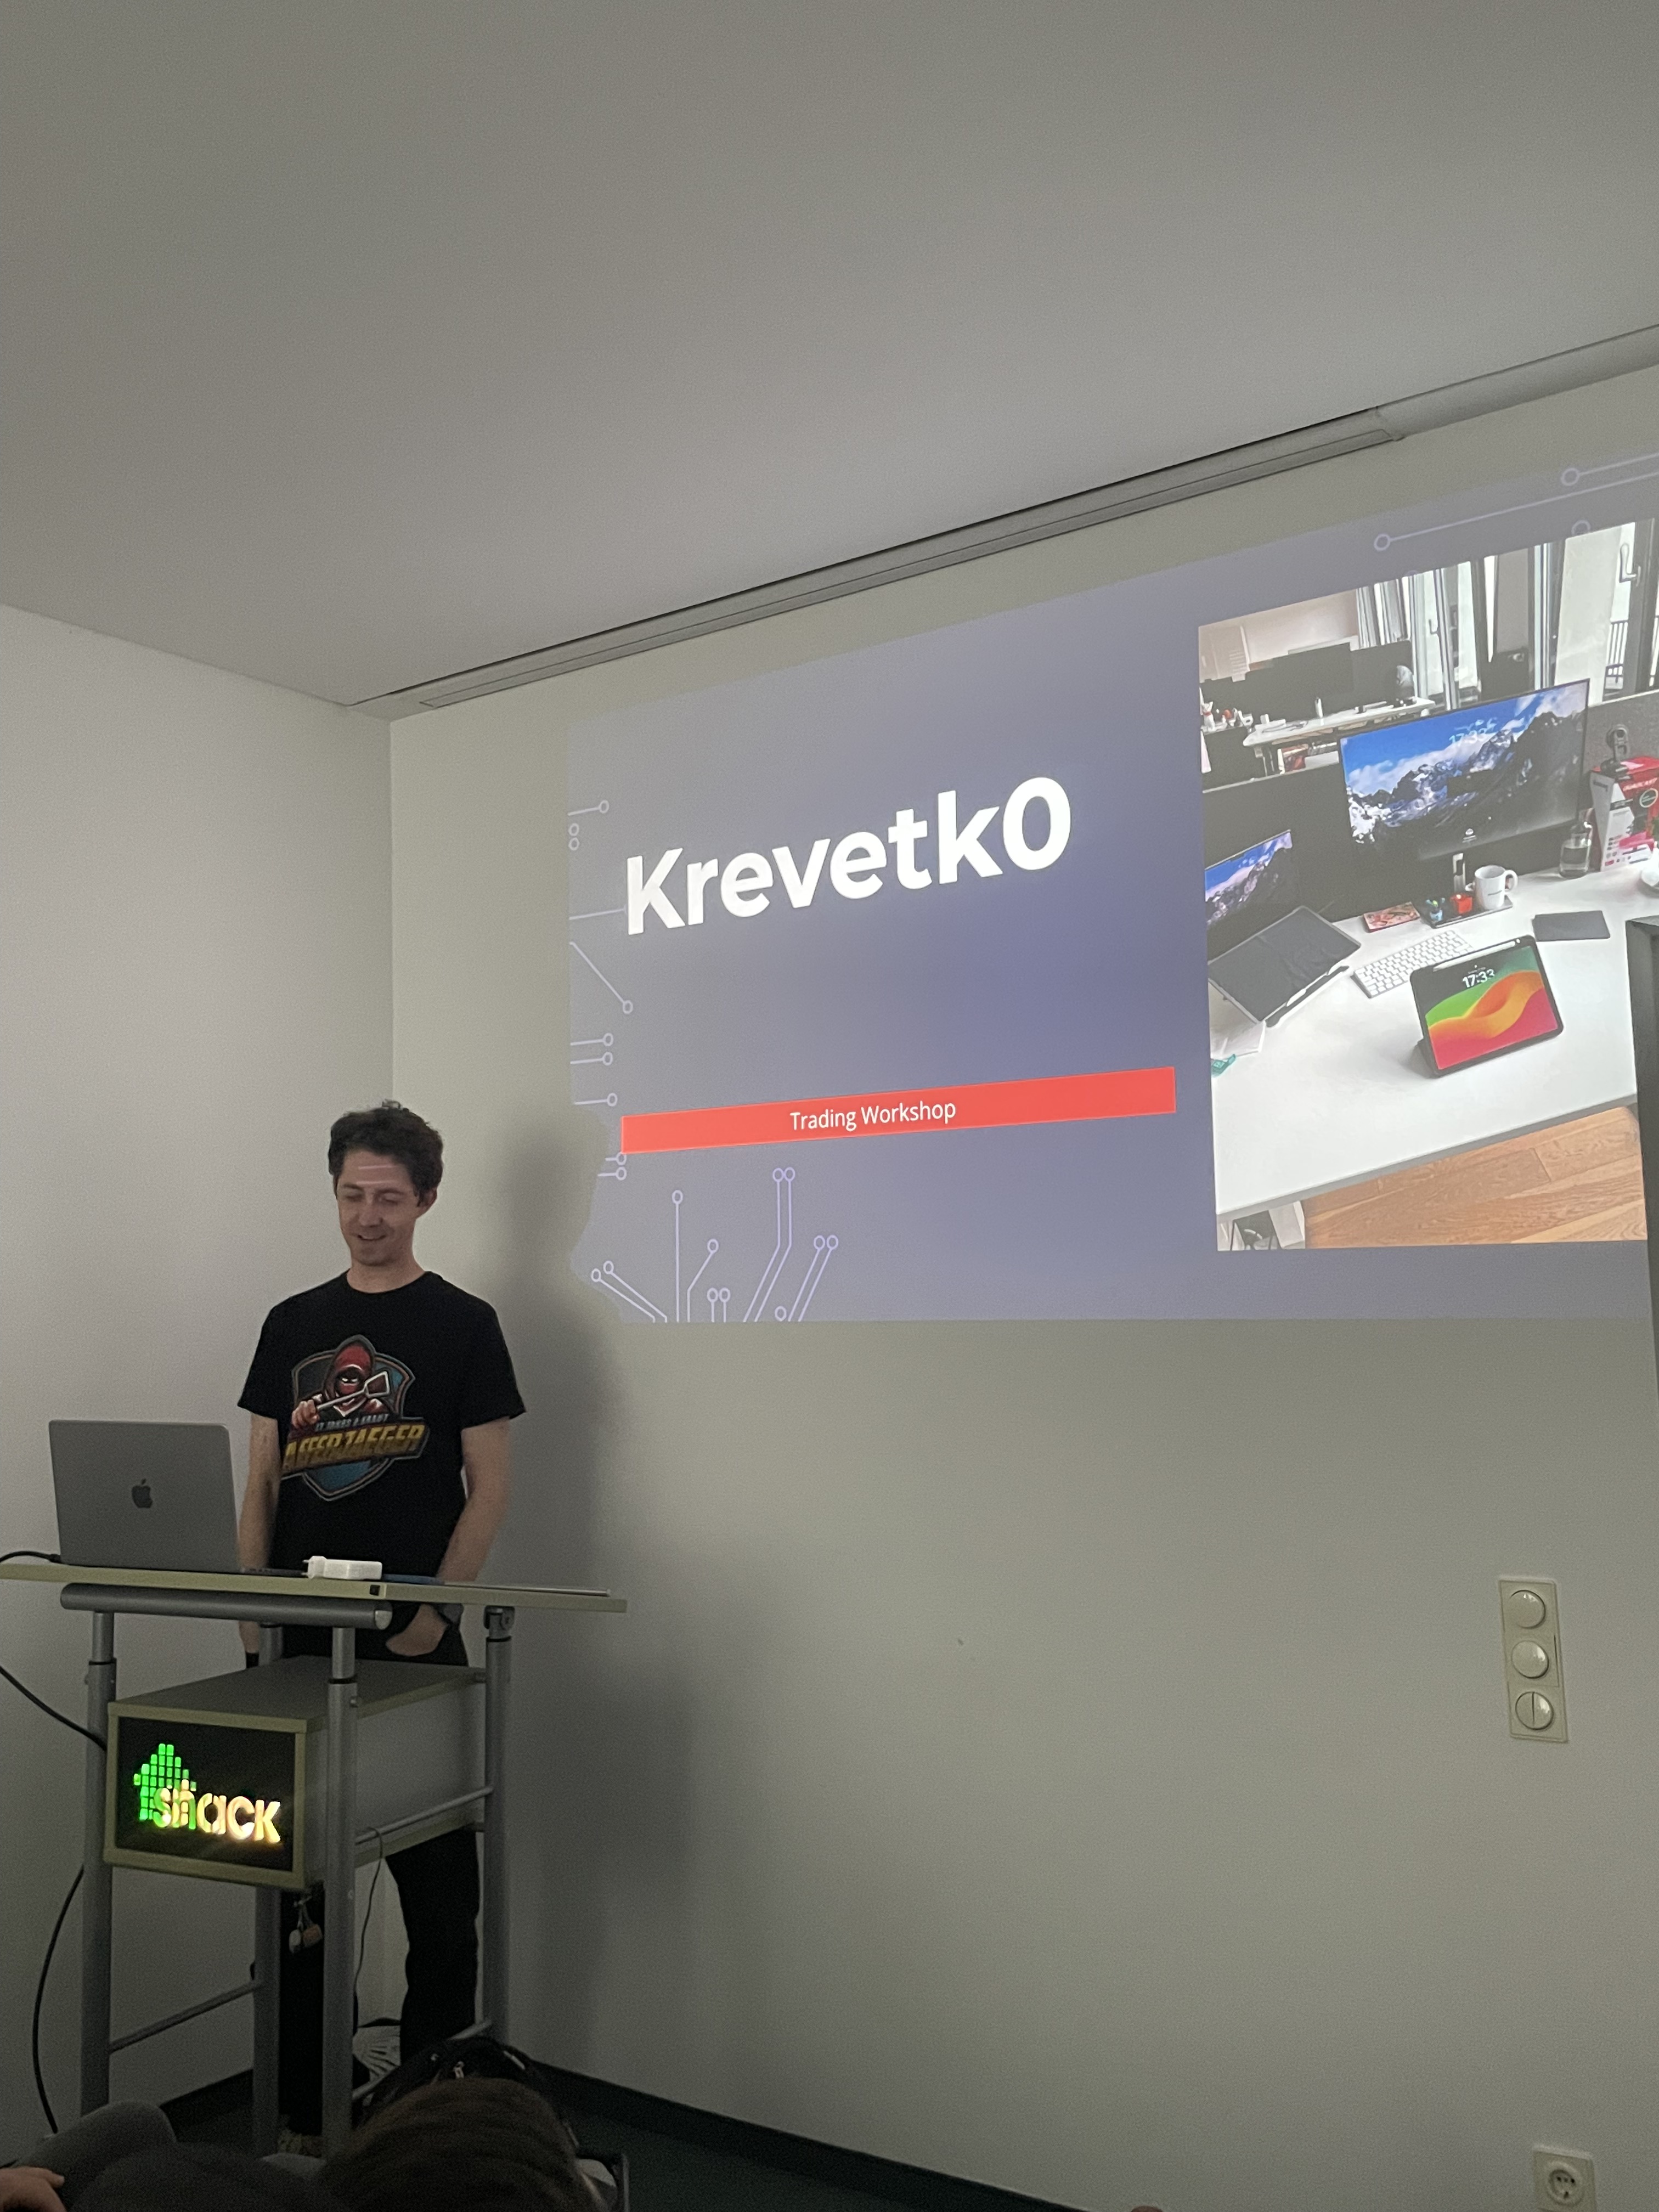
🚀 First @intigriti Bug Bounty Meetup Stuttgart was a success! 🇩🇪
🔥 great conversations
🔥 knowledge sharing
🔥 awesome atmosphere
🔥 hands-on hacking
Huge thanks to everyone who joined 🙌
Next one coming soon 👀



Magn4 retweeted

Chained CSPT into full account takeover using a 2FA bypass technique I hadn't seen used in bug bounty before.
whoareme.com/blog/cspt-accou…

Magn4 retweeted

I actually found it without AI 😅teapawt.net/elmehdimee/status/2036…


Magn4 retweeted

I really love this poll because it lets you discover a lot of great research from the past year that you might have missed.
I've decided to highlight the Сlient-Side related research that I think is especially worth your attention.

Voting is now live for the top ten web hacking techniques of 2025! Grab a coffee, browse the 61 quality nominations and cast your vote on the most creative and ground-breaking techniques:
portswigger.net/polls/top-10…

Magn4 retweeted

One of the best video and youtube channel dedicated to bug bounty.
Highly recommended.
@Magn4_ Respect🫡.
#Bugbounty #bountytips #hackerone #cybersecurity #hacking #infosec

New Video Out 🙌
In this one i explained what Client Side path traversal is, how to find it, and how to exploit. So even if you have no idea what it is, you will have all the knowledge needed to find one after watching the video.
This is by far my best video so far, and on my favorite bug, so i hope you guys will enjoy it, and learn something from it
youtube.com/watch?v=T6BKQ2O0…
Magn4 retweeted
4th place in the German Club LHE 😁 (Even tho not all bugs have been rewarded yet)
I had 0 expectations joining the event, just exited to hack with some insanely talented folks, and learn as much as i can.
And then out of nowhere i started finding some pretty nice bugs.
Special thanks go to @_lauritz_ (The German H1 Ambassador) for all his efforts, and @_ArtSec_ , pprad for the nice competition and all the collaborative work 🙌
PS: Get in contact with your local @Hacker0x01 Ambassador to participate in such events


Magn4 retweeted
I built an app to bypass ChatGPT's upload limits with one simple trick 😮💨
ChatGPT: "3-10 files max"
Me: uploads 50 files as ONE single file
OneFile merges unlimited files into one, so you can upload to any AI platform (ChatGPT, Gemini, etc.)
300+ monthly users. $0 marketing 🔥
Completely free & open-source: (link in first comment)
Magn4 retweeted

في هاذ الحلقة غادي نشوفو مع الضيوف ديالنا الثغرات الأمنية الأكثر شهرة و أهمية في الويب، حسب التقرير المستمر ديال منظمة OWASP. بالإضافة للتعريف بهاذ الثغرات، غادي نكتاشفو أمثلة على هاذ الثغرات و على الطرق باش نحميو راسنا منهم.

Magn4 retweeted

I found out that you can use "ftp::" to convert a limited Dom Clobering situation into a full CSPT. Then, while talking about it with @LooseSecurity, he found that we can also use "https::"
This can be used to prevent URL parsing of href, allowing us to hit other endpoints


