MalasadaTech (@MalasadaTech) header
MalasadaTech (@MalasadaTech) profile picture

ALOJAHZ WORLD! HOBBYIST THRUNTELLISEARCHER. VIEWS ARE MY OWN! 808 https://teapawt.net/t.co/5AFyJj7uay

ON-ISLAND
Joined August 2025
Photo by MalasadaTech (@MalasadaTech)Photo by MalasadaTech (@MalasadaTech)Photo by MalasadaTech (@MalasadaTech)Photo by MalasadaTech (@MalasadaTech)Photo by MalasadaTech (@MalasadaTech)Photo by MalasadaTech (@MalasadaTech)Photo by MalasadaTech (@MalasadaTech)Photo by MalasadaTech (@MalasadaTech)Photo by MalasadaTech (@MalasadaTech)Photo by MalasadaTech (@MalasadaTech)
MalasadaTech retweeted
⚠️Observed phishing URLs delivering RMM payload: RMM: Action1 Theme: Microsoft Teams URL: hxxps://teamsmeeting[.]site #ThreatIntel #Phishing #RMM
2
3
10
607
MalasadaTech retweeted
⚠️Observed phishing URLs delivering RMM payload: RMM: ScreenConnect Theme: Adobe URL: hxxps://ashland-energy[.]com/aa/ Download URL: hxxps://cleaningbyme.screenconnect[.]com/Bin/ScreenConnect.ClientSetup.exe #ThreatIntel #Phishing #RMM
1
4
8
499
MalasadaTech retweeted
🚨 Found another ClickFix page using a fake Windows Security verification prompt. The page copies an mshta command to the clipboard, which downloads the payload from MediaFire, saves it as %TEMP%\verification.exe, and executes it. The payload was observed attempting to exfiltrate data to Telegram using /sendDocument with the Everest/1.0 User-Agent. IOCs: ClickFix: hxxps://acmaturaky[.]cz Payload: e5233db1 (1).exe 51ad155fbf524318fb773d2334b0975c90e1cbbcaae1c58c98f0353fa530143e Payload host: hxxps://www[.]mediafire[.]com/file/yldoq9125h0znvl/e5233db1+(1)[.]exe/file?dkey=id39ilo7cpx&r=40 Dropped as: %TEMP%\verification.exe Telegram C2: api[.]telegram[.]org Bot ID: 8661764894 Chat ID: -1003967691004 Method: sendDocument User-Agent: Everest/1.0 #ClickFix #Malware #Infostealer #ThreatIntel #Telegram #mshta #CyberSecurity #IOC @malwrhunterteam @500mk500 @skocherhan @James_inthe_box @KirkDerpca @getbstr @urlyzeio @smica83
4
8
1
43
2,892
MalasadaTech retweeted
The ENKI WhiteHat Threat Research Team has identified a number of recent Kimsuky spear phishing cases against South Korean and Japanese targets. Aug 20, 2026 enki.co.kr/en/media-center/b…
8
1
59
4,838
MalasadaTech retweeted
7c:c2:55:75:de:bd win-n10se95a1ib
The ENKI WhiteHat Threat Research Team has identified a number of recent Kimsuky spear phishing cases against South Korean and Japanese targets. Aug 20, 2026 enki.co.kr/en/media-center/b…
1
3
17
1,210
MalasadaTech retweeted
The code-signing certificate for "OpsBridge LLC" is revoked. We continue to see new brands of RMM tools pop up and drop ScreenConnect immediately. We (CertGraveyard) didn't report the cert, but other's aren't putting up with this either. Others reported that OpsBridge was all kinds of suspicious: registered with throw-away email accounts, sold via Telegram, etc. virustotal.com/gui/file/7c6a… Thanks for those reviewing, writing, tweeting, about this type of stuff. @ExpectedErr0r @0xBurgers @devmihaylov. Your work is seen and appreciated.
OpsBridge - EV-signed MSI, RMM implant, silent ScreenConnect deploy. flavourworld[.]es/invite/ opsbridge[.]digital pub-45afe949f9564e33acd276c93be952c8[.]r2[.]dev relay[.]tolreanrust[.]site:8041 server[.]tolreanrust[.]site medium.com/@devmihaylov/an-o…
1
11
24
3,270
MalasadaTech retweeted
Fake Microsoft websites are tricking victims into uninstalling their antivirus. We found eleven of these sites on a single host that run a fake security scan designed to get victims to remove their security software and hand over personal, banking, and remote-access information.
2
22
3
77
6,195
Massive #ClickFix campaign
Compromised Site -> #ClickFix Malicious Domain: ultraspeed[.]pro urlscan.io/search/#ultraspee… #malware
1
11
96
11,872
MalasadaTech retweeted
New #ClickFix campaign leverages on-the-fly WebAssembly and #steganography through SVG files. Pages from legitimate but compromised sites lead to fake verification pages that instruct viewers to paste content into a Run window. Details at bit.ly/4gCuNAZ
2
54
4
212
20,962
🚨 UPDATE: The Google-abusing #Magecart campaign we exposed in late 2024 teapawt.net/sdcyberresearch/status… Is now being used for #ClickFix attacks 👇 1️⃣ A WebSocket opens to metrics.brandiser.\net 2️⃣ Its incoming message runs & fires a fake request to accounts.google[.]com 3️⃣ The reflected code calls consent.trandiqs.\com 4️⃣ The response serves the ClickFix attack #ClientSideSecurity #infosec #malware #magecart
2
4
620
MalasadaTech retweeted
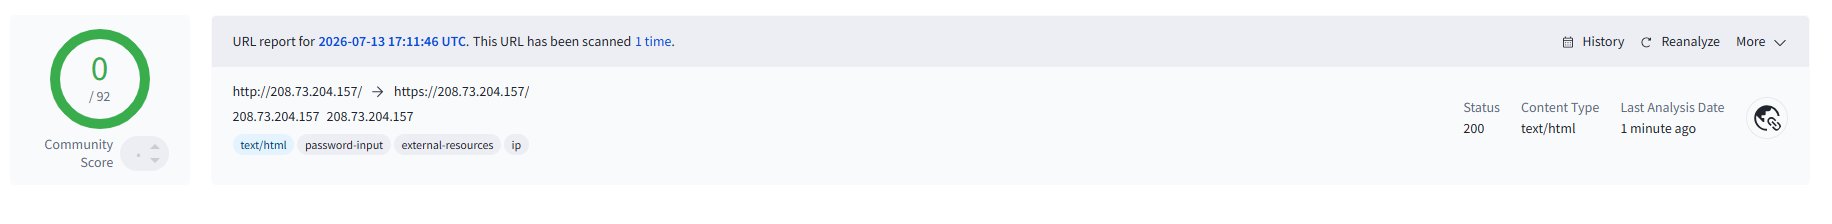
SharePoint Online "Secure Document Access" portal The phishing page impersonates a SharePoint Online "Secure Document Access" portal and targets multiple email providers: - Microsoft 365 / Outlook - Gmail - Apple iCloud - Yahoo Mail - AOL Mail - Proton Mail - Zoho Mail - Generic Webmail Testing showed it accepts arbitrary usernames/passwords, presents a fake 2FA prompt, accepts any 6-digit code, then redirects victims to the legitimate provider website after exfiltrating the data. IOCs: 208.73.204[.]157:8080 /submit.php api[.]ipify[.]org ipapi[.]co #Phishing #CredentialHarvesting @500mk500 @skocherhan @abuse_ch #zoho
2
6
23
2,250
MalasadaTech retweeted
Replying to @TheHackersNews
Great article. My YARA rule does detect some of these beyond just the original 7Zip campaign. crowdsourced_yara_rule:00f8244cec|hero_re_quest
2
4
419
MalasadaTech retweeted
#Kimsuky #DPRK🇰🇵 coalink[.]support webcamsdk-update[.]online team[.]business[.]in web02eu[.]live callsdk[.]online 144[.]172[.]110[.]53 AS14956 RouterHosting LLC 🇺🇸 @smica83 @malwrhunterteam @abuse_ch
1
4
1
14
14,312
MalasadaTech retweeted
207.174.0[.]143:8080/zoom-update.html which redirects to download executable from #dropbox which is now down hxxps://www.dropbox[.c]om/scl/fi/a0hp9g4w2ddkb3ggnkivx/Zoomupdateinstaller.msi?rlkey=rxs41my7pahnx0bfpha0zskyi&st=69oirdr0&dl=1
2
2
522
MalasadaTech retweeted
An exposed payload staging server at 207.174.0[.]143:8080 hosting multiple lure-named executables and installers (e.g., Adobe Reader, Document Viewer, System Check, Zoom Update). Open dir: 207.174.0[.]143:8080 One of the lures, zoom-update.html, impersonates a mandatory Zoom security update and automatically downloads Zoomupdateinstaller.msi from a Dropbox link. (details in comment) Analysis of one sample revealed it is a ConnectWise ScreenConnect client configured to communicate with: Domain: blog.derrspecial-onlinedmin[.]live IP: 216.227.218[.]126 This suggests the exposed directory is being used to distribute ScreenConnect-based remote access payloads, while the attacker-controlled ScreenConnect server is hosted on different infrastructure. SHA256: dc8b056dd6eb75df21e9721ac2e340f91bb5e94d5a6ff412d7d0c7539e0f06e2 433b61c29aefaa5b55fe78063e6ad8597d3835f36e1242d5402ab23e6dc61194 8e87a734daddd95322b3f18f71eb9275219e244aac4f62b8dc6da6e2e91525e9 3cd9b7d583442963261f9985128042bf45d25482efcbf903c9248837cb0d744b dd23012b4dc29cf7901185ae4fb2d507e737e9ea4d467846eafd6a86b26486bf aa84e2ac68f7fc18f4927b89be7b4a7739f2eaf099e489aa0f65c1d3913ce62a IOCs: 207.174.0[.]143 207.174.0[.]143:8080 207.174.0[.]143:8080/zoom-update.html blog.derrspecial-onlinedmin[.]live 216.227.218[.]126 #Malware #ScreenConnect #ConnectWise #opendir @malwrhunterteam @500mk500 @skocherhan @JAMESWT_WT
2
8
32
2,844
MalasadaTech retweeted
The server hosts numerous payloads and execution methods, including: - EXE - HTA - BAT - VBS - JS - SCR - CPL - COM - MSI - INF Analysis of one VBScript downloader (r.vbs) shows it: - Downloads 94.16.122[.]201:8080/a.exe - Saves it as %TEMP%\svc.exe - Executes it silently using WScript[.]Shell[.]Run IOCs: 94.16.122[.]201 Ports: 8080, 8033 02a04456bb5725fffb1afc5a47231a6362f04802a076c6230ed2bcde95c583d4 #malware #opendir @malwrhunterteam @500mk500 @skocherhan @volrant136
10
1
43
4,170
MalasadaTech retweeted
The same Google Meet site works on IP address 103.217.253[.]29:3000/call.html?code=<randomcode> #Clickfix #malware
2
3
495