
@TimHaines
🇳🇿Account based in
About this account
- Account based in
- New Zealand
- Connected via
- United States App Store
Account-level information from X, not a live location or the device used for a specific post.
Prev founded Percy, Respondly, & Favstar. Family guy who enjoys 🍦⛷ Ξ. Bug hunting for fun and profit. 👨🏼🍳
Wanaka, New Zealand
Joined April 2008
- Tweets69.8K
- Following1K
- Followers5.4K
- Likes58K






Do I know any other security researchers using paseo?
Would appreciate your opinions (and upvote?) on improving cyber refusal handling here: github.com/getpaseo/paseo/di…

Tim Haines 🇺🇦 retweeted

I took a closer look at the stealmybitcoin.com CTF, which aims to demonstrate that PHP2SHELL is not realistically exploitable. So I gave it a try.
Note: My analysis could be wrong, and I'm more than happy to be proven otherwise.
Here’s what I found:
• The server responds with Server: nginx and X-Powered-By: PHP/8.4.26.
• My differential fingerprinting scanner independently confirmed at least PHP 8.2+
• Hypotheses: I considered two possible setups:
◦ nginx → PHP-FPM
◦ nginx → Apache → PHP-FPM/mod_php
• After comparing the server's behavior against local test environments, the closest match appears to be nginx → PHP cli-server.
Plot twist: the response behavior is consistent with the PHP cli-server serving a static index.html rather than an index.php. If that's indeed the case, the challenge appears to be intentionally made unexploitable.
My conclusion (for now) is that I'm questioning whether this is a good-faith challenge.
Happy to be corrected if I've missed something!


I don’t think any of these companies will be gone by 2050. Some will need to adapt though.

1. ExxonMobil: Fusion energy makes oil obsolete.
2. GM: Robotaxis end traditional car companies.
3. Coca-Cola: Health policies ban sugary drinks.
4. Disney: AI content creators destroy studios.
5. Boeing: Urban air mobility replaces planes.
6. JPMorgan: Crypto and AI end big banks.
7. Walmart: Automated delivery kills stores.
8. Intel: Quantum computing leaves it behind.
9. Pfizer: Personalized AI drugs replace it.
10. McDonald's: Lab meat ends fast food.
Tim Haines 🇺🇦 retweeted

Example harness component using this:


lookup.disclose.io/ has become extremely useful for me recently. It tells you how to get in touch with a company's security team, based on a url, ip address, package, repo etc.
I've used it with great success to contact security teams to report issues, ask BB scope Qs, etc.

Tim Haines 🇺🇦 retweeted

We gave Moonshot’s new Kimi K3.1 Pro 100 pull requests with known vulnerabilities and one hour per PR to find them in the @BugBunny_ai VulnPR-100 benchmark.
It found 47/100 for $124.69.
That is 10 more vulnerabilities than Kimi K3 while costing $20.54 less. Cost per finding dropped from $3.93 to $2.65, a 33% improvement.
K3.1 Pro beat GPT-6 Astra and Muse Wonder 1.0, both at 46, and landed just one finding behind Claude Opus 5 while costing 3.6× less.
It still trails DeepSeek V4.1 Flash 1017, which found 54 vulnerabilities for only $7.53. That is seven more findings at roughly 16.6× lower cost.
A strong generational improvement from @Kimi_Moonshot, but DeepSeek remains the model to beat on cost-adjusted security performance.


Tim Haines 🇺🇦 retweeted

I applied to the Cyber Verification Program this morning and got rejected, I wanted to run it against my projects like urllib3 (1+ billion monthly downloads).
The entire form was very offensive-researcher focused (link a CVE with your name etc), maintainers defending aren't it.
lookup.disclose.io/ has become extremely useful for me recently. It tells you how to get in touch with a company's security team, based on a url, ip address, package, repo etc.
I've used it with great success to contact security teams to report issues, ask BB scope Qs, etc.
Tim Haines 🇺🇦 retweeted

If you don’t like people finding and disclosing vulnerabilities, you’ll really not like what happens when they *don’t* do that.
Abliterated open weight models didn’t find the PHP vulnerabilities, but if they did it would actually be an endorsement of those models.

Just life now. Picked out a farm yet?

If you're looking at an updated Node.js, and calling CVE-2026-111497 done? We have some bad news: We likely don't even know the true scale of "Node2Shell" yet.
Node patched CVE-2026-111497 on Oct 21. But the CVE wasn't in Node, it was in Brotli. So our researchers Diptendu Kar and Kurt Boberg went looking for every other package that bundles the same vulnerable Brotli decoder. Here's what we found
433 package entries across 12 ecosystems not great but the absolute worse part: Many of them don't even have fixes available yet. Now are they all reachable and exploitable? Probably not, we're finding out. But the important part: Node isn't the only affected runtime or package, not even close.
We're working through the list to manually verify each one but so far we're looking at a 71% no fix yet rate, of the fixes most are still in alpha/early releases.
The problem is most implementations aren't even called "brotli." The decoder is compiled into other runtimes like Chromium. 38 entries bundle Brotli older than 1.0.3. Some of those copies date to 2016, and of course are vulnerable to more than just this CVE. And there's no easy well to tell if you're affected.
For example, 19 are WebAssembly builds, where memory corruption exists, but stays inside the sandbox. Some require explicit configurations to enable Brotli compression and they aren't on by default. But it's not obvious unless you are looking for it and testing for it. We're going to keep validating (and producing rules), but it's going to be a rough weekend for incident responders.

Just noticed GitHub Security publishes a skill to check your report before you file it to their bounty program. Described at the bottom of bounty.github.com/report-qua….
That could make a good checkbox on the Bug Bounty Maturity Framework: bugbountymaturity.com/framew… @SteveHernandezM

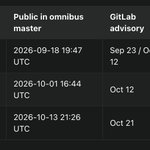
Dunno why @gitlab disclosed this without coordinating with the Ruby patches.

I recommend everyone upgrade Ruby immediately. This is a DoS and RCE vector if you accept user input into Regexp.new() ruby-lang.org/en/news/2026/1…
Tim Haines 🇺🇦 retweeted

I recommend everyone upgrade Ruby immediately. This is a DoS and RCE vector if you accept user input into Regexp.new() ruby-lang.org/en/news/2026/1…
Becoming adept at using a weeks worth of tokens in a day. Thanks @thsottiaux.

Tim Haines 🇺🇦 retweeted

Thanks a lot to @TimHaines for performing a security audit of Rack Gateway: github.com/DocSpring/rack-ga…
I've been working hard on this project and I've been trying to make it as secure as possible, but Tim was able to find a huge number of things that I had missed.

Interesting facets coming out of the PHP foundation's reports about Mythos and Daybreak Red not finding the bugs disclosed this week.

wait, PHP was actually scanned by Anthropic’s Claude Mythos earlier this year. they also had access to OpenAI’s Daybreak Red for validating exploits.
the PHP Foundation revealed this JUST yesterday.
keeping frontier cyber models in the hands of a selected few doesn’t seem to be working well for the internet.
thephp.foundation/blog/2026/…
